
AiSOC
Open-source, self-hostable AI Security Operations Center that ingests telemetry, detects threats, and investigates them with auditable AI agents.
At a Glance
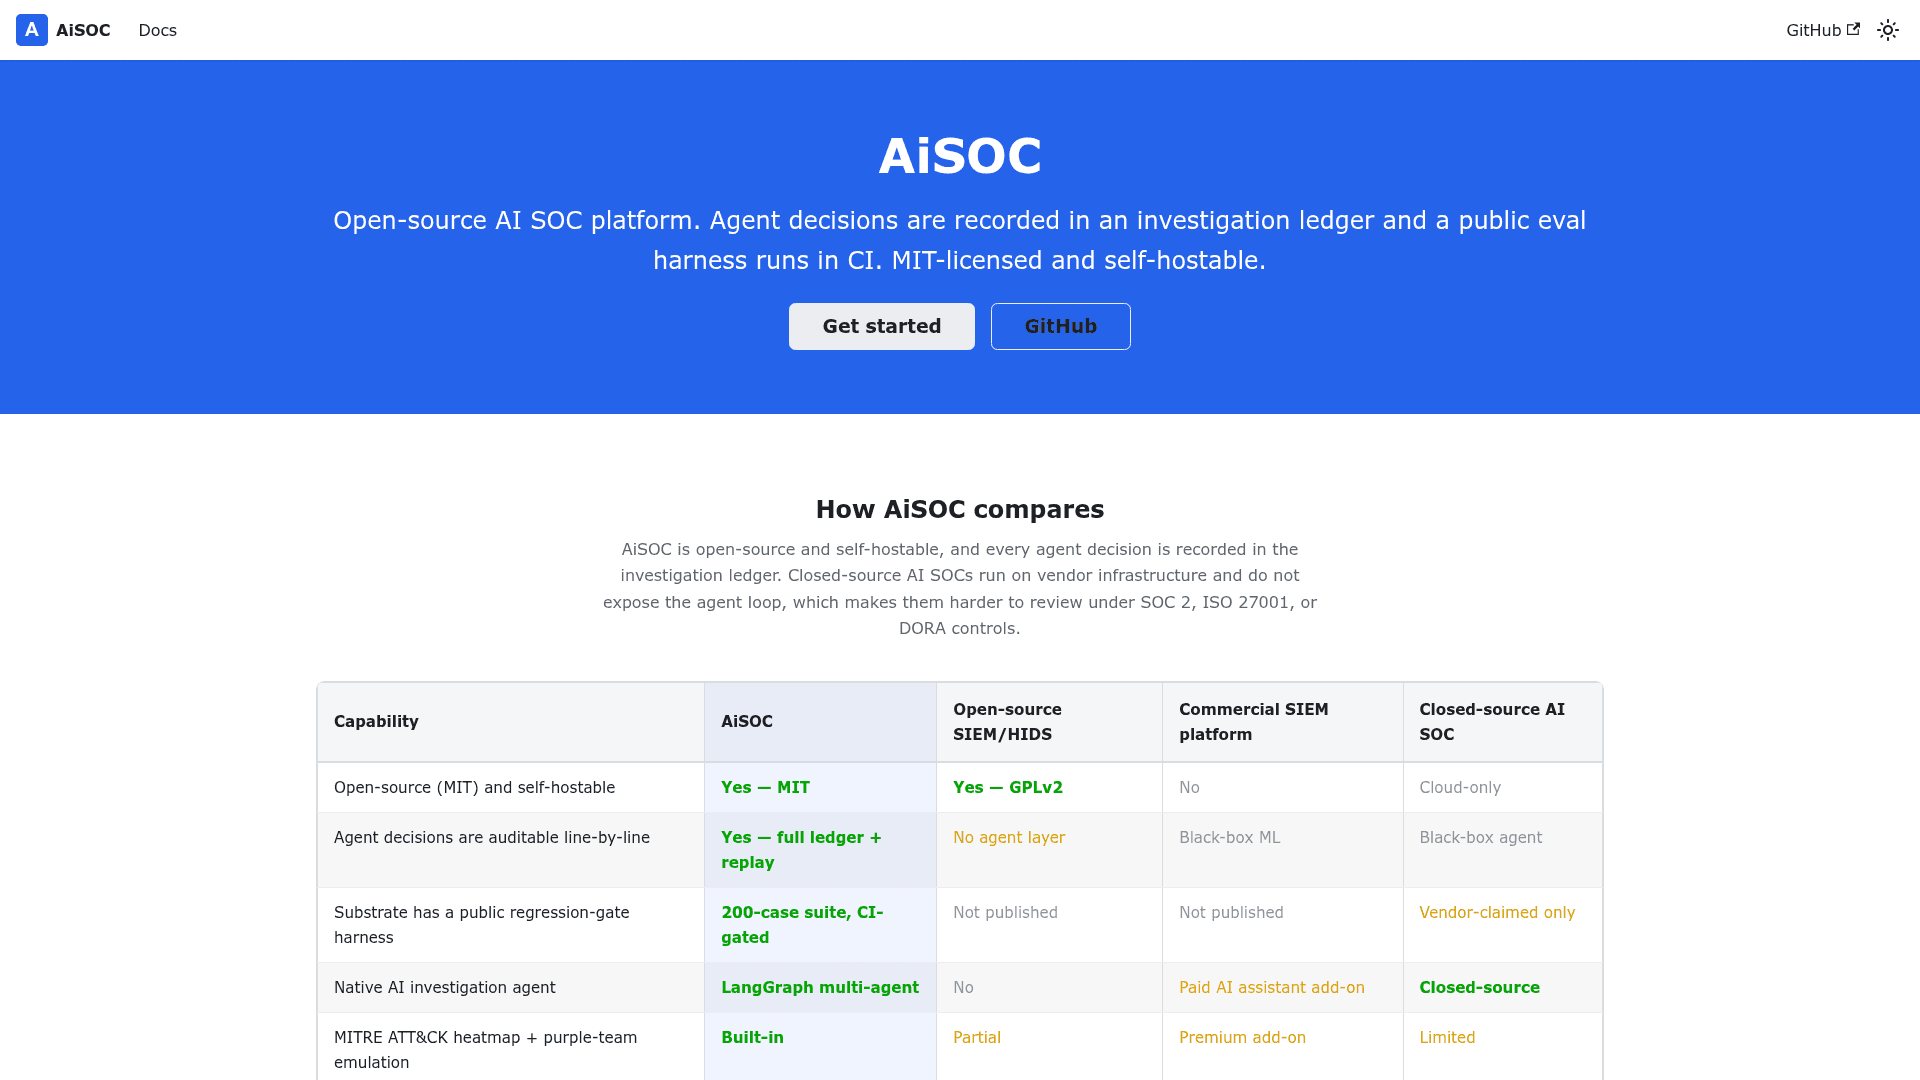
MIT-licensed, self-hostable AI Security Operations Center; no Cyble-only features, no gated modules, no telemetry.
Engagement
Available On
Alternatives
Listed Nov 2026
About AiSOC
AiSOC is an open-source, MIT-licensed AI Security Operations Center developed by contributors in the beenuar/AiSOC repository, with development funded and supported by Cyble according to the project site. It ingests security telemetry, runs detection rules, groups alerts into incidents, and uses AI agents to investigate each one while recording every prompt and tool call. Latest release listed is v21.0.0.
What It Is
AiSOC is a self-hostable security operations platform covering ingest, detection, correlation, investigation, and response. Telemetry is normalized, passed through Kafka, and evaluated against the project's rule library (the README cites 2966 executable rules of 7407 on disk). Related alerts are correlated into incidents, and an agent investigates and writes its reasoning to an Investigation Ledger. Proposed response actions require human approval unless a tenant has explicitly granted autonomy for a given action.
How the Investigation Workflow Works
Agents read the alert, correlated alerts, entity context, and prior verdicts, then call typed tools such as lake queries, graph traversals, and enrichment lookups. Prompts, tool calls, citations, verdicts, and token cost are logged and can be exported as a signed evidence bundle. Playbooks preview their plan before acting, and approval steps are durable pauses that survive restarts. The project also describes retro-hunting when new threat intelligence arrives, a LangGraph multi-agent orchestrator, UEBA, honeytokens, purple-team emulation with an ATT&CK heatmap, and compliance dashboards.
Setup and Deployment
The quick start is cloning the repo and running make up, which generates secrets, creates an administrator, and starts the stack. Install scripts exist for Windows, Linux, and macOS, and a pip-installable sandbox demo runs without Docker. The README lists 8 GB memory and 20 GB free disk for the Docker VM. A bundled local model (llama3.2 3B quantized via Ollama) serves triage by default, with options for GPU, a host LLM, or your own provider. Core, full, and demo profiles are available, with Helm charts and Docker Compose.
Connectors and Extensibility
The README lists 91 data connectors, including Splunk, Sentinel, Elastic, CrowdStrike, Okta, AWS, and Kubernetes audit, plus collectors for CloudTrail, GCP Pub/Sub, Azure Event Hubs, and syslog/CEF. A migration package translates Splunk SPL, Sentinel KQL, and Elastic EQL rules, refusing what it cannot carry. Plugin SDKs and an MCP server are described.
Stated Limits
The README says AiSOC is not a drop-in SIEM replacement, cannot see telemetry that has not been connected, and is not autonomous by default. It also notes no hosted LLM provider has been exercised in its testing.
Community Discussions
Be the first to start a conversation about AiSOC
Share your experience with AiSOC, ask questions, or help others learn from your insights.
Pricing
Open Source (Self-hosted)
MIT-licensed, self-hostable AI Security Operations Center; no Cyble-only features, no gated modules, no telemetry.
- MIT License (OSI-approved)
- Self-hostable via Docker Compose and Helm
- Runs with no API keys using a bundled local model
- No CLA, no telemetry, no calls home
- Optional external LLM provider costs are borne by the operator (BYOK)
Capabilities
Key Features
- Auditable Investigation Ledger of prompts, tool calls, and verdicts
- Signed evidence bundle export
- LangGraph multi-agent investigation
- Alert fusion and correlation into incidents
- Sigma, YARA, KQL/EQL detection engineering
- Playbook engine with human approval steps
- UEBA anomaly scoring
- Honeytokens
- Purple team emulation and MITRE ATT&CK heatmap
- Attack graph with Neo4j
- 91 data connectors and cloud collectors
- Detection rule migration from Splunk, Sentinel, and Elastic
- SAML/OIDC SSO, SCIM, MFA, RBAC, multi-tenancy
- Compliance dashboards (SOC 2, ISO 27001, NIST CSF, PCI-DSS, HIPAA, DORA)
- Plugin SDKs and community marketplace
- Bundled local LLM for CPU inference
- MCP server
- Helm and Docker Compose deployment