
Drata
Agentic trust management platform that automates compliance, internal and third-party risk management, and customer assurance.
At a Glance
About Drata
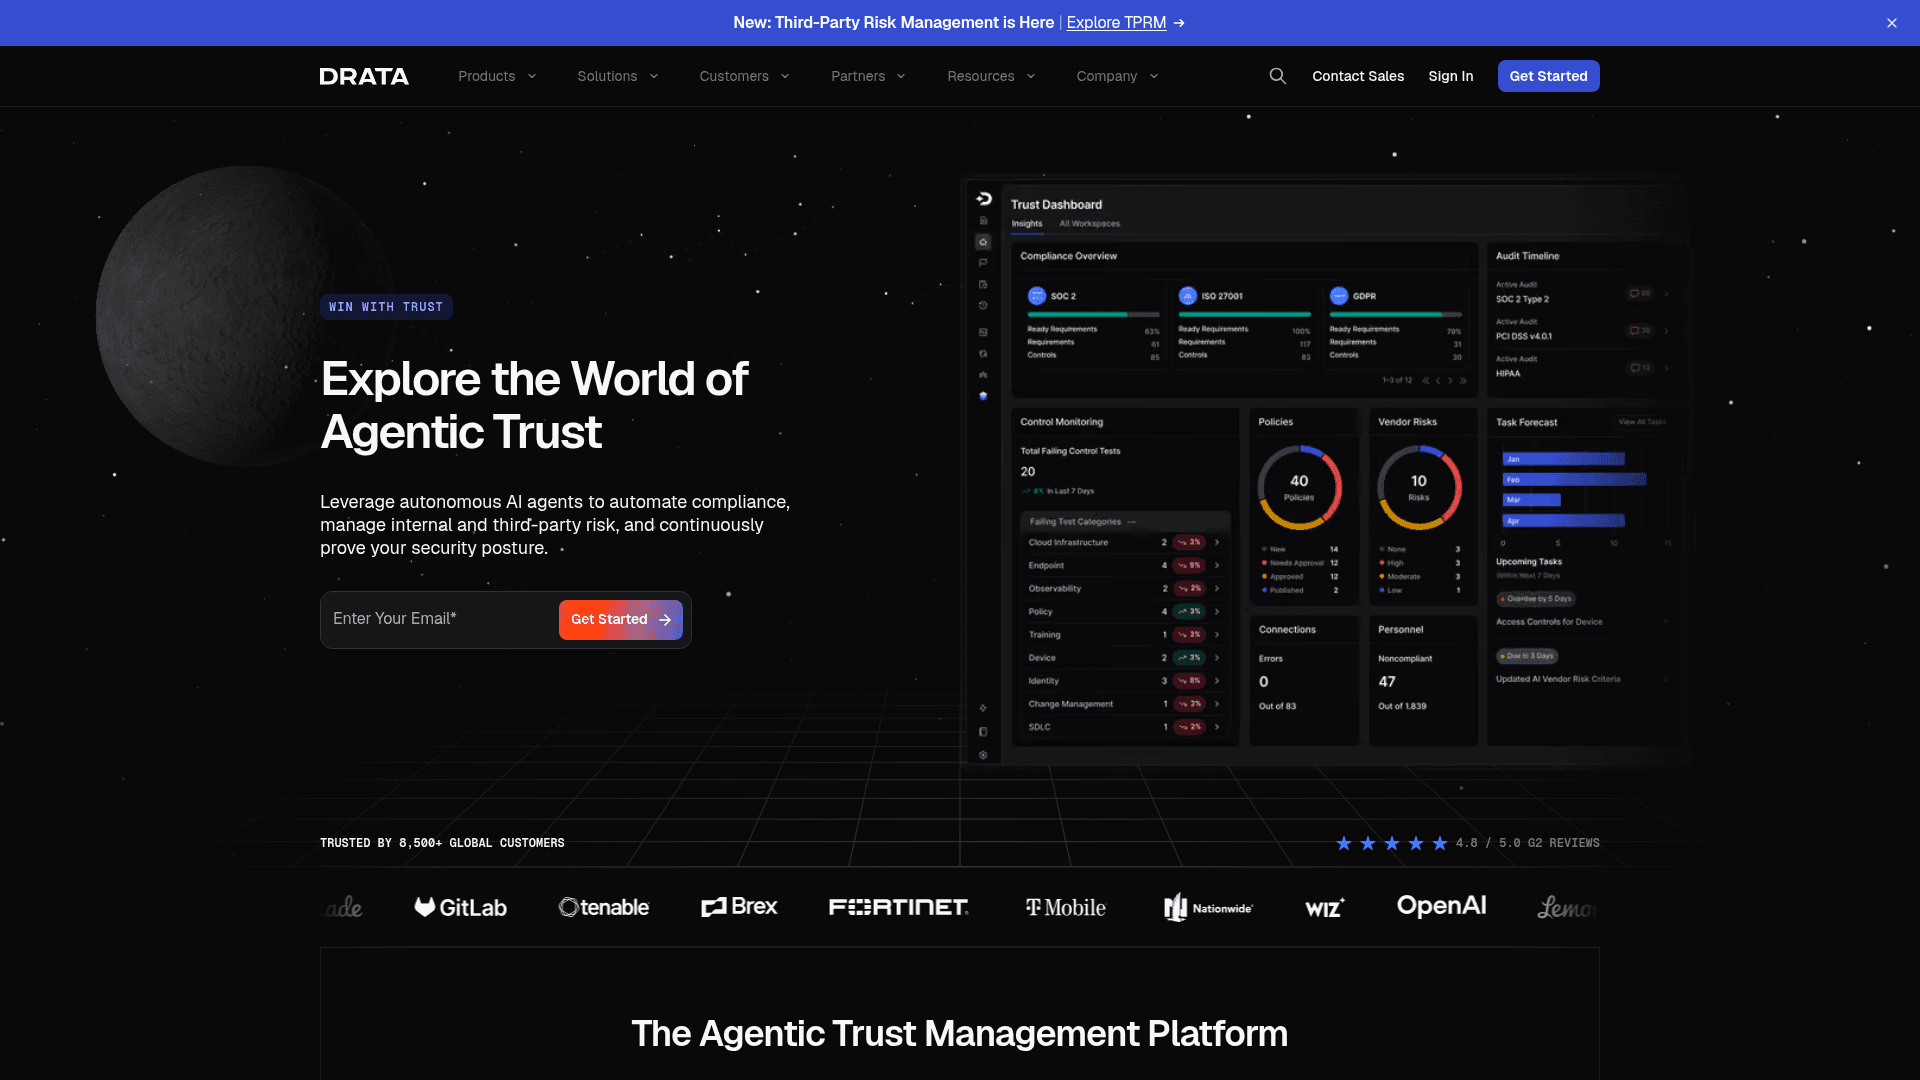
Drata is a trust management platform from Drata Inc. that combines governance, risk, compliance, and customer assurance in one system. It uses AI agents to automate evidence collection, control monitoring, questionnaire responses, and vendor risk assessments.
What It Is
Drata is a GRC (governance, risk, and compliance) and trust management platform. It brings controls, risks, policies, and evidence together so teams can map controls once and reuse them across multiple frameworks, including SOC 2, ISO 27001, ISO 42001, GDPR, HIPAA, and PCI DSS, plus custom frameworks.
The product lineup covers Enterprise GRC, Compliance Automation, Trust Center, AI Questionnaire Assistance, Third-Party Risk Management, and AI Agent Governance.
How the Workflow Operates
- Compliance Automation collects evidence automatically and monitors controls continuously, with guided remediation.
- The Trust Center gives prospects and customers a self-serve place to review security posture, request documents, and get answers.
- AI Questionnaire Assistance drafts answers from a Knowledge Base of approved trust content.
- Third-Party Risk Management uses AI agents to build criteria from existing questionnaires, collect documents from Trust Centers, run assessments, and follow up with vendors.
AI Agent Governance
Drata describes a newly announced product, listed as limited availability, that discovers AI agents running in an environment, enforces policy before an action executes, and produces auditor-grade records of decisions.
Company Background
Drata was founded in 2020 by Adam Markowitz, Troy Markowitz, and Daniel Marashlian, and has offices in San Francisco, New York, San Diego, London, and Sydney. Drata's site says it is trusted by 8,500+ global customers; this is a vendor claim.
Community Discussions
Be the first to start a conversation about Drata
Share your experience with Drata, ask questions, or help others learn from your insights.
Pricing
Foundation
Compliance Automation tier: launch your program with everything you need for liftoff. Pricing not published; request a demo.
- Up to 50 FTEs
- 1 Pre-Mapped Framework (limited to SOC 2, ISO 27001, Cyber Essentials, HIPAA, and GDPR)
- Pre-Built Integrations
- Trust Center Standard
- AI Questionnaire Assistance Standard
- Risk Management
- Custom Controls
- Compliance as Code
- Open API Access
- Add-Ons: Additional Frameworks, User Access Review
Advanced
Compliance Automation tier: build a scalable GRC program designed to grow with your fleet. Pricing not published; request a demo.
- Everything in Foundation
- Any Available Framework
- Custom Connections and Tests
- Custom Fields and Formulas
- Add-Ons: Additional Frameworks, User Access Review, Risk Management Pro, Workspaces, Custom Frameworks
Enterprise
Compliance Automation tier: proactively optimize and keep your mature GRC program mission-ready. Pricing not published; contact sales.
- Everything in Advanced
- Risk Management Pro
- Compliance as Code Pro
- User Access Review
- Add-Ons: Additional Frameworks, Workspaces, Additional Custom Tests, Custom Frameworks, Agentic TPRM Assessment
Capabilities
Key Features
- Continuous control monitoring
- Automated evidence collection
- Multi-framework control mapping
- Enterprise GRC
- Trust Center
- AI questionnaire automation
- Agentic third-party risk management
- AI agent governance
- Guided remediation
- Integrations with tech stack tools