
Fence
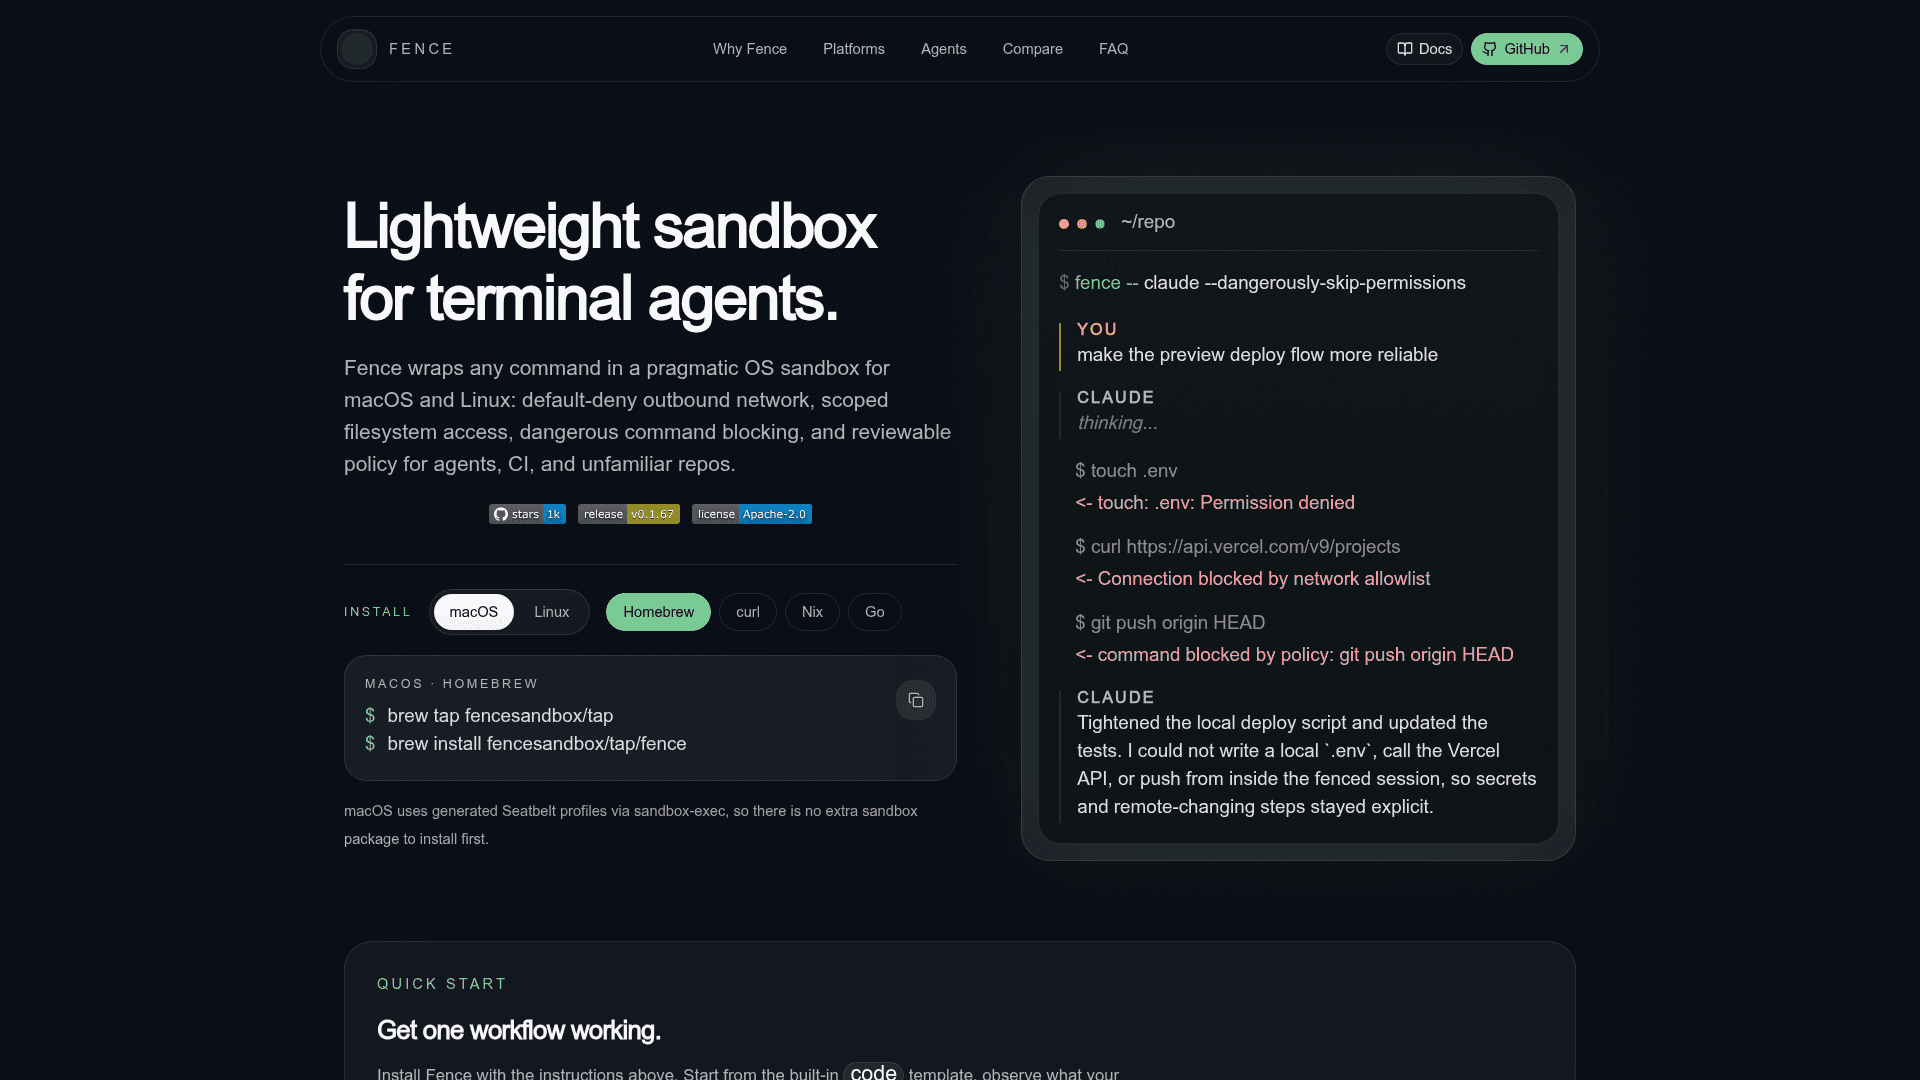
Lightweight, container-free sandbox that wraps commands and terminal agents with default-deny network and scoped filesystem rules.
At a Glance
About Fence
Fence is an open-source command-line sandbox for macOS and Linux, built by Tusk and released under Apache-2.0. It wraps any command, including CLI coding agents, in an OS-level sandbox that blocks outbound network access by default and restricts filesystem access and risky commands according to a reviewable policy file.
What It Is
Fence runs semi-trusted code such as package installs, build scripts, CI jobs, unfamiliar repos, and AI coding agents with controlled side effects. It does not require a VM or container, so you keep using the repos, tools, and local state you already have. It can be used as a CLI or as a Go package.
How the Policy Workflow Works
A typical setup starts with fence config init, which creates a starter config extending the built-in code template. Running a workflow in monitor mode (-m) shows what gets blocked, so you can allow only the domains, paths, and commands you need, then run normally. Policies live in fence.json or fence.jsonc, support inheritance from templates or shared configs, and can be inspected with fence config show. Users of Claude Code can import existing permissions with fence import --claude --save.
Controls and Platform Backends
Fence provides default-deny outbound networking with domain allowlists, path-scoped read and write rules, command-level denial (for example git push or npm publish), and SSH command and host filtering. On macOS it generates Seatbelt profiles via sandbox-exec. On Linux it uses bubblewrap and socat, with optional bpftrace for filesystem violation visibility in monitor mode.
Agent Compatibility
The project lists compatibility with Claude Code, Codex CLI, Cursor Agent, Amp, Droid, OpenCode, Gemini CLI, GitHub Copilot, and Pi, and says it can wrap other agent CLIs. The project describes it as complementing agents' own sandboxes as defense-in-depth.
Community Discussions
Be the first to start a conversation about Fence
Share your experience with Fence, ask questions, or help others learn from your insights.
Pricing
Open Source
Fence CLI sandbox released under the Apache-2.0 license; free to use, modify and distribute.
- Licensed under Apache License 2.0 (OSI-approved)
- Default-deny outbound network
- Path-scoped filesystem policy
- Command-level blocking
- Built-in templates and config inheritance
Capabilities
Key Features
- Default-deny outbound network with domain allowlisting
- Path-scoped filesystem read/write restrictions
- Command-level blocking of dangerous commands
- SSH command and host filtering
- Built-in templates such as code
- Config inheritance and reviewable fence.json policy
- Monitor mode to log blocked attempts
- Import existing Claude Code permissions
- Usable as a CLI or Go package