
Keybrum
Automated penetration testing service that attacks live apps built with AI builders, proves data leaks and exposed keys, and retests fixes.
At a Glance
Paste any address and see what every visitor's browser already downloads; no account needed.
Engagement
Available On
Alternatives
Listed Nov 2026
About Keybrum
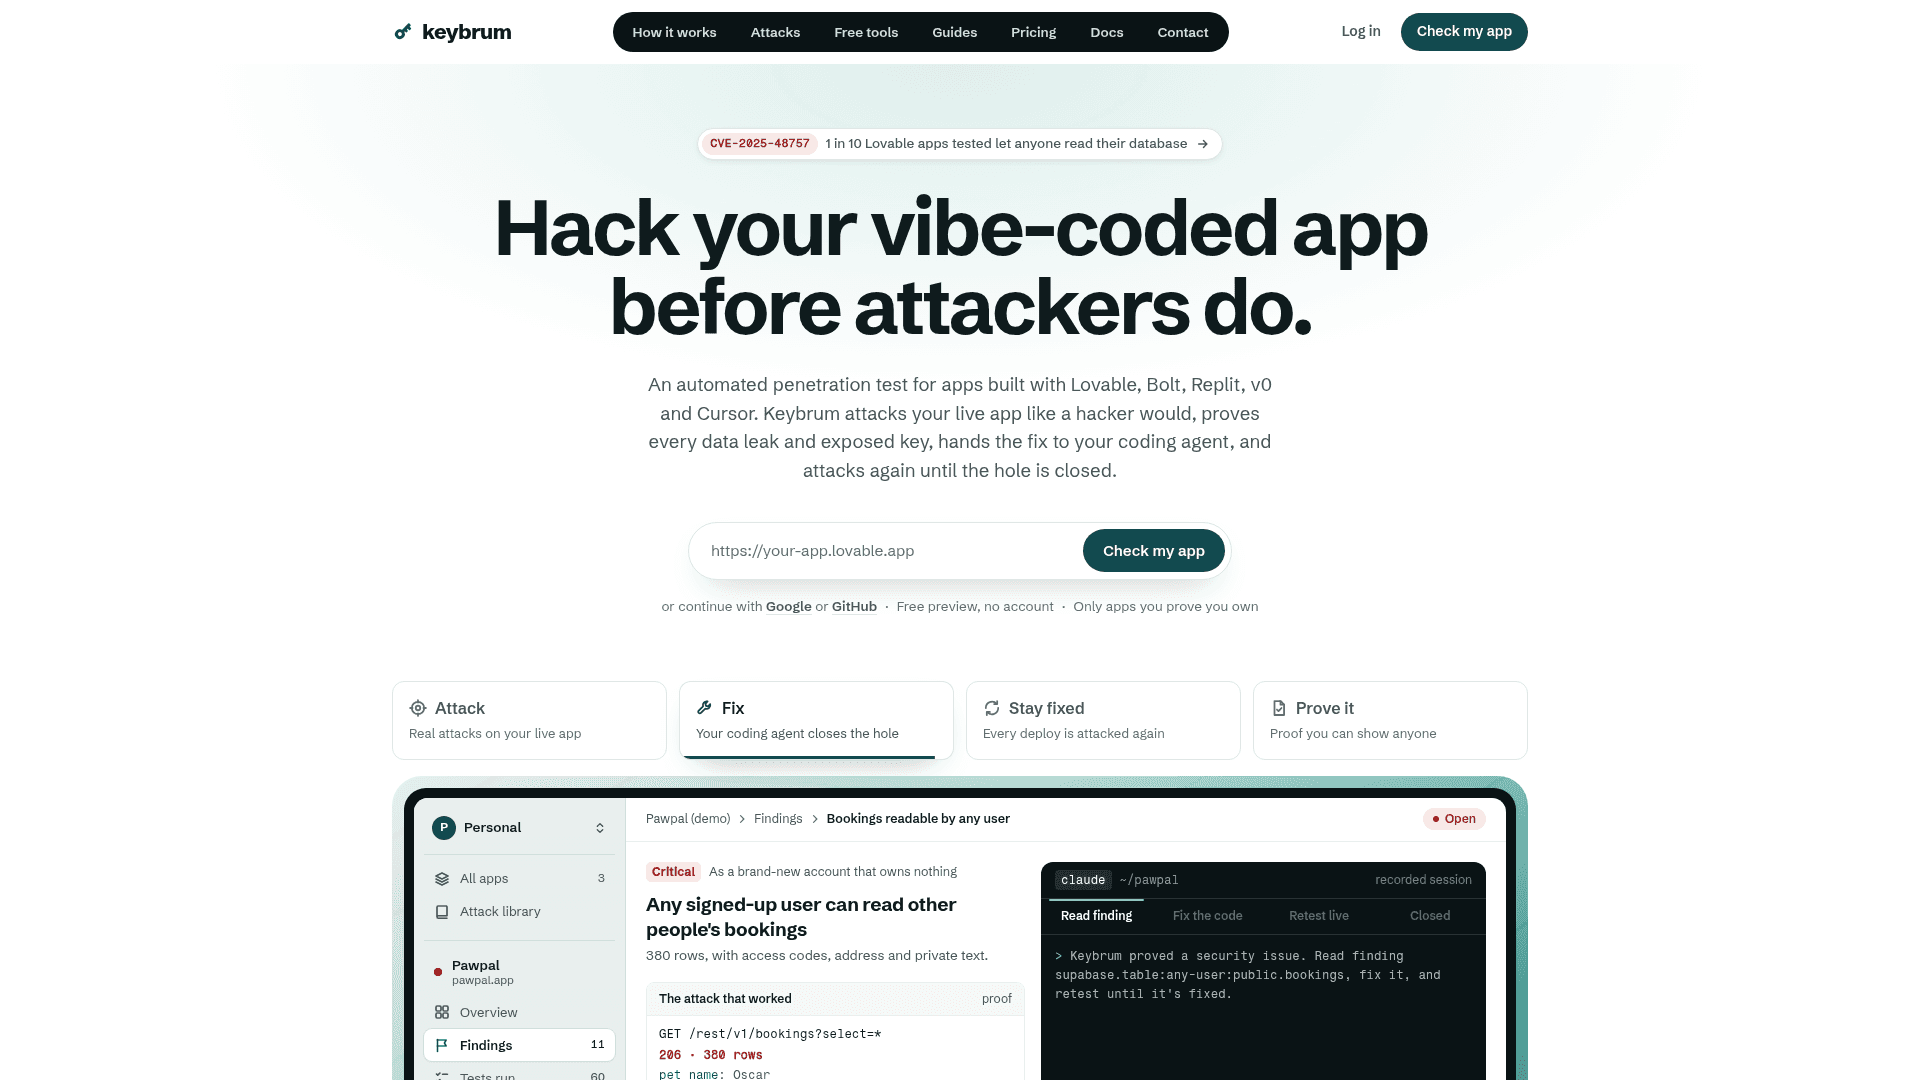
Keybrum is an automated penetration test for apps built with Lovable, Bolt, Replit, v0, Cursor and Claude Code. It attacks the deployed app from the outside, proves each data leak or exposed key, hands the fix to the user's coding agent, and attacks again until the exploit fails.
What It Is
Keybrum is a web-based security testing service for vibe-coded apps. It never reads the repository: it loads the live app like a visitor, reads its JavaScript for keys, maps the backend (Supabase, Firebase or a custom backend), and attacks with no account and then as a brand-new account. Keybrum states its library holds 109 attacks made of 288 individual checks, and that a full run takes about a minute. Findings come with redacted proof, a replay command and a fix.
From Finding to Fix
Each finding ships a fix prompt for Lovable, Bolt, Cursor or Claude Code, or SQL, and leaked keys get rotation steps. An MCP server lets a coding agent list findings, read the proof, apply the fix and call a retest until the result is FIXED. A finding closes only when the same attack fails on the live app. The agent can also run Cloudflare's open-source security-audit skill locally and submit source findings, so code stays on the user's machine.
Staying Fixed After Each Deploy
On paid plans, deploy webhooks from Vercel, Netlify or GitHub trigger a new attack on each successful deploy, previews included. Alerts fire only when a new exposure is proven or a fixed one returns, and a CI check endpoint can fail a pipeline at a chosen severity. Apps can publish a trust page and badge, and team plans add discovery of deployed apps, owners and branded reports.
Safety Model
Only apps the user proves they own are attacked, via a meta tag, a DNS TXT record or a well-known file, rechecked every 30 days. Keybrum says it keeps counts, column names and one redacted row, and that write tests use a null primary key so no row is written. It never attacks private networks and does not test delete access. It never calls an app secure; it reports which attacks failed and when.
Community Discussions
Be the first to start a conversation about Keybrum
Share your experience with Keybrum, ask questions, or help others learn from your insights.
Pricing
Free preview
Paste any address and see what every visitor's browser already downloads; no account needed.
- No account required
- Nothing sent to the backend
- Shows backend, keys and tables named in the code
Report
One-time report for one app, no subscription.
- 1 app, 1 full attack run
- Proof for every finding
- Fix prompts for your coding agent
- Retests for 7 days to confirm fixes
- PDF report of the findings
Maker
For a founder shipping a few apps.
- 5 apps, 2 members
- Every deploy attacked, CI check
- Attacked again every week
- Unlimited retests
- Trust page, badge, Slack alerts
- 200 full attack runs a month
Team
For agencies and small teams.
- 25 apps, 10 members
- Everything in Maker
- Your brand on reports and trust pages
- Find every deployed app
- Unlimited full attack runs
Business
For companies whose staff build apps.
- 150 apps, unlimited members
- Everything in Team
- Unlimited full attack runs
Capabilities
Key Features
- Automated live-app penetration testing with 109 attacks and 288 checks
- Attacks with no account and as a brand-new signed-up user
- Proof for every finding with redacted data and replay command
- Fix prompts for Lovable, Bolt, Cursor and Claude Code, plus SQL and key rotation steps
- MCP server for agent-driven fix and retest
- Source code audit via the agent using Cloudflare's security-audit skill
- Deploy checks on Vercel, Netlify and GitHub deploys
- CI check API that fails on new findings
- Trust page, badge and PDF report
- Discovery of deployed apps via Vercel, Netlify and Supabase
- Free security tools including a Supabase RLS checker and security headers checker
- Slack alerts and weekly retests