Knostic
Security platform that discovers, monitors and enforces policy on AI agents, coding assistants and their supply chain at the endpoint.
At a Glance
For individual developers / small teams (1 - 5 users)
14-day free trial of Team and Enterprise plans
Engagement
Available On
Alternatives
Listed Oct 2026
About Knostic
Knostic builds security software for agentic AI workflows, covering coding assistants such as Cursor, Claude Code, GitHub Copilot and Windsurf, as well as Claude Cowork. Its products are Kirin, an endpoint security layer for agents, and AgentMesh, threat intelligence for skills, MCP servers and extensions. Knostic also publishes the open-source OpenAnt vulnerability scanner.
What It Is
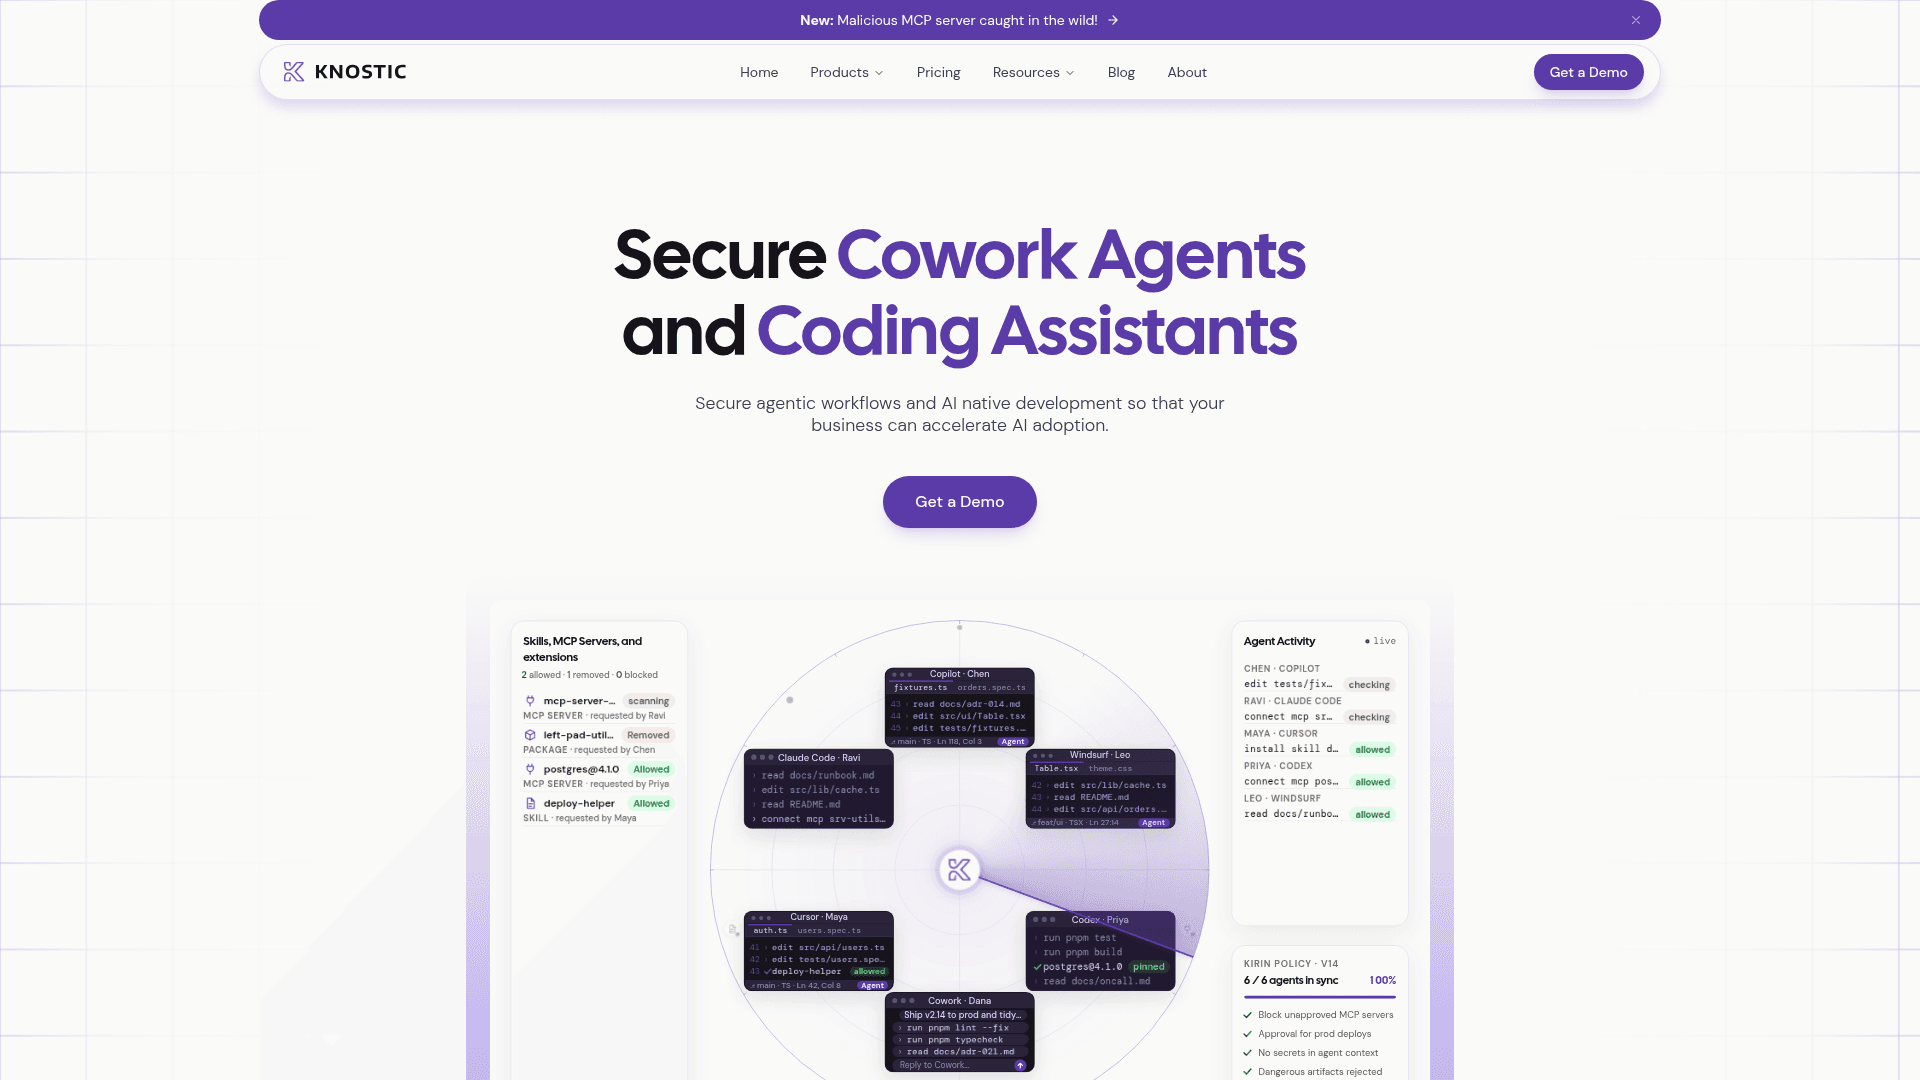
Knostic is an agentic-endpoint security platform. Instead of asking a model to behave, it checks each agent action against a central policy before the action runs. Allowed actions proceed, while risky ones are blocked or routed to a human for review. The same policy applies across the different agents a team uses.
How Kirin Works
Kirin installs as a user-space client (no admin rights required) and, for Cursor and VS Code, as an extension. Policies run in Off, Monitor or Enforce modes. In Enforce mode, Kirin can block a read of secret files or sanitize secrets before they reach the model. It quarantines unverified MCP servers for admin review and enforces allow/block lists for extensions. Kirin also provides shadow AI discovery of local LLMs, browser chatbots and unsanctioned APIs, along with centralized policy management. According to the FAQ, supported agents are Claude Code CLI, Claude Desktop and Cowork, Cursor, Windsurf, and VS Code with GitHub Copilot, on macOS and Windows, with Linux in beta.
AgentMesh and the Agentic Supply Chain
AgentMesh continuously discovers and scans agent skills, MCP servers and VS Code extensions. It returns dangerous, risky or clean verdicts, supports lookup by SHA-256, and offers a REST API. Knostic's research blog reports findings on malicious VS Code extensions and MCP packages.
AI SDLC and Generated Code
Knostic describes detecting hallucinated and vulnerable packages, enforcing secure coding rules including automatic threat modeling, and discovering vulnerabilities and generating patches. The FAQ says audit logs and SIEM, Slack and Teams integrations are available on higher tiers, with Enterprise SSO.
Community Discussions
Be the first to start a conversation about Knostic
Share your experience with Knostic, ask questions, or help others learn from your insights.
Pricing
Kirin Free
For individual developers / small teams (1 - 5 users)
- Continuous scanning across projects
- Granular policies control
- Configuration enforcement
- Extensions scanning
- Rules and Generated Code scanning
Kirin Team/Enterprise Free trial
14-day free trial of Team and Enterprise plans
AgentMesh Free
No time limit · login required
- 300 items per category (fixed set)
- Web UI + limited API access
Kirin Team
For growing teams (5+ users)
- Includes everything in Free
- Unified dashboard
- Organizational policy
- Role-based access control
- Audit logs
- Cross-org MCP, rules, hooks visibility
- Priority support
- Advanced contextual detection: add-on
Kirin Enterprise
For engineering managers (10+ users)
- Includes everything in Team
- Policy groups
- Advanced contextual detections (add-on included)
- Enterprise SSO
- Integrations (SIEM, Slack)
- Compliance Ready Reporting
- Dedicated enterprise support
AgentMesh Premium
Full catalog · Kirin included
- Full catalog - all categories
- Up to 300 API calls per month (20/day)
- Kirin IDE security included
AgentMesh Pro
Unlimited API · Kirin included
- Full catalog - all categories
- Unlimited API access
- Kirin IDE security included
Capabilities
Key Features
- Shadow AI discovery
- Inline policy enforcement for agent actions
- Secrets leakage blocking
- MCP server quarantine and review
- Extension allow/block lists
- Centralized security posture management
- Agentic supply chain scanning
- SHA-256 artifact lookup
- Hallucinated and vulnerable package detection
- Automatic threat modeling for AI-generated code
- Audit logs and SIEM integration