
Offense
Security tools that coding agents can discover, call and verify through CLI, MCP and HTTP, returning structured security evidence.
At a Glance
Apache-2.0 licensed open-source core with CLI, MCP and HTTP interfaces; local dependency engine runs on your machine with no Offense usage charge.
Engagement
Available On
Listed Nov 2026
About Offense
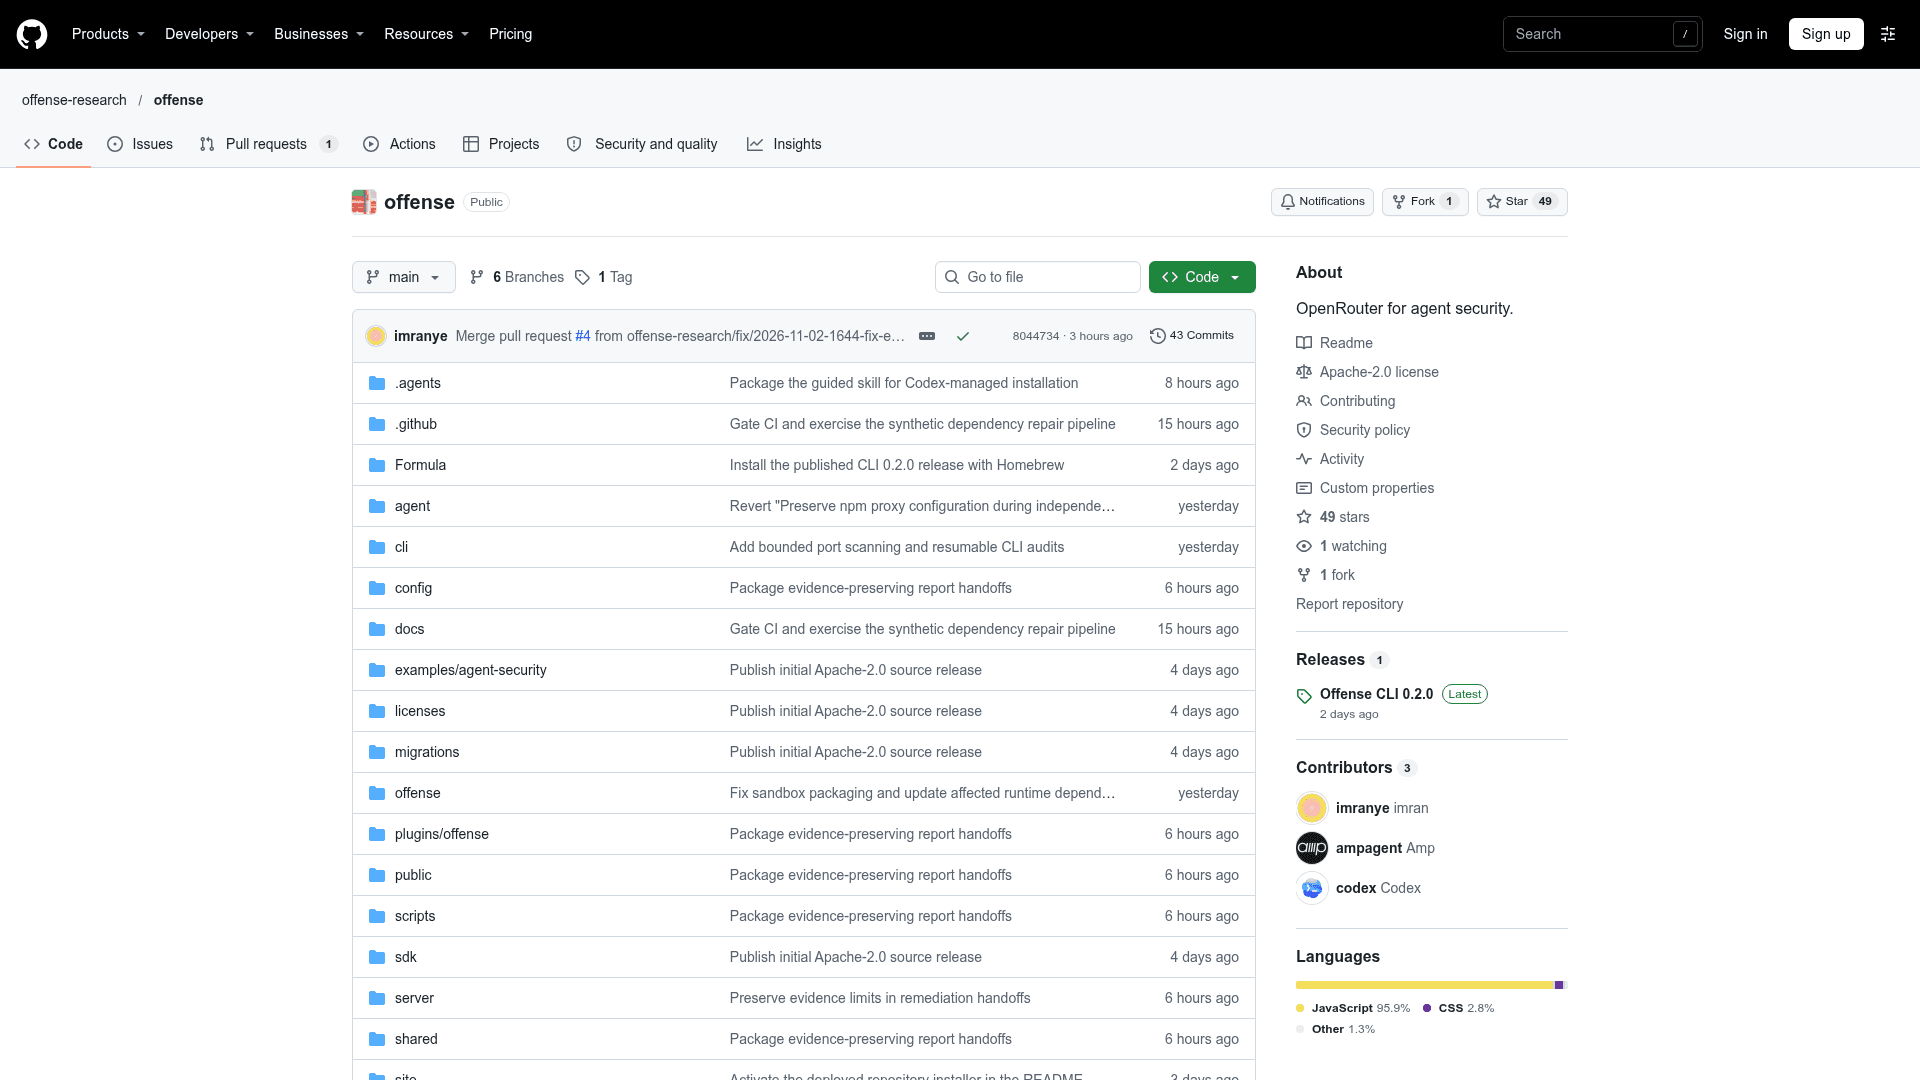
Offense is a product of Offense Research, Inc. that gives coding agents security tools for auditing dependencies, inspecting source and GitHub Actions workflows, and testing proposed fixes. It returns structured evidence through a CLI, MCP and an HTTP API, and the agent uses its own model, repository access and permissions to act on it. The code is open source under Apache-2.0, with optional paid hosting and a self-hostable platform.
What It Is
Offense is a security toolkit for AI coding agents such as Codex, Claude Code, Pi, Hermes and Crush. It does not run its own agent or require a model-provider key. Instead it produces evidence such as advisory matches, scanner findings, coverage warnings and remediation prompts, and the agent investigates and edits code within the scope the user authorizes. The README states that a finding is not a confirmed exploit and that a partial scan is not a clean bill of health.
How the Workflow Runs
The documented flow runs from discovery to assessment, investigation, fix and verification. A local engine previews supported npm and pnpm lockfiles, then queries OSV and npm metadata. It writes scan.json and a remediation.md for the agent. The agent traces real usage, tests upgrades in isolation and rescans the changed inputs. A preview mode makes no network calls, and uploads, paid calls and code edits need separate approval. Saved hosted audits or job receipts can also be exported as a local PDF report.
Execution Modes
Three modes are documented. The local dependency engine needs Node.js 24+ and npm. The self-hosted platform needs Linux amd64, Node.js 24+, Git and Docker, and runs dependency audits plus Opengrep and Zizmor in isolated containers with Offense billing disabled. The hosted service offers managed execution through an Offense account. A starter GitHub Actions workflow can add pull-request dependency audits via an installation PR.
Agent Integration
A portable Agent Skill, scanning-with-offense, teaches compatible agents the preview, approval and verification workflow. The README lists project skill directories for agents including Pi, OMP, Hermes, Codex, Claude Code, Crush, Cursor, OpenCode, Copilot and Gemini CLI. A local stdio MCP server exposes offense.audit_dependencies, and a Codex plugin is built from the same skill and CLI. The CLI can be installed through Homebrew, a GitHub release archive, or npm-style commands.
Community Discussions
Be the first to start a conversation about Offense
Share your experience with Offense, ask questions, or help others learn from your insights.
Pricing
Open Source (Self-hosted)
Apache-2.0 licensed open-source core with CLI, MCP and HTTP interfaces; local dependency engine runs on your machine with no Offense usage charge.
- Apache License 2.0
- Local dependency engine: Node.js 24+, npm; no Docker or Offense account for dependency analysis
- Self-hosted platform available
- Free npm/pnpm dependency audits on pull requests via starter GitHub Actions workflow
- Optional paid hosting is separate; prices not published in supplied evidence
Capabilities
Key Features
- Dependency audits of npm and pnpm lockfiles using OSV advisories
- Structured scan.json output and remediation.md for coding agents
- Offline preview of dependency inputs before any network call
- Source and GitHub Actions workflow scanning with Opengrep and Zizmor in the self-hosted profile
- CLI, MCP and HTTP interfaces
- Local stdio MCP tool offense.audit_dependencies
- Portable scanning-with-offense Agent Skill
- Offline PDF export of saved hosted audit or job reports
- Installation PR that adds read-only dependency audits to GitHub Actions
- Self-hosted platform with isolated Docker scanners
- Local TCP port exposure preview (unreleased)
- Tool catalog discovery with coverage and quotes