
prowler agent
Self-hosted workspace for reviewing Prowler-compatible Google Cloud security findings with triage, compliance mapping, reports and audit trail.
At a Glance
Self-hosted workspace for reviewing Google Cloud security findings, licensed under Apache 2.0. Early-stage; supplied Docker Compose setup is for trusted local development only.
Engagement
Available On
Alternatives
Listed Oct 2026
About prowler agent
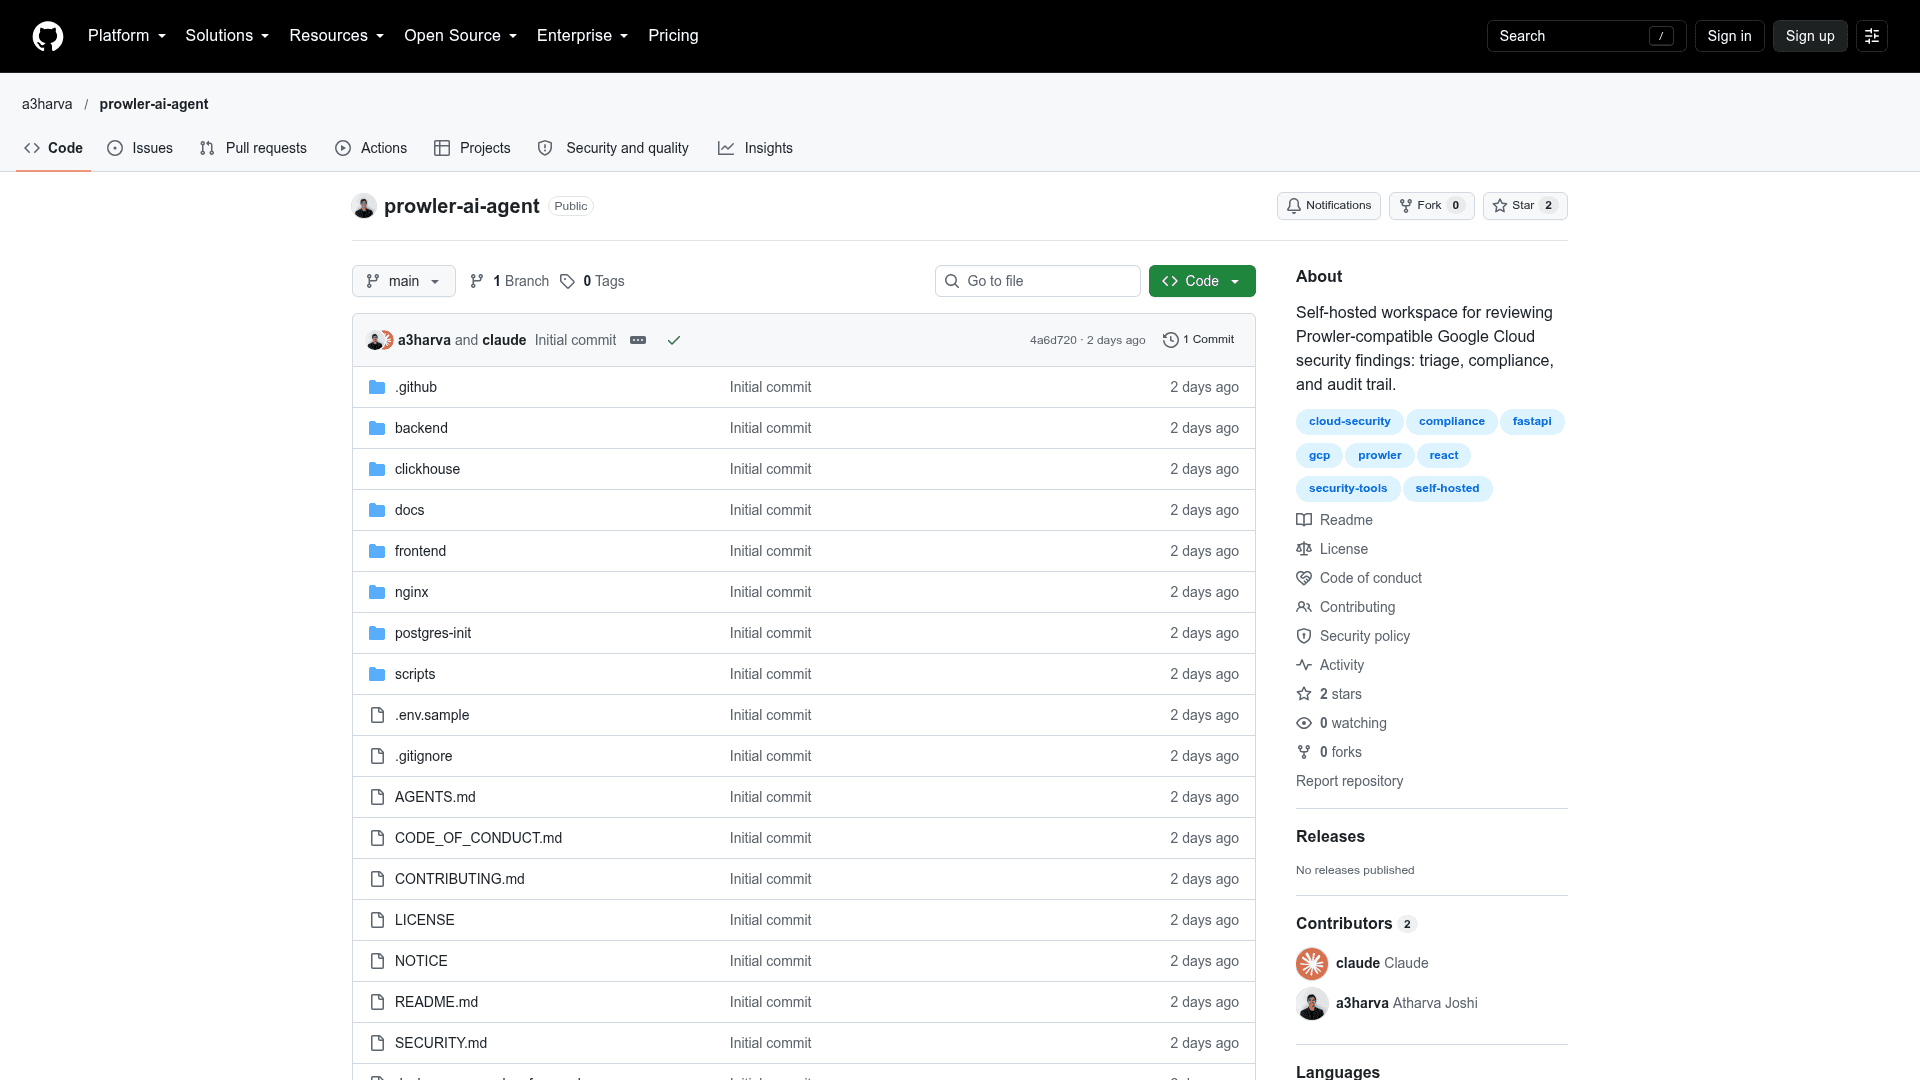
prowler agent is a self-hosted workspace, published by the GitHub user a3harva, for reviewing Google Cloud security findings from Prowler-compatible scans. It pairs a React review console with a FastAPI API and background workers. The project is labeled early-stage, and its Docker Compose setup is documented for trusted local development only.
What It Is
The tool collects Prowler GCP scan results in one place so security teams can turn a scan snapshot into a repeatable review process. Operators onboard GCP organizations and projects, record the service account used for scan impersonation, and either run Prowler GCP scans or import their CSV, OCSF JSON, HTML and compliance exports. It is not an autonomous remediation tool, and it does not replace validating scanner output or cloud permissions.
Review workflow
Findings can be filtered, assigned, annotated and muted with a reason, using department-scoped Editor and Admin access. Review decisions are preserved across later scans. Findings are rolled up by the compliance frameworks present in the scanner's exports, and PDF assessment reports can be rendered. An audit log records every mutation and attributes it to a user.
Architecture and optional integrations
A React browser app sits behind nginx and talks to a FastAPI service backed by PostgreSQL. Redis and Celery workers run the Prowler scan container and report jobs, and the output is imported into the database. Optional integrations cover Google OAuth sign-in, Freshservice department validation, Gemini for AI-generated report content or agent responses, Langfuse tracing, and an allowlisted read-only gcloud/bq context worker for live cloud investigation.
Deployment boundary
The README states that the supplied stack should not be exposed to untrusted networks. The development worker has Docker-socket access to launch scanner containers. The project has not had an independent security review and does not claim production readiness. It is licensed under Apache 2.0 and is not affiliated with Prowler.
Community Discussions
Be the first to start a conversation about prowler agent
Share your experience with prowler agent, ask questions, or help others learn from your insights.
Pricing
Self-hosted (Apache 2.0)
Self-hosted workspace for reviewing Google Cloud security findings, licensed under Apache 2.0. Early-stage; supplied Docker Compose setup is for trusted local development only.
- Licensed under Apache 2.0
- Self-hosted; Docker Compose for trusted local development only
- Onboard GCP organizations and projects
- Run and import Prowler GCP scans
- Triage findings with assign, annotate and mute
Capabilities
Key Features
- Onboard GCP organizations and projects
- Run Prowler GCP scans or import CSV, OCSF JSON, HTML and compliance exports
- Assign, annotate and mute findings with preserved decisions across scans
- Compliance framework rollups
- PDF assessment reports with optional AI-generated content
- Audit log of mutations
- Department-scoped Editor/Admin access
- Optional read-only live cloud context via gcloud/bq