Talos
Self-hosted, open-source beta AI agent for terminal and Telegram with a deterministic permission kernel and action- or task-scoped approvals.
At a Glance
MIT-licensed software for self-hosting. Bring your own model access; model-provider and hosting costs depend on your setup.
Engagement
Available On
Listed Sep 2026
About Talos
Talos is a self-hosted, open-source AI agent written in Python that runs on your own machine, takes instructions over a chat channel (terminal, Telegram, email, or WhatsApp), reasons through a language model, and executes tools — but only after a deterministic security kernel has ruled on each action. The project is available under the MIT license on GitHub and entered beta on October 1, 2026. See the release page for the current version.
What It Is
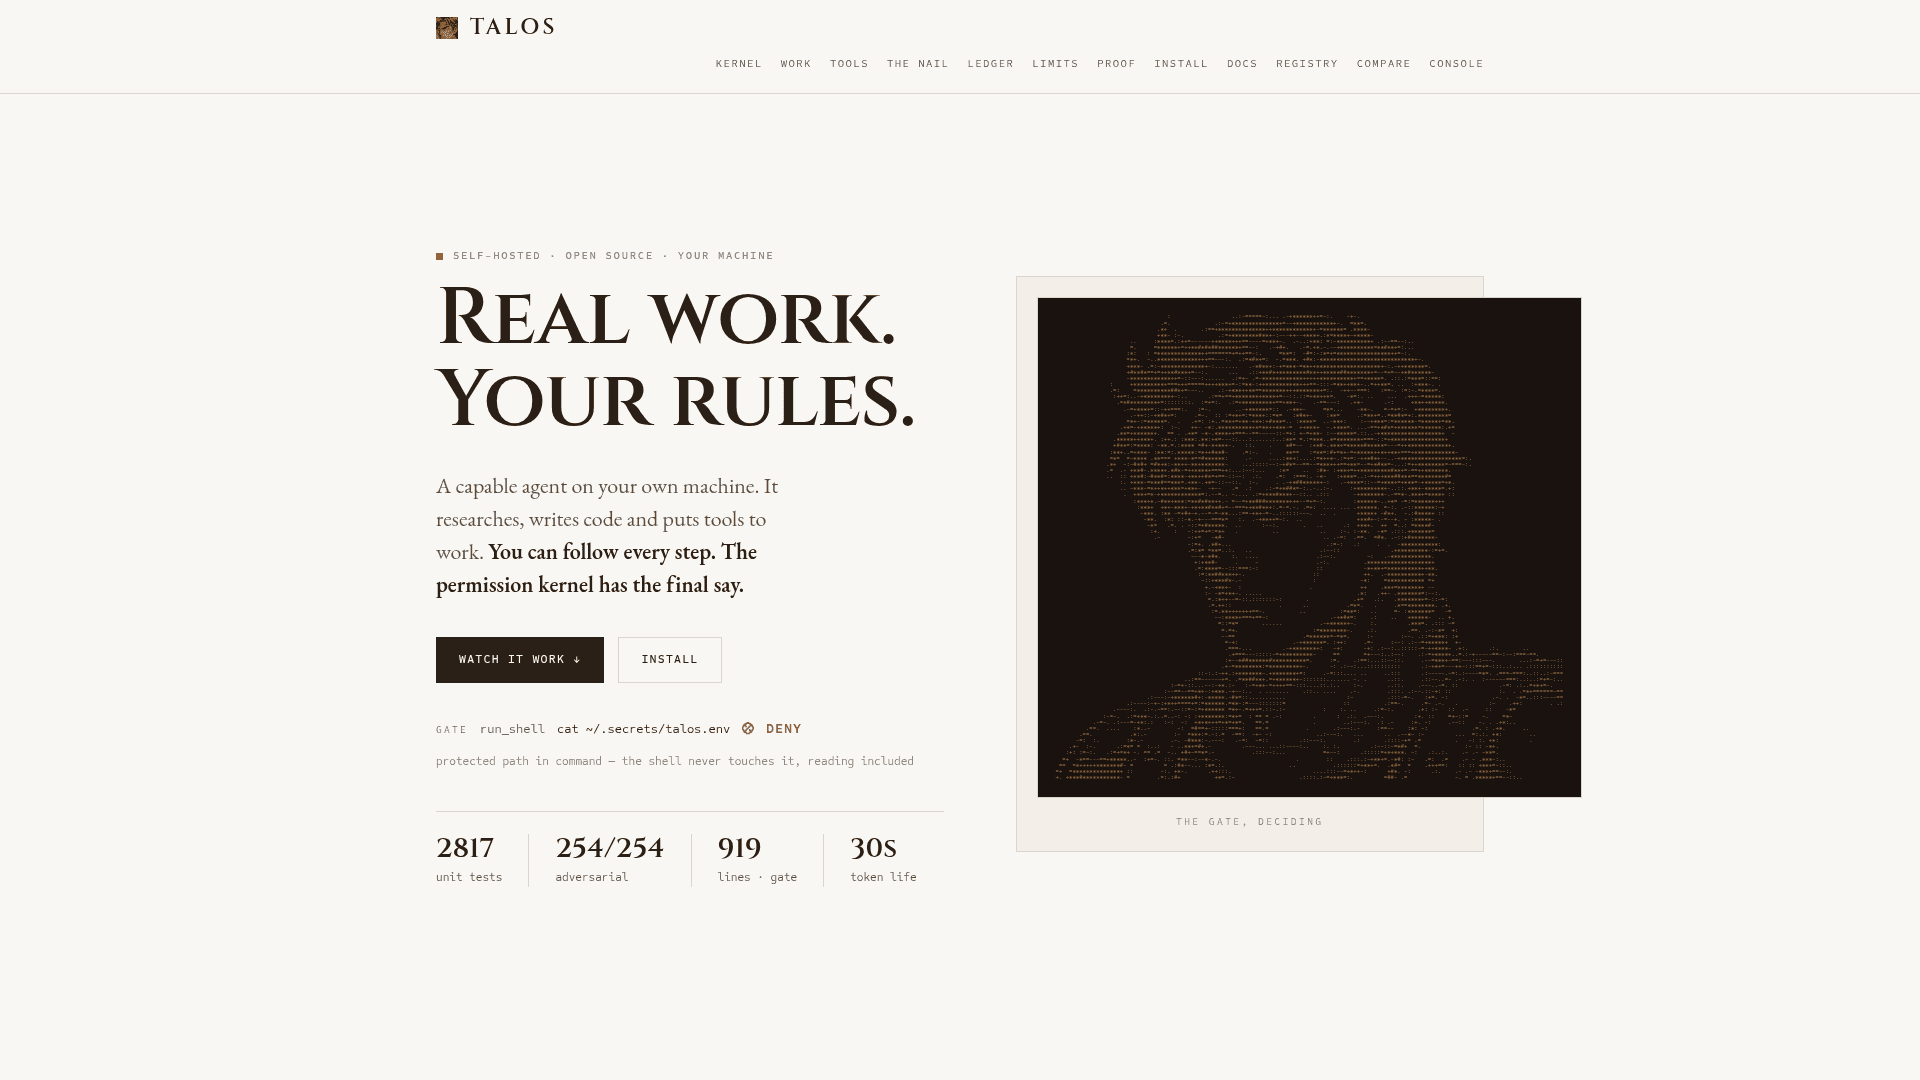
Talos sits in the category of autonomous agent frameworks with a security-first design philosophy. Its core premise is that the language model proposes actions but never decides them: every tool call passes through PolicyKernel.decide(), which returns exactly three verdicts — ALLOW, NEEDS_HUMAN, or DENY — before any runner is invoked. Authority is represented as a capability token bound to exact arguments, valid once, for 30 seconds. A tool without a registered target extractor is DENY by construction, not by a rule someone wrote.
How the Permission Kernel Works
The kernel's decision pipeline covers four broad classes of action:
- Ordinary work (reads, builds, tests, writes inside the workspace) — runs automatically
- Risky but recoverable (curl piped to shell,
git reset --hard,rm -rf <path>) — asks the operator - Persistence and secrets (
.bashrc, systemd units,~/.ssh, the agent's own source) — asks the operator - Catastrophic (
rm -rf /,mkfs,ddto a block device, fork bomb) — refused unconditionally
DENY is evaluated before the approval check, so a human "yes" cannot reach a hardline rule. Operators can approve one exact action with Allow once or approval-required actions within the current foreground task with Allow this task. Task-scoped approval ends when that task finishes or the operator stops it; it does not carry into a new task or override a kernel denial. The kernel still judges every action. One-shot approvals have a five-minute TTL and are re-verified against file hashes immediately before execution.
The Autonomy Dial and Unattended Ceiling
/autonomy 0..5 sits above the kernel and can only tighten, never loosen. Level 5 is the unfiltered kernel; level 0 refuses everything. During unattended runs (timed schedules, background tasks, delegated sub-runs), NEEDS_HUMAN automatically becomes DENY — what may run without asking runs, everything else is reported rather than performed. This means a timed run can do strictly less than something typed interactively, which is the opposite of how cron usually works.
Tool Set and Worker Delegation
Talos beta includes 33 gated tools across read, write, and execution effect classes. These cover browsing, web search, file operations, media perception, sandboxed shell execution, remote SSH execution, HTTP requests, git network operations, and worker delegation.
Worker delegation (delegate_code, delegate_dag, delegate_agy, delegate_codex) hands bounded coding tasks to a confined Claude or Codex worker process running in a UID-separated disposable workspace. MCP integration is routed through the claude-worker seam — Talos itself never speaks MCP; the child worker does, and which servers may exist is an operator decision declared in a gitignored registry file.
Channels and Identity Model
Every inbound channel fetches rather than listens — Telegram long-polls, mail pulls over IMAP, WhatsApp uses an operator-controlled SSH broker queue. No port is opened. Identities are channel-qualified: telegram:123456789 and cli:1000 are distinct even if they represent the same person. The agent ships with zero allowed identities; TALOS_ALLOWED_PRINCIPALS must be set explicitly or the agent refuses to start.
Beta, Compatibility, and Installation
Talos entered beta on October 1, 2026. Supported hosts are Linux and macOS with Python 3.11–3.13; Windows is not a tested host. The MIT license covers the software. Operators supply their own configured model-provider access or supported signed-in CLI; model-provider access is not included for free.
The release page lists current releases. Beta release notes link version-specific executed evidence. Test collection includes explicit platform and repository skips, so collected test totals should not be read as a universal passing-test count.
An optional Pinokio launcher is available for Linux and macOS. Existing installations are not upgraded automatically; review the installation and update instructions before upgrading.
Correction — October 2, 2026: Updated beta status, approval scope, host/Python support, model-access costs, release links, version-specific counts, and Pinokio installation guidance.
Community Discussions
Be the first to start a conversation about Talos
Share your experience with Talos, ask questions, or help others learn from your insights.
Pricing
Open Source
MIT-licensed software for self-hosting. Bring your own model access; model-provider and hosting costs depend on your setup.
- Full permission kernel with 33 gated tools
- Terminal and Telegram channels
- Sandboxed shell execution
- Worker delegation to Claude and Codex
- MIT license — free to use, modify, and distribute
Capabilities
Key Features
- Deterministic permission kernel with ALLOW/NEEDS_HUMAN/DENY verdicts
- 33 gated tools across read, write, and exec effect classes
- Sandboxed shell execution (bubblewrap on Linux, sandbox-exec on macOS)
- Capability tokens bound to exact arguments, valid once for 30 seconds
- Autonomy dial (0-5) that can only tighten, never loosen
- Unattended ceiling converts NEEDS_HUMAN to DENY for timed/background runs
- Worker delegation to confined Claude and Codex workers
- MCP integration via claude-worker seam with operator-owned registry
- Multi-channel support: terminal, Telegram, email (IMAP), WhatsApp (SSH broker)
- Zero default identities — TALOS_ALLOWED_PRINCIPALS must be set explicitly
- Render-only browser with DNS resolver caging against rebind attacks
- Announced plans that tighten step budgets rather than widen them
- Verifiable audit trail with write-ahead intent logging
- /undo command with file snapshot rollback
- Background tasks with independent cancellation and unattended ceiling
- Conversation memory with bounded history and middle-summarization
- Skill writing gated behind mandatory human approval
- Per-provider credential model with fail-closed key resolution
- Keyless web search via DuckDuckGo by default
- Local audio transcription with faster-whisper
- Local speech synthesis with piper
- Video frame extraction via ffmpeg
- /policy dry-run command to preview kernel verdicts without executing
- Verifiable event log with chain digest and anchor pinning
- Allow once or allow the current foreground task; kernel denials still apply
- Linux and macOS hosts with Python 3.11–3.13
- Optional Pinokio launcher; existing installations are not automatically upgraded