
Adversa AI Coding Agent Security Platform
Runtime control layer that monitors AI coding agent actions, links them into chains, and blocks dangerous ones before they complete.
At a Glance
About Adversa AI Coding Agent Security Platform
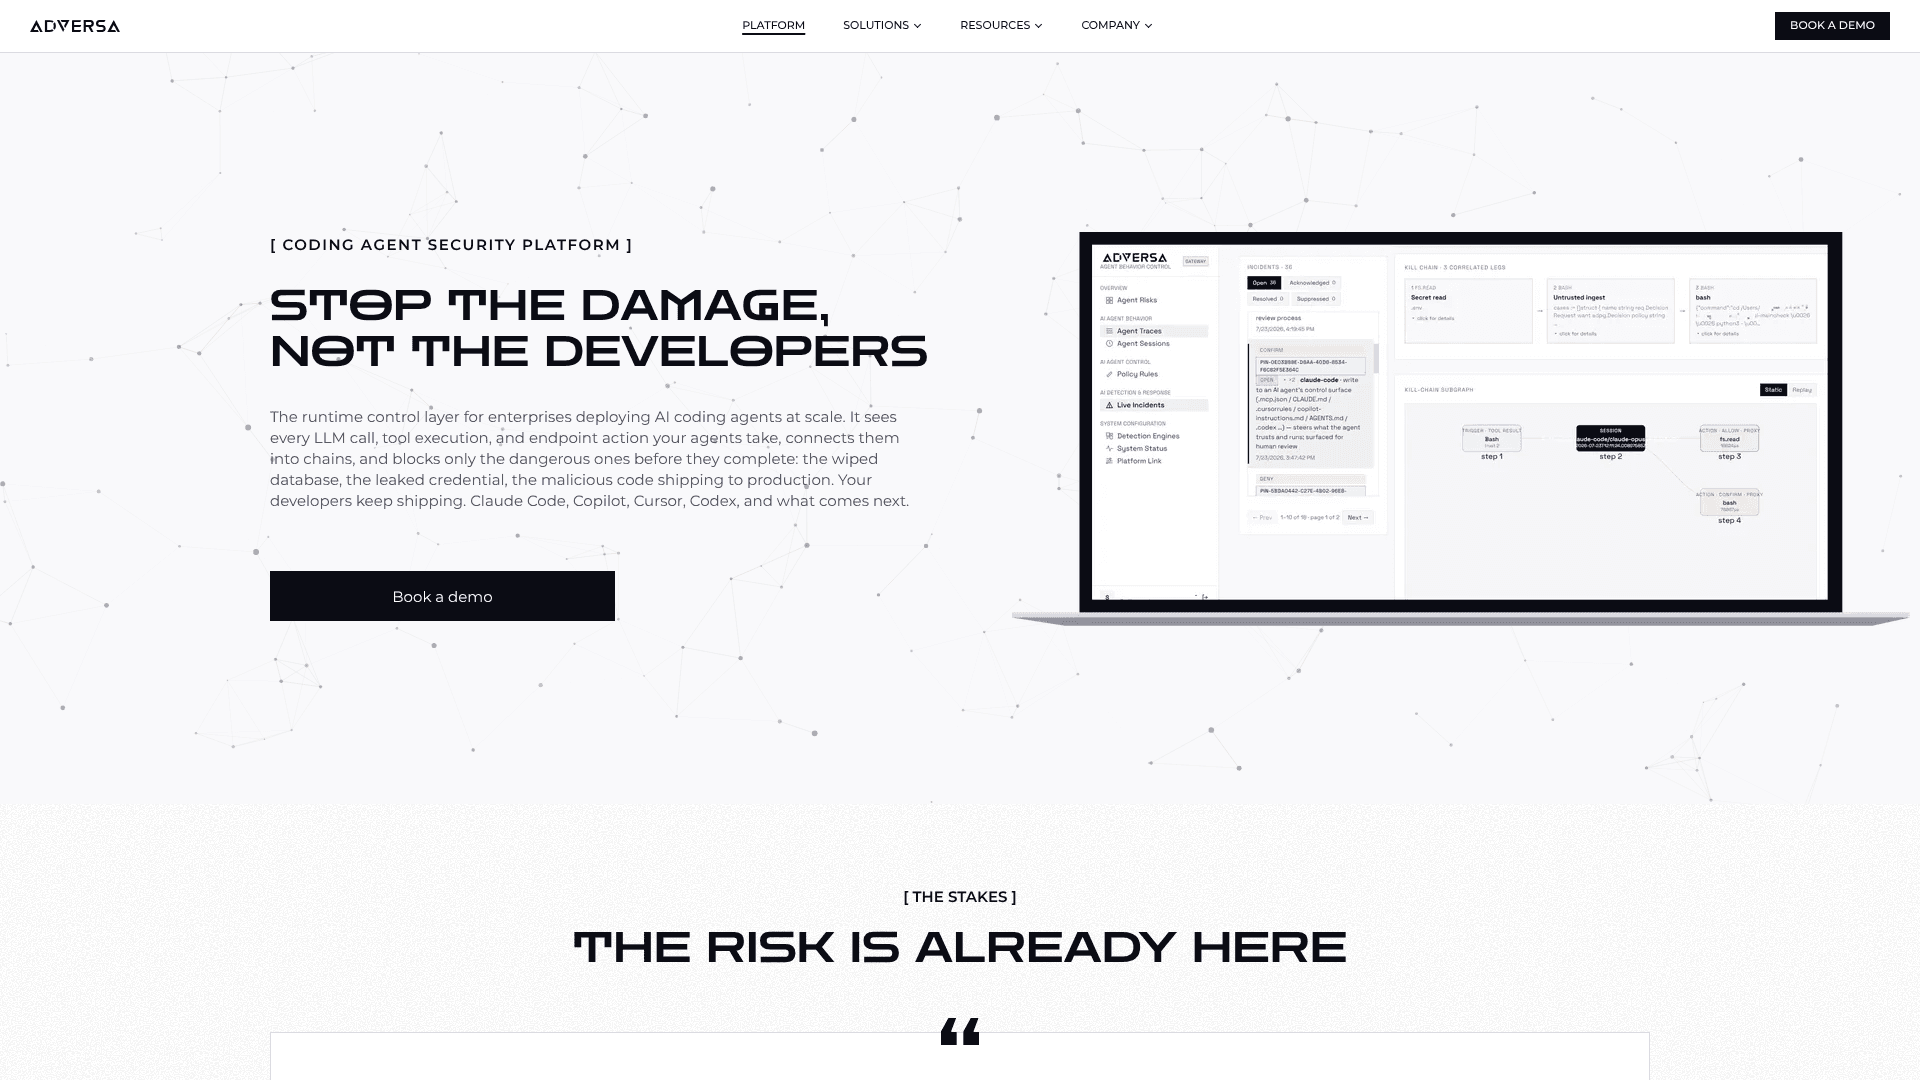
Adversa AI Ltd. offers a Coding Agent Security Platform that acts as a runtime control layer for enterprises deploying AI coding agents such as Claude Code, Copilot, Cursor, and Codex. It captures LLM calls, tool executions, and endpoint actions, connects them into chains, and blocks dangerous ones before they complete. The vendor states the platform is in early access with first production deployments live.
What It Is
The platform is an AI detection and response product built for coding agents. Rather than inspecting prompts alone, it builds an agent behavior graph correlating model conversations, tool calls, and endpoint actions, and scores risk across the linked chain. Detections ship with the chain, the rule that fired, and the evidence behind it.
How the See, Understand, Stop workflow works
- See: Watches model traffic (including tool and MCP calls), the agent harness, the developer's machine, and vendors' compliance APIs.
- Understand: Correlates events into chains, so a lone suspicious step is context rather than an alert.
- Stop: Blocks a chain when its risk score crosses a configured threshold; enforcement can be scoped per policy, environment, or team.
Adversa says over 300 policies ship by default, and teams can describe policies in plain English, which the platform converts into enforceable policies that are validated, simulated, versioned, and approved before going live.
Deployment model
The vendor describes three components: an agent security gateway on agent traffic (inline or reading from an existing gateway), endpoint sensors on developer machines that watch only agent actions, and harness hooks plus provider integrations. It runs on customer infrastructure or in the cloud. Pilots begin in observe mode, with blocking enabled when the customer is ready. The vendor states the design fails open and that SIEMs can ingest the event stream.
Compliance and roles
The vendor maps its action records and pre-execution blocking to requirements such as EU AI Act Articles 12 and 14, DORA, and SR 11-7, and to frameworks like NIST AI RMF, ISO 42001, and SOC 2. It targets AppSec teams, CISOs, engineering leaders, and risk and compliance teams.
Community Discussions
Be the first to start a conversation about Adversa AI Coding Agent Security Platform
Share your experience with Adversa AI Coding Agent Security Platform, ask questions, or help others learn from your insights.
Pricing
Contact sales
Pricing is not published; the platform page offers a Book a demo CTA.
Capabilities
Key Features
- Visibility into LLM calls, tool and MCP calls, file access, and outbound connections
- Agent behavior graph correlating model, tool, and endpoint actions
- Chain-level risk scoring with pre-execution blocking
- 300+ default policies
- Plain-English policy creation with validation, simulation, and versioning
- Observe-only mode for pilots
- Agent security gateway and endpoint sensors
- Harness hooks and vendor compliance API integrations
- Event stream ingestible by SIEM
- Compliance evidence and audit records of agent actions