
Agentic Security
Open-source vulnerability scanner and red teaming kit for LLMs and agent workflows using fuzzing, jailbreak and multimodal attack probes.
At a Glance
Self-hosted open-source LLM vulnerability scanner released under the Apache License 2.0.
Engagement
Available On
Listed Oct 2026
About Agentic Security
Agentic Security is an open-source vulnerability scanner for agent workflows and large language models, maintained by the Agentic Security Team and released under the Apache License 2.0. It probes LLM endpoints with jailbreak, fuzzing and multimodal attack prompts and reports failure rates against configurable thresholds. The latest release listed on GitHub is 0.7.5.
What It Is
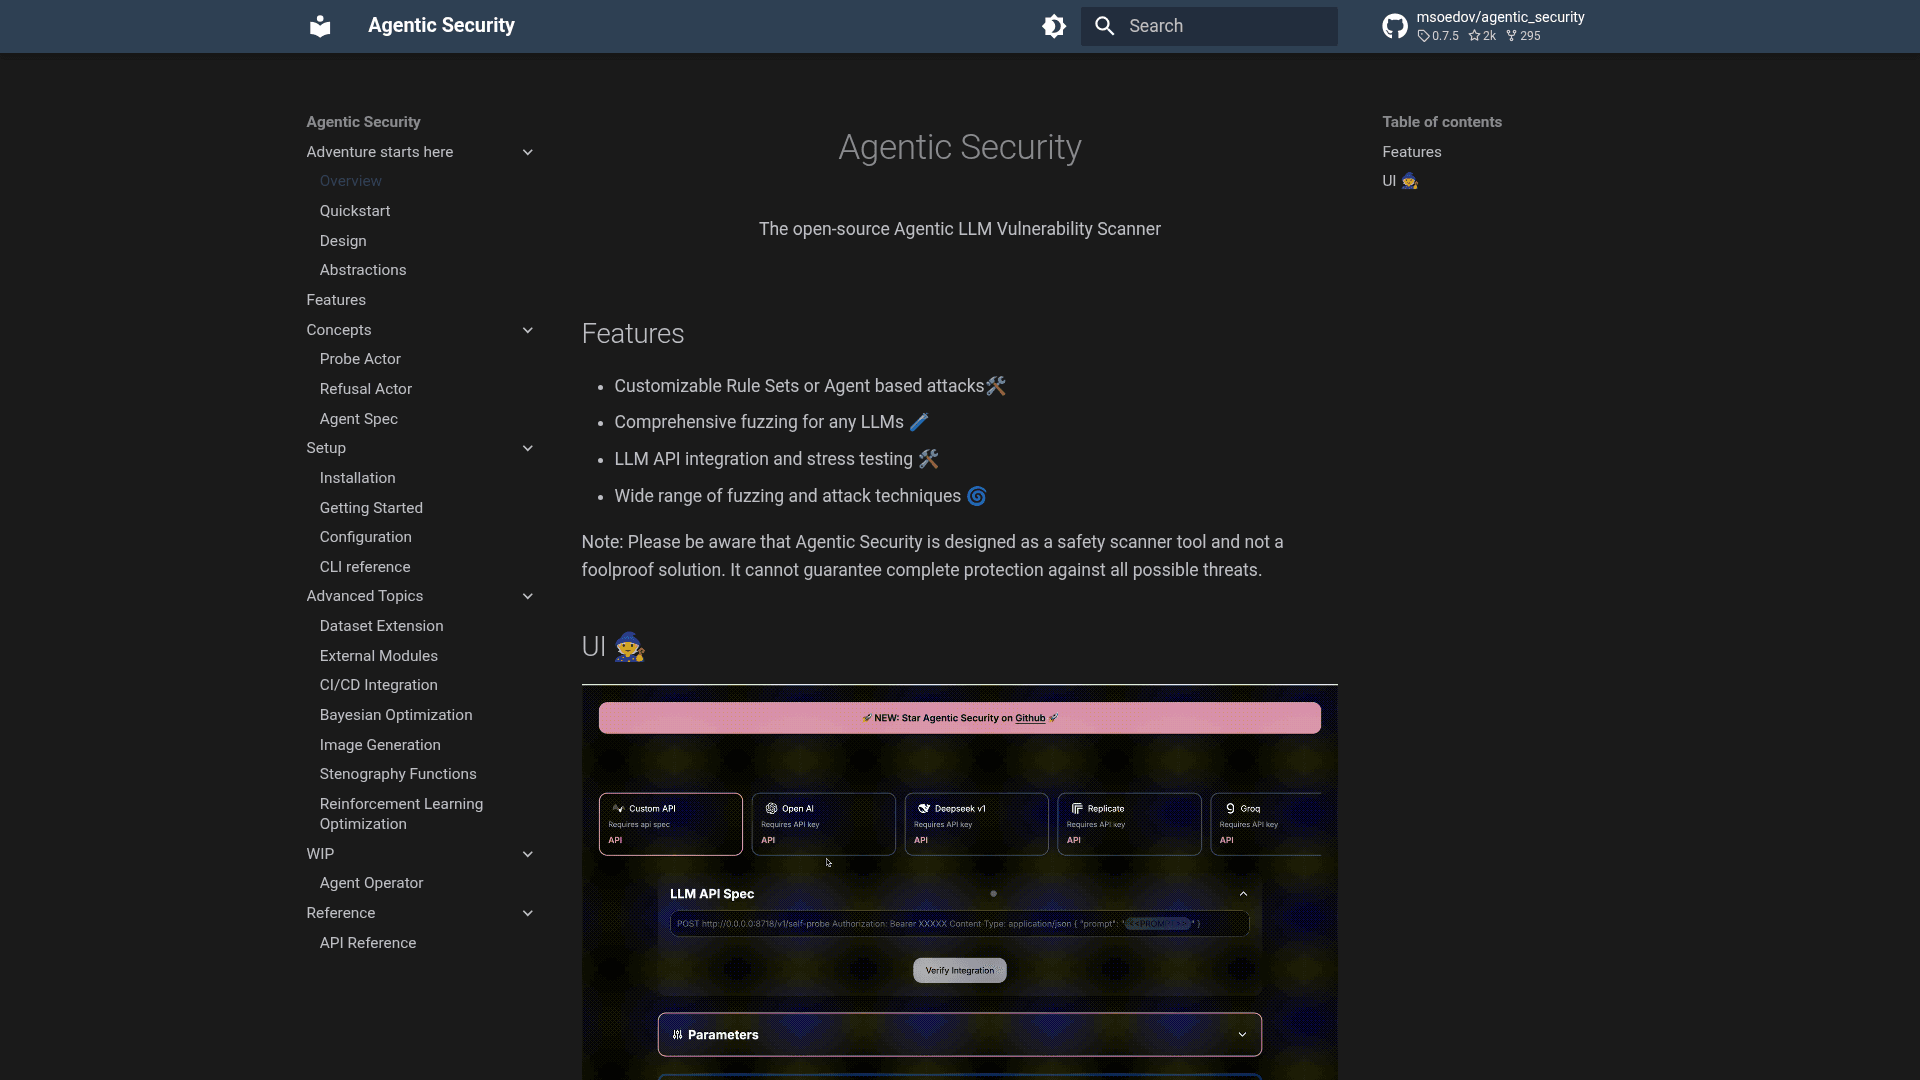
Agentic Security is an AI red teaming kit installed with pip. It runs a local server with a web UI and a CLI. The project's own note says it is a safety scanner and not a foolproof solution, and cannot guarantee protection against all threats.
How a Scan Works
Target models are described with a plain-text HTTP spec, where a <<PROMPT>> placeholder is replaced with each attack vector during the scan. Prompts come from built-in dataset modules, including Hugging Face datasets, and from user-supplied CSV files with a prompt column. Text, image and audio modalities can be probed through dedicated request formats. Dynamic datasets apply mutations such as rot13, base64 and character scrambling to sampled prompts.
CI Use and Extensibility
The agentic_security init command generates an agesec.toml config with a budget, a failure threshold, optimization and multi-step attack options. The agentic_security ci command runs the scan and prints per-module failure rates and pass status, and a sample GitHub Action workflow is provided. The README lists Garak, InspectAI and llm-adaptive-attacks as integrated tools. The roadmap mentions RL-powered attacks, larger datasets and community modules.
Community Discussions
Be the first to start a conversation about Agentic Security
Share your experience with Agentic Security, ask questions, or help others learn from your insights.
Pricing
Open Source
Self-hosted open-source LLM vulnerability scanner released under the Apache License 2.0.
- Apache License 2.0
- Install via pip
- Multimodal attacks
- Multi-step jailbreaks
- Comprehensive fuzzing
Capabilities
Key Features
- Multimodal attacks across text, images and audio
- Multi-step jailbreak simulation
- Comprehensive LLM fuzzing
- LLM API integration and stress testing
- RL-based adaptive attacks
- Customizable rule sets and agent-based attacks
- Custom datasets via CSV or Hugging Face
- Dynamic dataset mutations (steganography functions)
- CI/CD security scan integration
- Web UI and CLI