
DeepTeam
Open-source Python framework for red teaming LLM applications and AI agents by simulating adversarial attacks and detecting vulnerabilities.
At a Glance
About DeepTeam
DeepTeam is an open-source red teaming framework for LLM systems from Confident AI, the team behind DeepEval. It simulates attacks such as jailbreaking, prompt injection and multi-turn exploitation against AI agents, RAG pipelines and chatbots, and reports vulnerabilities like bias, PII leakage and SQL injection. It runs locally and is licensed under Apache 2.0.
What It Is
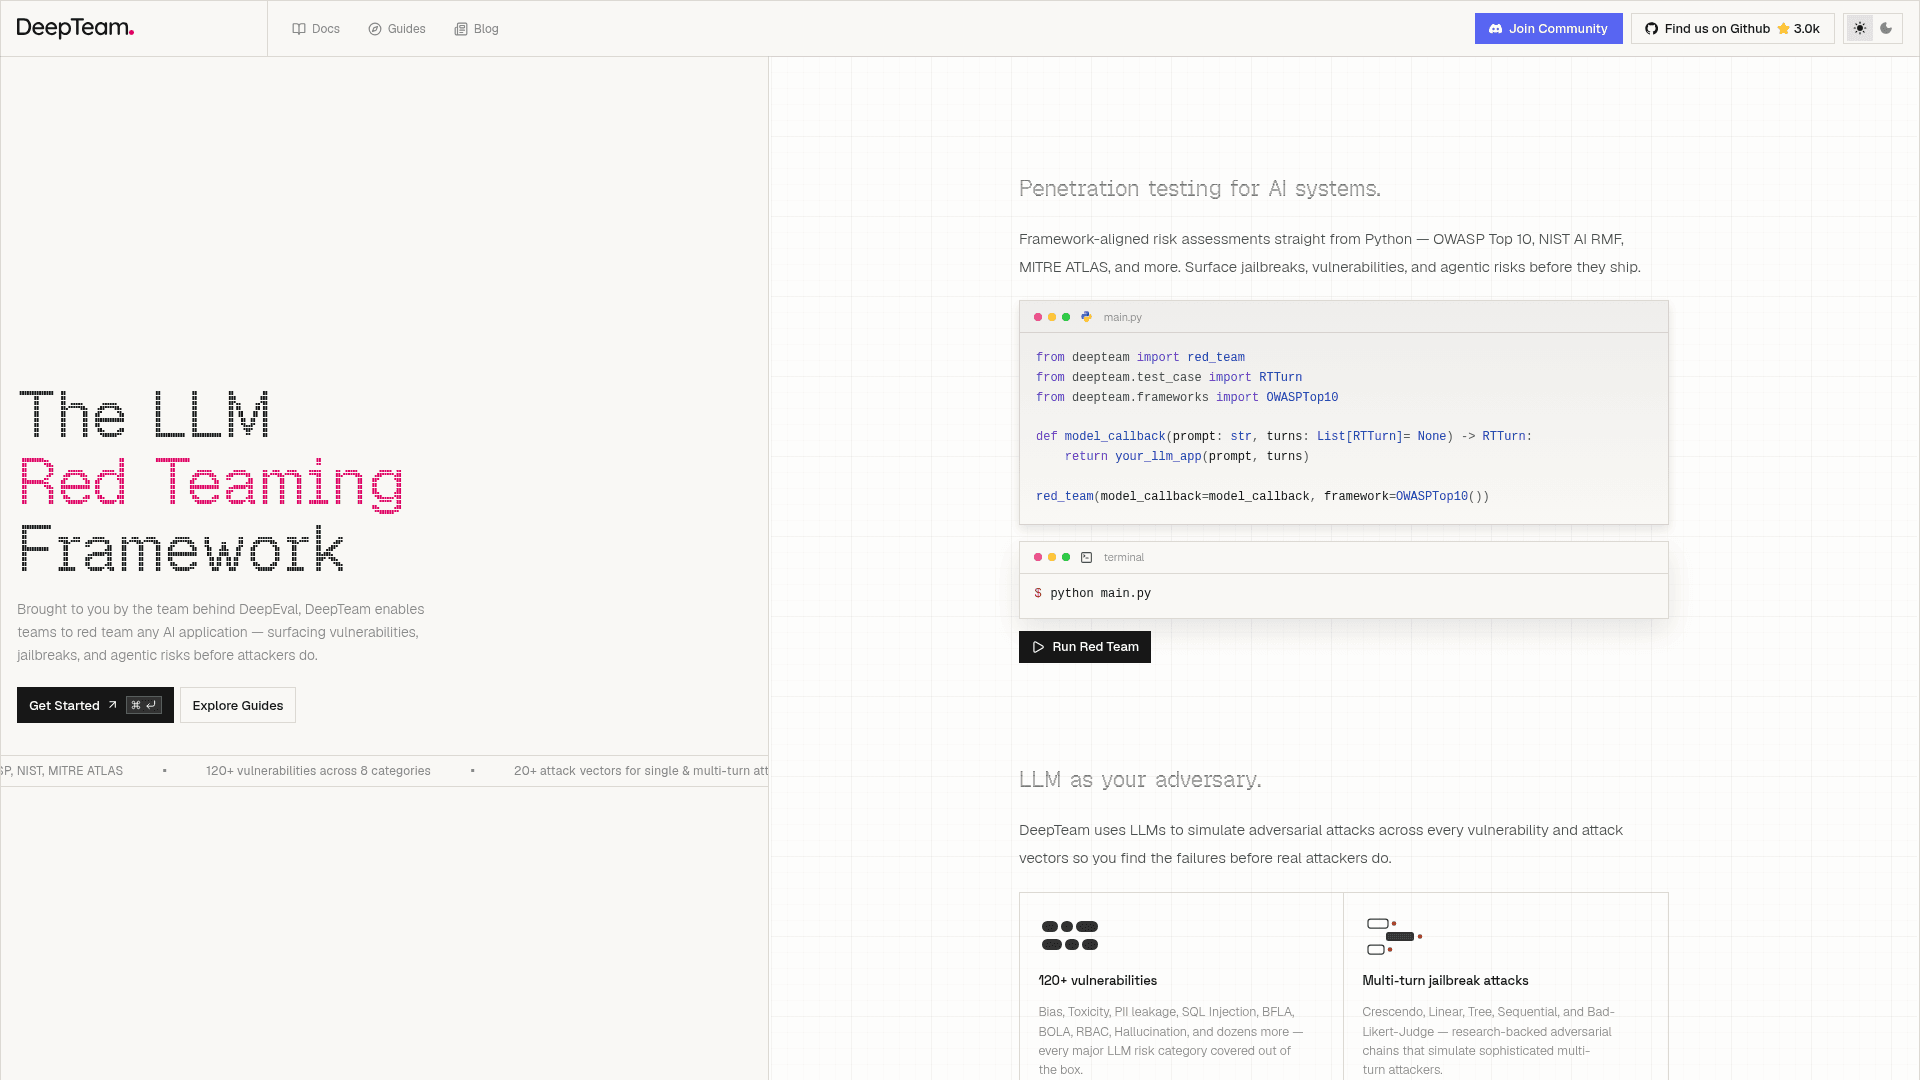
DeepTeam works like penetration testing for LLM applications. You wrap your application in a model callback, choose vulnerabilities and attacks (or an entire safety framework), and the tool generates adversarial prompts dynamically, so no prepared dataset is needed. Each vulnerability is scored by LLM-as-a-judge metrics that run locally and produce binary pass/fail results with reasoning. The resulting risk assessment can be viewed in dataframes and saved locally as JSON.
Vulnerabilities and Attacks
The README documents 50+ vulnerabilities grouped into data privacy, responsible AI, security, safety, business and agentic categories, plus custom vulnerabilities defined in code. The homepage advertises 120+ vulnerabilities. More than 20 attack methods cover single-turn techniques (prompt injection, roleplay, encoding obfuscation, context flooding) and multi-turn jailbreaks (Linear, Tree, Crescendo, Sequential, Bad Likert Judge).
Frameworks and Guardrails
Built-in framework support maps categories to the relevant vulnerabilities and attacks: OWASP Top 10 for LLMs 2025, OWASP Top 10 for Agents 2026, NIST AI RMF, MITRE ATLAS, BeaverTails and Aegis. After testing, seven guardrails (toxicity, prompt injection, privacy, illegal content, hallucination, topical and cybersecurity) can classify inputs and outputs in production.
Setup Path
Install with pip, set an OpenAI API key or configure a custom model, and run a Python script that calls red_team. Runs can also be driven from the CLI with YAML configs, and the site lists CI/CD runners such as GitHub Actions, GitLab CI and Jenkins. Results can optionally be managed in the separate Confident AI platform.
Community Discussions
Be the first to start a conversation about DeepTeam
Share your experience with DeepTeam, ask questions, or help others learn from your insights.
Pricing
Open Source
Apache 2.0-licensed DeepTeam red teaming framework that runs locally; LLM provider costs are external.
- Runs locally on your machine
- Open-source red teaming framework for LLM systems
- Guardrails to prevent issues in production
- Licensed under Apache 2.0
Capabilities
Key Features
- 50+ ready-to-use vulnerabilities with LLM-as-a-judge scoring
- 20+ single-turn and multi-turn adversarial attacks
- Framework-based red teaming (OWASP, NIST, MITRE ATLAS, BeaverTails, Aegis)
- 7 production guardrails for inputs and outputs
- Custom vulnerabilities and attacks
- CLI with YAML configs and Python API
- Local risk assessment output as dataframes and JSON
- Runs locally