
agentjail
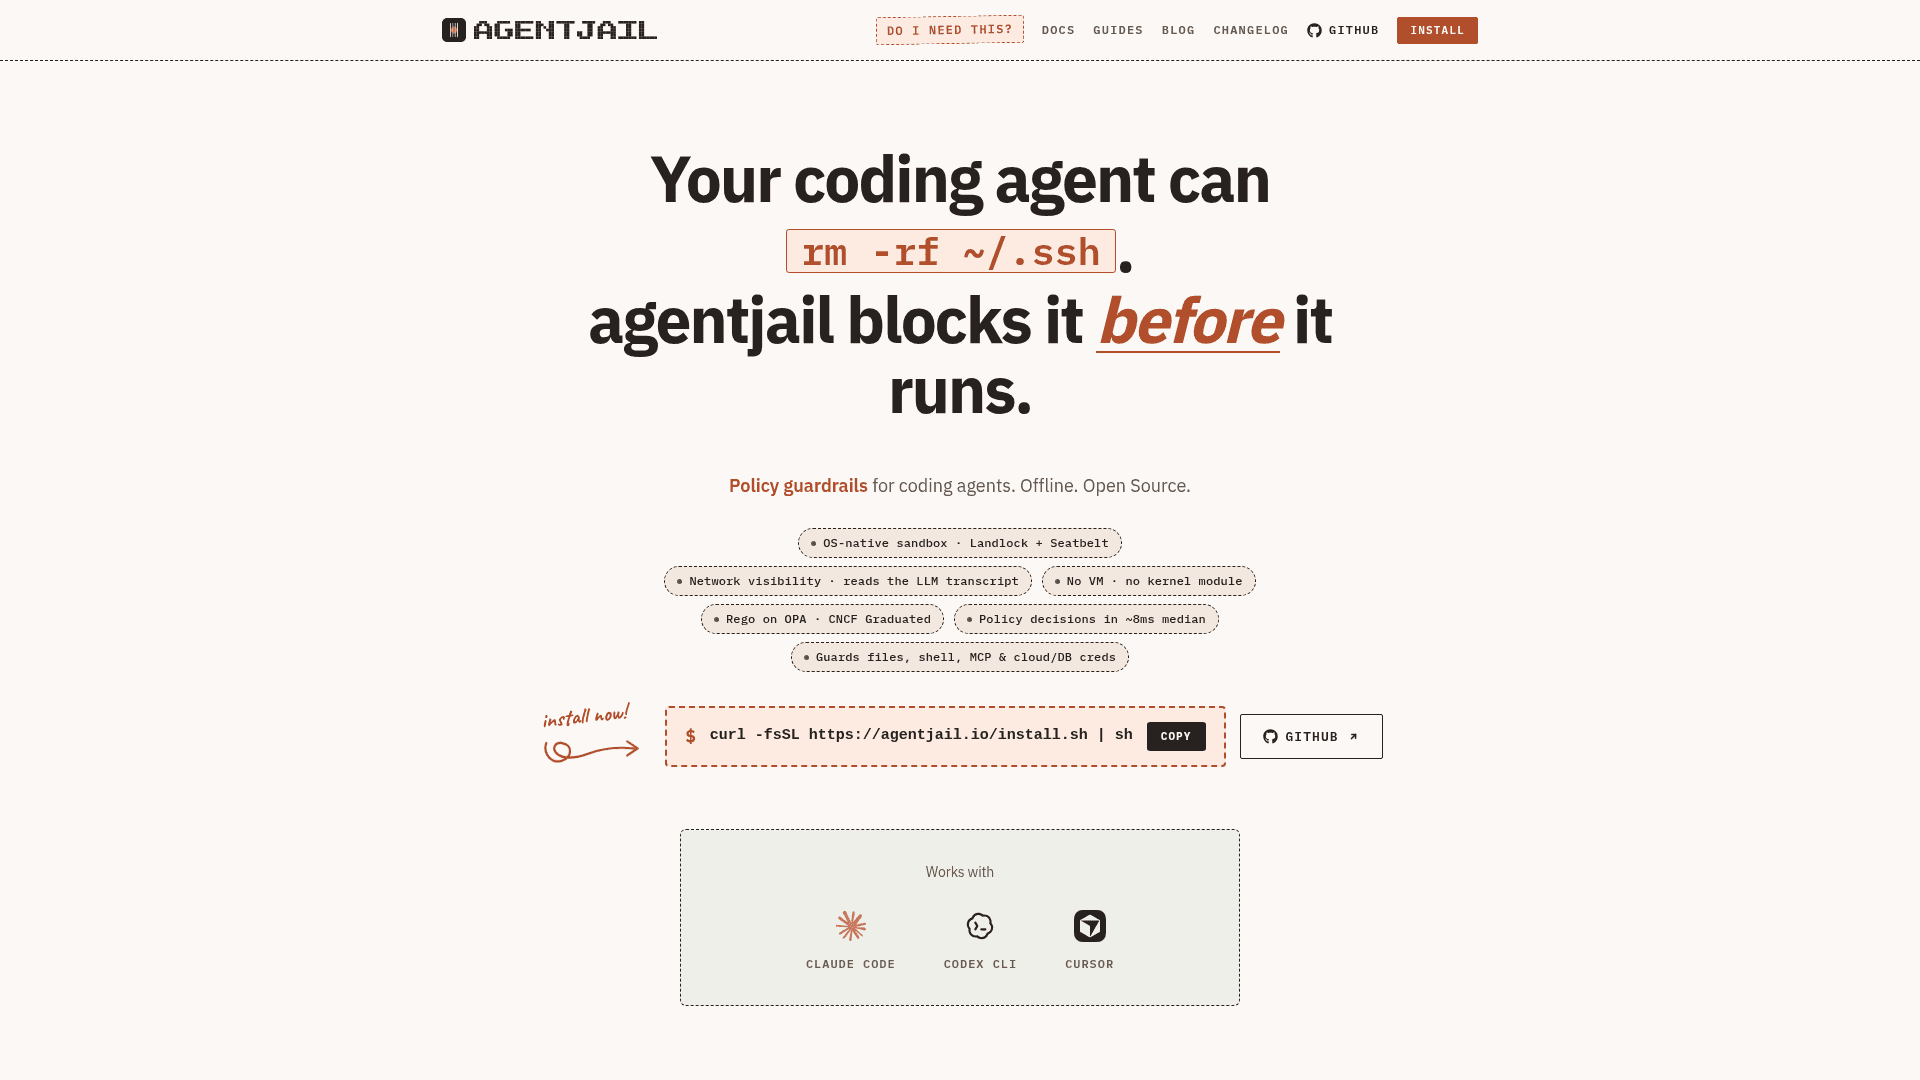
Open-source policy guardrails and OS-level sandboxing that check coding agent tool calls locally before they run.
At a Glance
About agentjail
agentjail is an open-source safety layer for coding agents such as Claude Code, Codex CLI and Cursor. It installs hooks that send each tool call to a local OPA daemon, which evaluates Rego policies and returns allow, ask or deny. Launching an agent through agentjail run adds an OS-native sandbox on top of the hook checks.
What It Is
agentjail is a local policy and sandboxing tool for AI coding agents. A one-line installer detects supported agents and registers hooks. Each supported tool call (shell commands, file reads and writes, MCP calls) is checked against policy before execution. The project says the median policy decision takes about 8 ms.
How enforcement works
Hooks provide policy decisions and explanations, but the README states they are cooperative checks, not a filesystem isolation boundary. agentjail run adds the agentjail-shield sandbox, which uses Landlock on Linux and Seatbelt on macOS to enforce filesystem restrictions independently of the hook daemon. An optional transparent tunnel (--tunnel) adds network visibility and per-host policy, including TLS interception that is disclosed at launch. On macOS, LLM traffic can be captured through a base-URL capture gateway.
What it blocks by default
Three core policies are always on: file_policy for paths such as .ssh, .aws and .env files, mcp_policy for unknown or payment-related MCP servers, and command_policy for patterns like rm -rf, curl | bash, sudo and force-push. Opt-in library rules cover shell init writes, destructive AWS or git commands, history reads and shell eval. Custom rules are written in Rego and added with agentjail policy add.
Operations and visibility
The CLI provides doctor, logs, stats, session listing, an interactive replay TUI, a local web UI, a monitor mode that reports what would have been blocked, and cost analytics for Claude Code, Codex and OpenCode usage. MCP servers can be listed, allowed, blocked and scanned. Anonymous telemetry can be disabled. The roadmap lists a macOS app and eBPF/system-extension enforcement as planned.
Community Discussions
Be the first to start a conversation about agentjail
Share your experience with agentjail, ask questions, or help others learn from your insights.
Pricing
Open Source
Self-hosted agentjail CLI and daemon under the Apache License 2.0, free to use, modify and distribute.
- Apache-2.0 licensed core
- OS-native sandbox (Landlock + Seatbelt)
- Rego/OPA policy guardrails
- MCP policy and inventory
- Network visibility and egress control
Capabilities
Key Features
- Pre-tool-use policy checks via OPA Rego
- Allow, ask and deny verdicts
- OS-native sandbox using Landlock and Seatbelt
- Default file, MCP and command policies
- Per-tool MCP policy and MCP inventory scan
- Default-deny network egress with allowlist
- Network visibility via capture gateway and transparent tunnel
- Monitor mode to preview blocks before enforcing
- Custom Rego policies with validation
- Replay TUI and local web UI
- Cost analytics and budget alerts
- Encrypted credential broker with session credentials
- Self-protection rules and daemon auto-update