AutoCVE
Agent-driven platform that automates CVE discovery through source code auditing, vulnerability verification, and report generation.
At a Glance
Self-hosted AutoCVE core released under AGPL-3.0, an OSI-approved license. Model/LLM costs are external.
Engagement
Available On
Listed Oct 2026
About AutoCVE
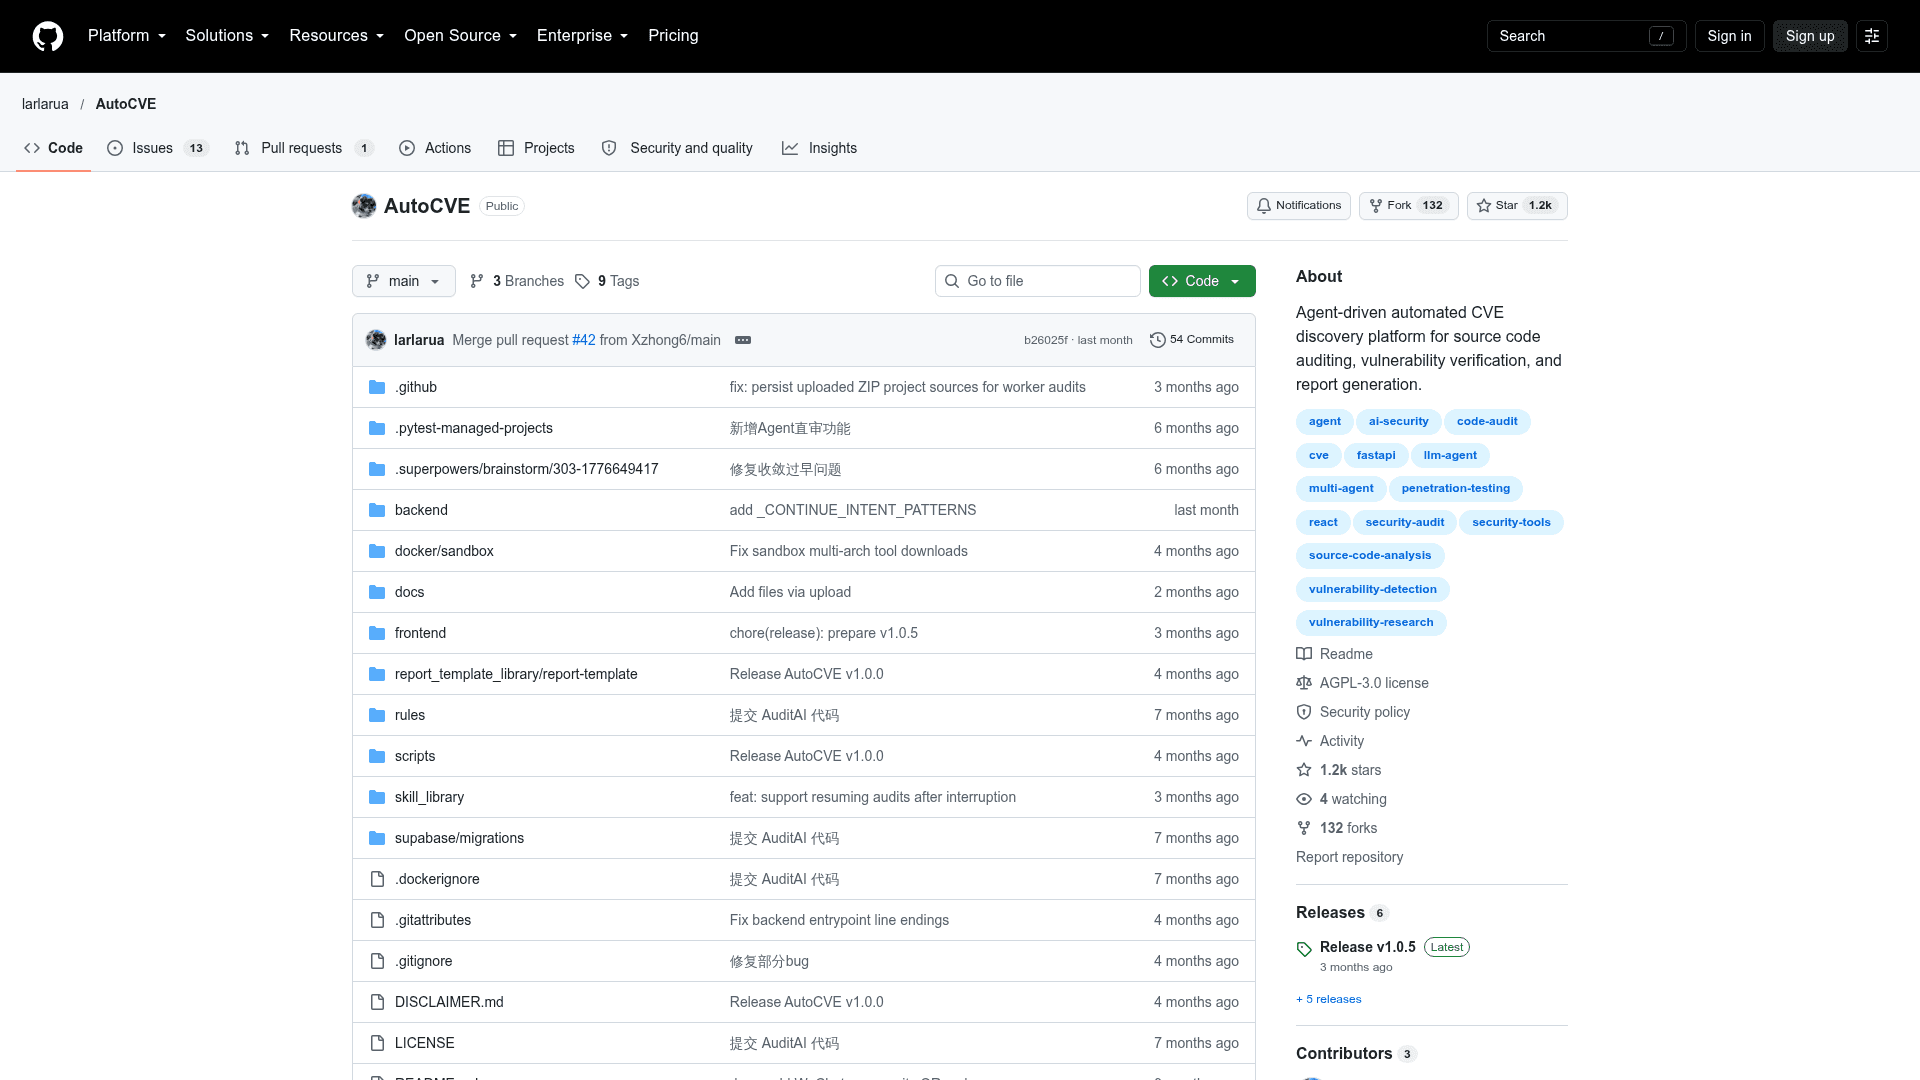
AutoCVE is an open-source, AGPL-3.0 platform published by larlarua on GitHub that uses LLM agents to audit open-source code for vulnerabilities and prepare CVE submission reports. The latest listed release is v1.0.5, and it deploys with Docker Compose.
The README says the workflow covers project selection, repository import, audit task creation, agent-based vulnerability discovery, and CVE report generation.
What It Is
AutoCVE is a web application with a React frontend and a FastAPI backend, backed by PostgreSQL. Users configure a model, import a project, create an audit task, follow the audit live, manage the findings, and edit or export the report. An Orchestrator coordinates Recon, Scan, Triage, Finding, and Verification agents. Together they handle information gathering, tool scanning, false-positive filtering, deeper vulnerability analysis, and dynamic verification.
Audit Modes and Agents
Three audit modes are offered. Enhanced Scan runs Scan then Triage to analyze tool results and filter false positives. Smart Audit uses the Finding agent for deep source analysis aimed at CVE and 0-day research. Comprehensive Audit combines both. The Finding agent works through a ReAct loop with specialized tools, nudge-based correction, and a structured FinalizeFinding termination step.
Interaction, Findings and Skills
The full audit session serves as conversation context, so users can ask follow-up questions, request more evidence, or have the attack chain explained. The interface shows activity logs, an Agent Tree, tool calls, stage progress, and preliminary reports. Agents submit findings through tools, which are deduplicated and stored in a vulnerability management module. Per-agent Skills can be configured.
Results and Responsible Use
The README reports that in a one-week test, AutoCVE found and submitted 30 vulnerabilities across 14 open-source projects. Full reports are linked from a separate repository. The project states that it is only for authorized security research and code audits, and asks users to follow each target's disclosure policy.
Community Discussions
Be the first to start a conversation about AutoCVE
Share your experience with AutoCVE, ask questions, or help others learn from your insights.
Pricing
Open Source (Self-hosted)
Self-hosted AutoCVE core released under AGPL-3.0, an OSI-approved license. Model/LLM costs are external.
- License: GNU Affero General Public License v3.0 (AGPL-3.0)
- Self-hosted via Docker Compose
- Multi-Agent audit (Recon, Scan, Triage, Finding, Verification)
- Three audit modes: enhanced scan, smart audit, comprehensive audit
- Vulnerability management and Skills configuration
Capabilities
Key Features
- One-click CVE discovery workflow from project selection to report generation
- Multi-agent audit with Orchestrator, Recon, Scan, Triage, Finding and Verification agents
- Three audit modes: enhanced scan, smart audit, comprehensive audit
- Finding agent with ReAct loop and structured FinalizeFinding termination
- Interactive follow-up questions on audit results
- Visual audit tracing with Agent Tree, tool calls and activity logs
- Automatic vulnerability submission with deduplication and management
- Per-agent Skills configuration
- Editable and exportable reports
- Docker Compose deployment