
Brotli Checker
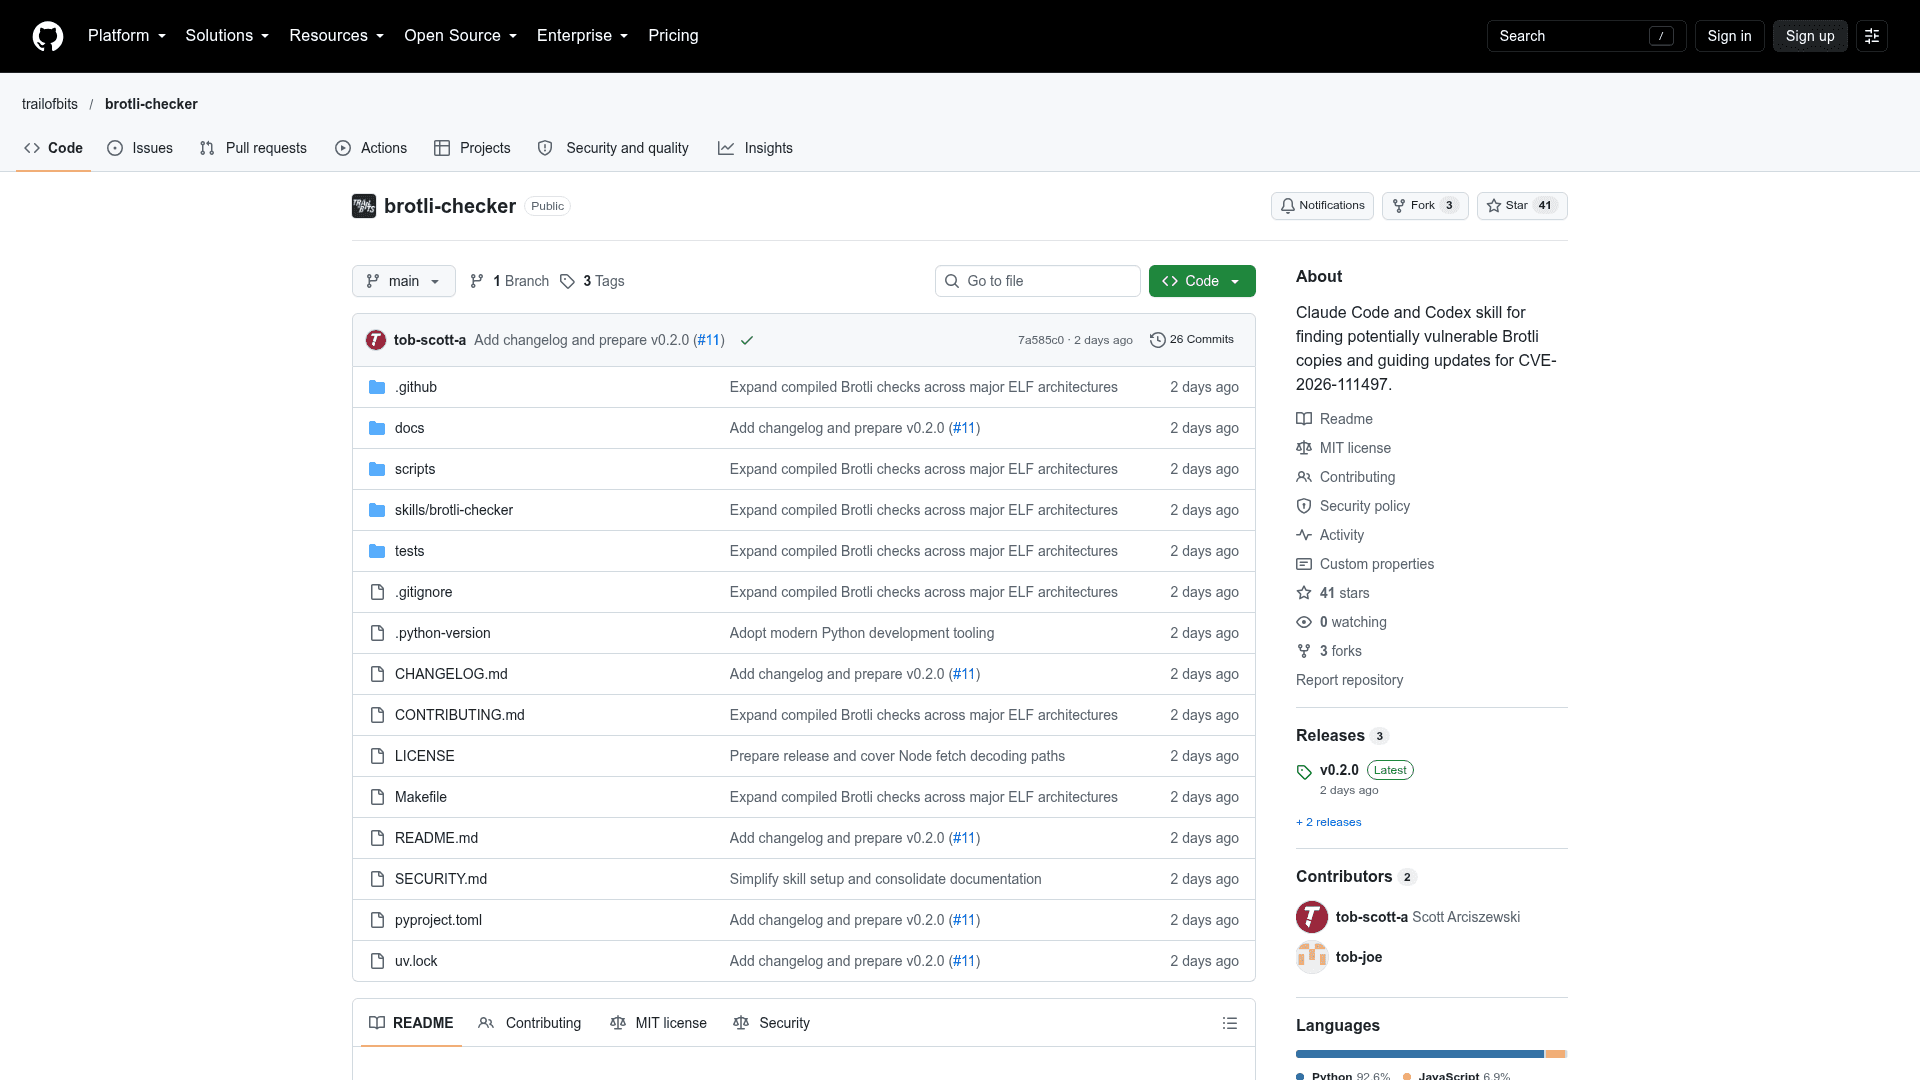
A Claude Code and Codex skill that scans projects for Brotli decoder copies that may need an update for CVE-2026-111497.
At a Glance
Brotli Checker skill and standalone scanner, released under the MIT License. Compiled Brotli references retain their upstream notices.
Engagement
Available On
Alternatives
Listed Oct 2026
About Brotli Checker
Brotli Checker is an open-source skill from Trail of Bits for Claude Code and Codex. It scans source, dependencies, app packages, and unpacked container filesystems for copies of the Brotli decoder that may need an update for CVE-2026-111497. The latest listed release is v0.2.0.
What It Is
Brotli Checker is a vulnerability-inventory skill and standalone Python scanner. It checks source fingerprints and supported ELF binary code, investigates which copies an app actually uses, and explains what to update or review. Each copy found keeps its own result, so a fixed copy does not clear other bundled copies.
How the Workflow Runs
After installing the skill, a user opens a project and asks the assistant to check it. A folder or app package can also be named. For source review, Trailmark maps calls to the decoder and fetch APIs so the assistant can find callers to inspect, and the assistant then checks whether those connections apply to the running app. If given only a website address, the skill explains what is missing and prepares a request for the hosting provider, since HTTP headers cannot establish patch status.
Running the Scanner Directly
The scanner can be run without an agent by pointing a Python script at an application path. Default output explains findings and next steps, and a JSON mode provides per-copy evidence, coverage gaps, and a plain-language summary. It reads files without executing application code or sending network probes.
Reading the Results
Affected code calls for an update or vendor-backport review. Version and dependency findings need confirmation against the actual build, and an empty scan does not establish that an app is safe. Compiled references cover x86, x86-64, ARM/Thumb, AArch64, RISC-V64, PowerPC64 little-endian, s390x, MIPS32/64, and LoongArch64 ELF builds, with coverage depending on compiler and build flags. Unsupported formats, skipped files, and resource limits are reported as coverage gaps. Rules use an advisory snapshot dated 2026-10-23.
Community Discussions
Be the first to start a conversation about Brotli Checker
Share your experience with Brotli Checker, ask questions, or help others learn from your insights.
Pricing
Open Source (MIT)
Brotli Checker skill and standalone scanner, released under the MIT License. Compiled Brotli references retain their upstream notices.
- MIT licensed core product
- Claude Code / Codex skill
- Standalone scanner using only the Python standard library
- Requires Python 3.12–3.15 and uv for Trailmark source discovery
- Compiled Brotli references retain upstream notices
Capabilities
Key Features
- Scans source, dependencies, app packages, and unpacked container filesystems
- Checks source fingerprints and supported ELF binary code
- Per-copy results for each Brotli decoder found
- Trailmark call mapping for decoder and fetch API callers
- Standalone scanner using only the Python standard library
- JSON output with per-copy evidence, coverage gaps, and user summary
- Reads files without executing code or sending network probes
- Reports coverage gaps for unsupported formats and skipped files