
Cloudflare Security Audit Skill
A coding-agent skill that turns your AI agent into a multi-phase security auditor with independently verified, machine-readable vulnerability findings.
At a Glance
About Cloudflare Security Audit Skill
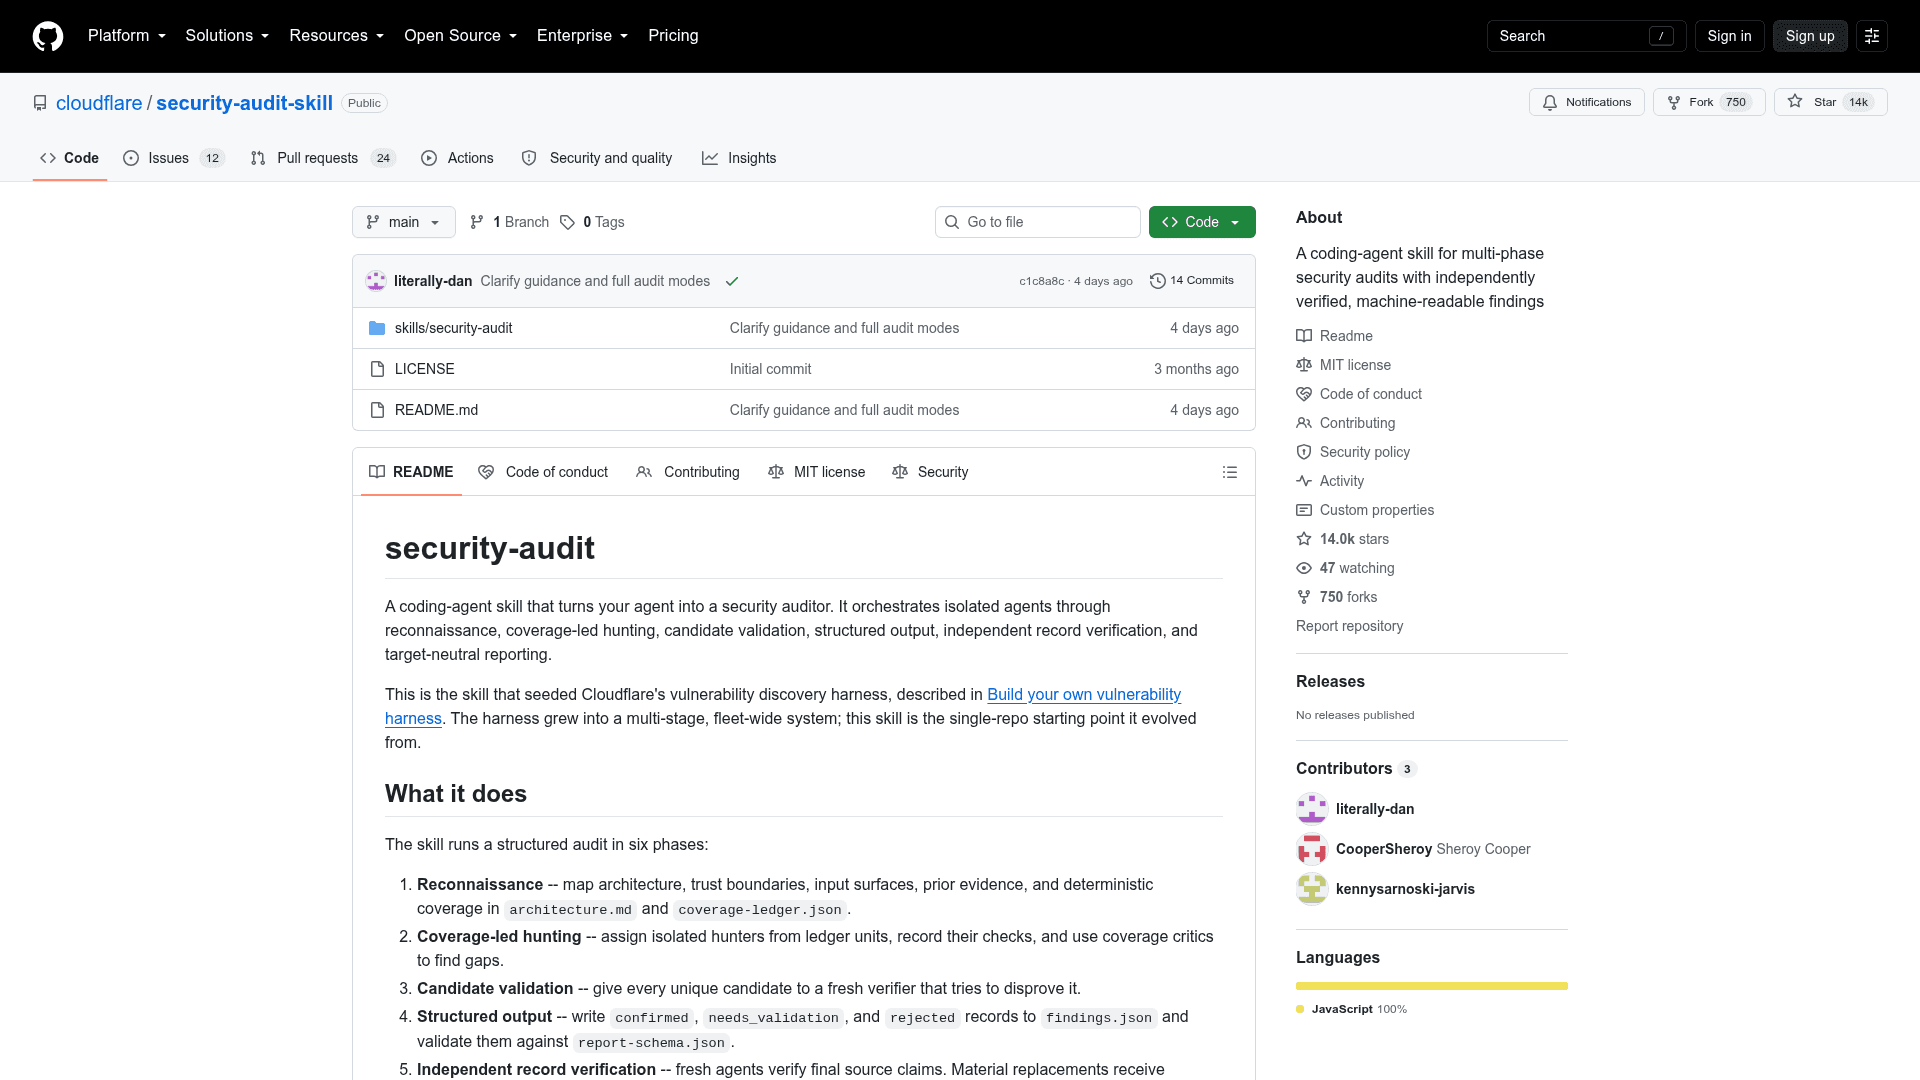
Cloudflare's security-audit-skill is an open-source, MIT-licensed coding-agent skill that orchestrates a structured, multi-phase security audit of any codebase. It was created by Cloudflare's security AI research team and seeded the internal vulnerability discovery harness described in the Cloudflare blog post "Build your own vulnerability harness." The skill is installed via the Skills CLI and activates automatically when a compatible coding agent receives a security audit or vulnerability-finding request.
What It Is
Security-audit-skill is a prompt-and-orchestration package that gives a coding agent a repeatable, adversarially validated security audit workflow. Rather than a single-pass scan, it runs six structured phases—reconnaissance, coverage-led hunting, candidate validation, structured output, independent record verification, and target-neutral reporting—each using isolated sub-agents to prevent confirmation bias. The output is a set of machine-readable JSON findings validated against a bundled schema, plus human-readable Markdown reports.
Six-Phase Audit Workflow
The skill structures every audit into six distinct phases:
- Reconnaissance — maps architecture, trust boundaries, input surfaces, and prior evidence into
architecture.mdandcoverage-ledger.json. - Coverage-led hunting — assigns isolated hunter agents from ledger units, records their checks, and uses coverage critics to surface gaps.
- Candidate validation — each unique candidate is handed to a fresh verifier agent that attempts to disprove it (adversarial validation).
- Structured output — writes
confirmed,needs_validation, andrejectedrecords tofindings.json, validated againstreport-schema.json. - Independent record verification — fresh agents verify final source claims; material replacements receive another independent verifier.
- Target-neutral reporting — derives
REPORT.md,FINDINGS-DETAIL.md, andNEEDS-VALIDATION.mdfrom verified records and the coverage ledger.
Validators (validate-coverage-ledger.cjs and validate-findings.cjs) run automatically at key phase boundaries to enforce schema integrity throughout.
Attack Class Coverage
The skill ships with a comprehensive library of attack-class prompt files covering a wide range of target types:
- Core, wildcard, and obvious-things classes (
ATTACK-CLASSES.md) - Memory safety and binary/kernel targets (
MEMORY-SAFETY-AND-BINARY.md) - AI and LLM targets including prompt injection and agent/tool abuse (
AI-AND-LLM.md) - Web, HTTP protocol, cache, and authentication (
WEB-PROTOCOL-AND-AUTH.md) - Client-side: DOM injection, messaging trust, UI redress, prototype pollution (
CLIENT-SIDE.md) - Supply chain, CI, release, signing, and plugin/extension (
SUPPLY-CHAIN-AND-RELEASE.md) - Cloud and deployment: IAM, IaC, container, serverless, ingress (
CLOUD-AND-DEPLOYMENT.md) - RPC, serialization, queue, broker, webhook, and streaming protocols (
PROTOCOLS-RPC-AND-MESSAGING.md) - Resource exhaustion, quota, and operator-spend (
RESOURCE-EXHAUSTION-AND-AVAILABILITY.md) - Data isolation, tenant separation, cache, export, backup, and deletion (
DATA-ISOLATION-AND-LIFECYCLE.md) - Native app, deep-link, webview, exported components, and local IPC (
DESKTOP-MOBILE-AND-LOCAL-IPC.md)
Design Principles
The skill enforces several opinionated rules to keep findings trustworthy:
- Only confirm established boundary failures. Blocked leads stay as
needs_validationwith an exact unresolved fact rather than being promoted to confirmed. - Adversarial validation. The agent that checks a finding is never the agent that found it.
- Severity requires impact. Likelihood × impact, not deviation from a checklist.
- Defense-in-depth gaps are not vulnerabilities. If Layer A prevents the attack, the absence of Layer B is a hardening note.
- Multiple runs are additive. The skill uses prior ledgers and findings to target gaps and revalidate changed source across runs. The README notes that in Cloudflare's test runs, a single run found roughly half the vulnerabilities that repeated runs found in total.
Setup Path and Requirements
Installation uses the Skills CLI (npx skills add), with an optional --global flag for user-level installation. The skill requires a coding agent whose underlying model supports tool use and parallel sub-agents, Node.js for the zero-dependency validators, and an OS-enforced sandbox for any target-controlled code execution. Without sandbox controls, the workflow keeps leads as needs_validation rather than executing target code. The GitHub repository had over 13,900 stars and 744 forks as of its last recorded update.
Community Discussions
Be the first to start a conversation about Cloudflare Security Audit Skill
Share your experience with Cloudflare Security Audit Skill, ask questions, or help others learn from your insights.
Pricing
Open Source
Fully free and open source under the MIT License. Free to use, modify, and distribute.
- Six-phase structured security audit workflow
- Full attack-class prompt library
- Zero-dependency findings and coverage-ledger validators
- Machine-readable JSON findings with schema validation
- Human-readable Markdown report generation
Capabilities
Key Features
- Six-phase structured security audit workflow
- Adversarial candidate validation with independent verifier agents
- Coverage-led hunting with coverage-ledger tracking
- Machine-readable findings output validated against JSON schema
- Human-readable Markdown reports (REPORT.md, FINDINGS-DETAIL.md, NEEDS-VALIDATION.md)
- Comprehensive attack-class prompt library (AI/LLM, web, cloud, supply chain, memory safety, etc.)
- Zero-dependency findings and coverage-ledger validators (Node.js)
- Additive multi-run support targeting gaps from prior runs
- Automatic skill activation on security audit trigger phrases
- Guidance mode for focused vulnerability questions without full report artifacts
- Sandbox-aware workflow (keeps leads as needs_validation without OS-enforced sandbox)
- Skills CLI installation with global flag support