
Codex Security
OpenAI's application security agent, available as a CLI and TypeScript SDK, for finding, validating, and fixing code vulnerabilities.
At a Glance
The @openai/codex-security CLI and TypeScript SDK are licensed under Apache License 2.0. Scans require OpenAI API credentials (or another supported provider) and Node.js/Python; those usage costs are external.
Engagement
Available On
Alternatives
Listed Oct 2026
About Codex Security
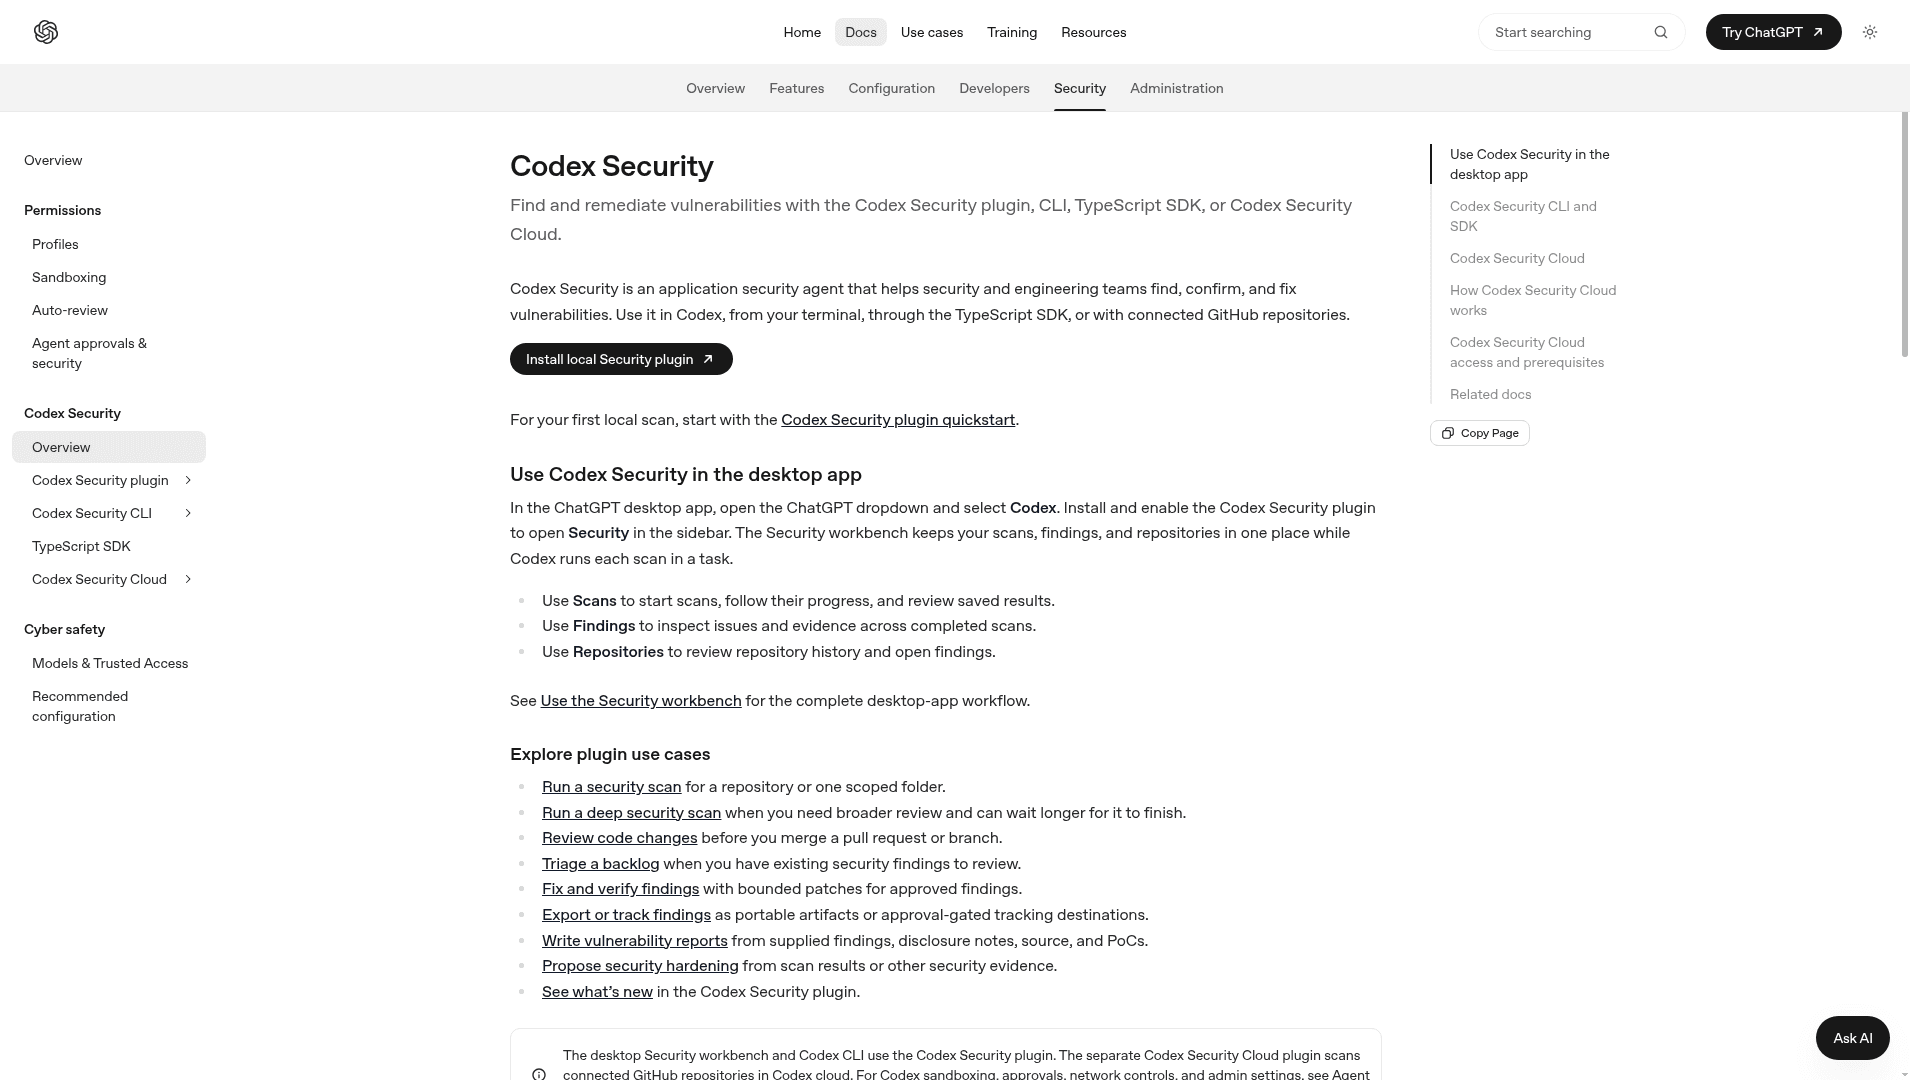
Codex Security is OpenAI's application security agent for security and engineering teams. It is available as a plugin in Codex, a CLI and TypeScript SDK (the @openai/codex-security package), and a Codex Security Cloud plugin for connected GitHub repositories. The CLI and SDK are published as an Apache-2.0 open-source repository.
What It Is
Codex Security scans repositories, selected paths, or Git changes for vulnerabilities, then validates candidate findings, generates patches, and verifies existing fixes. Results can be browsed as saved scans and findings, and the tool can draft SECURITY.md policies and save threat models for later review.
How the Workflow Runs
After installing the CLI with npm and signing in, a scan is started from the repository directory. Scope can be narrowed to specific paths or to committed changes from a base revision, and a deep mode runs parallel discovery workers. Findings can be deduplicated, rated against a custom severity rubric, and matched to suggested owners based on source and Git history. The TypeScript SDK exposes the same scanning so it can be built into applications or developer tools, with progress reporting and cost controls.
Automation and Integrations
The CLI supports bulk, resumable scans across repositories, CI runs including a GitHub Action and GitLab CI/CD, and containerized scans. It can import GitHub code scanning alerts, export SARIF, JSON, or CSV, and publish findings to Linear or a findings service. Scans support OpenAI, Amazon Bedrock, OpenRouter, and Fireworks AI as providers.
Current Status and Access
The docs describe Codex Security Cloud as a research preview, with one-time or continuous scanning of connected GitHub repositories. Running scans requires Codex Security access, and some cybersecurity requests and protected findings require Trusted Access for Cyber approval. The CLI requires Node.js (22.13.0+ within 22.x, or 24.x or 26.x) and Python 3.10+.
Community Discussions
Be the first to start a conversation about Codex Security
Share your experience with Codex Security, ask questions, or help others learn from your insights.
Pricing
Open Source (Apache-2.0)
The @openai/codex-security CLI and TypeScript SDK are licensed under Apache License 2.0. Scans require OpenAI API credentials (or another supported provider) and Node.js/Python; those usage costs are external.
- CLI and TypeScript SDK for finding, validating, and fixing security vulnerabilities
- Scan repositories, selected paths, or Git changes
- Export SARIF, JSON, or CSV
- GitHub Action and containerized bulk scans
- Supports OpenAI, Amazon Bedrock, OpenRouter, and Fireworks AI providers (provider/API costs are external)
Capabilities
Key Features
- Scan repositories, selected paths, or Git changes
- Deep scans with parallel discovery workers
- Validate findings, generate patches, and verify fixes
- Draft SECURITY.md policies and save threat models
- Deduplicate findings, severity rubric assessment, and owner suggestions
- Import GitHub code scanning alerts and export SARIF, JSON, or CSV
- Publish findings to Linear or a findings service
- Bulk resumable scans across repositories
- CI integration with GitHub Action and GitLab CI/CD
- Containerized scans
- TypeScript SDK
- Security workbench in the Codex desktop app
- Codex Security Cloud for connected GitHub repositories