
farol by winninjs
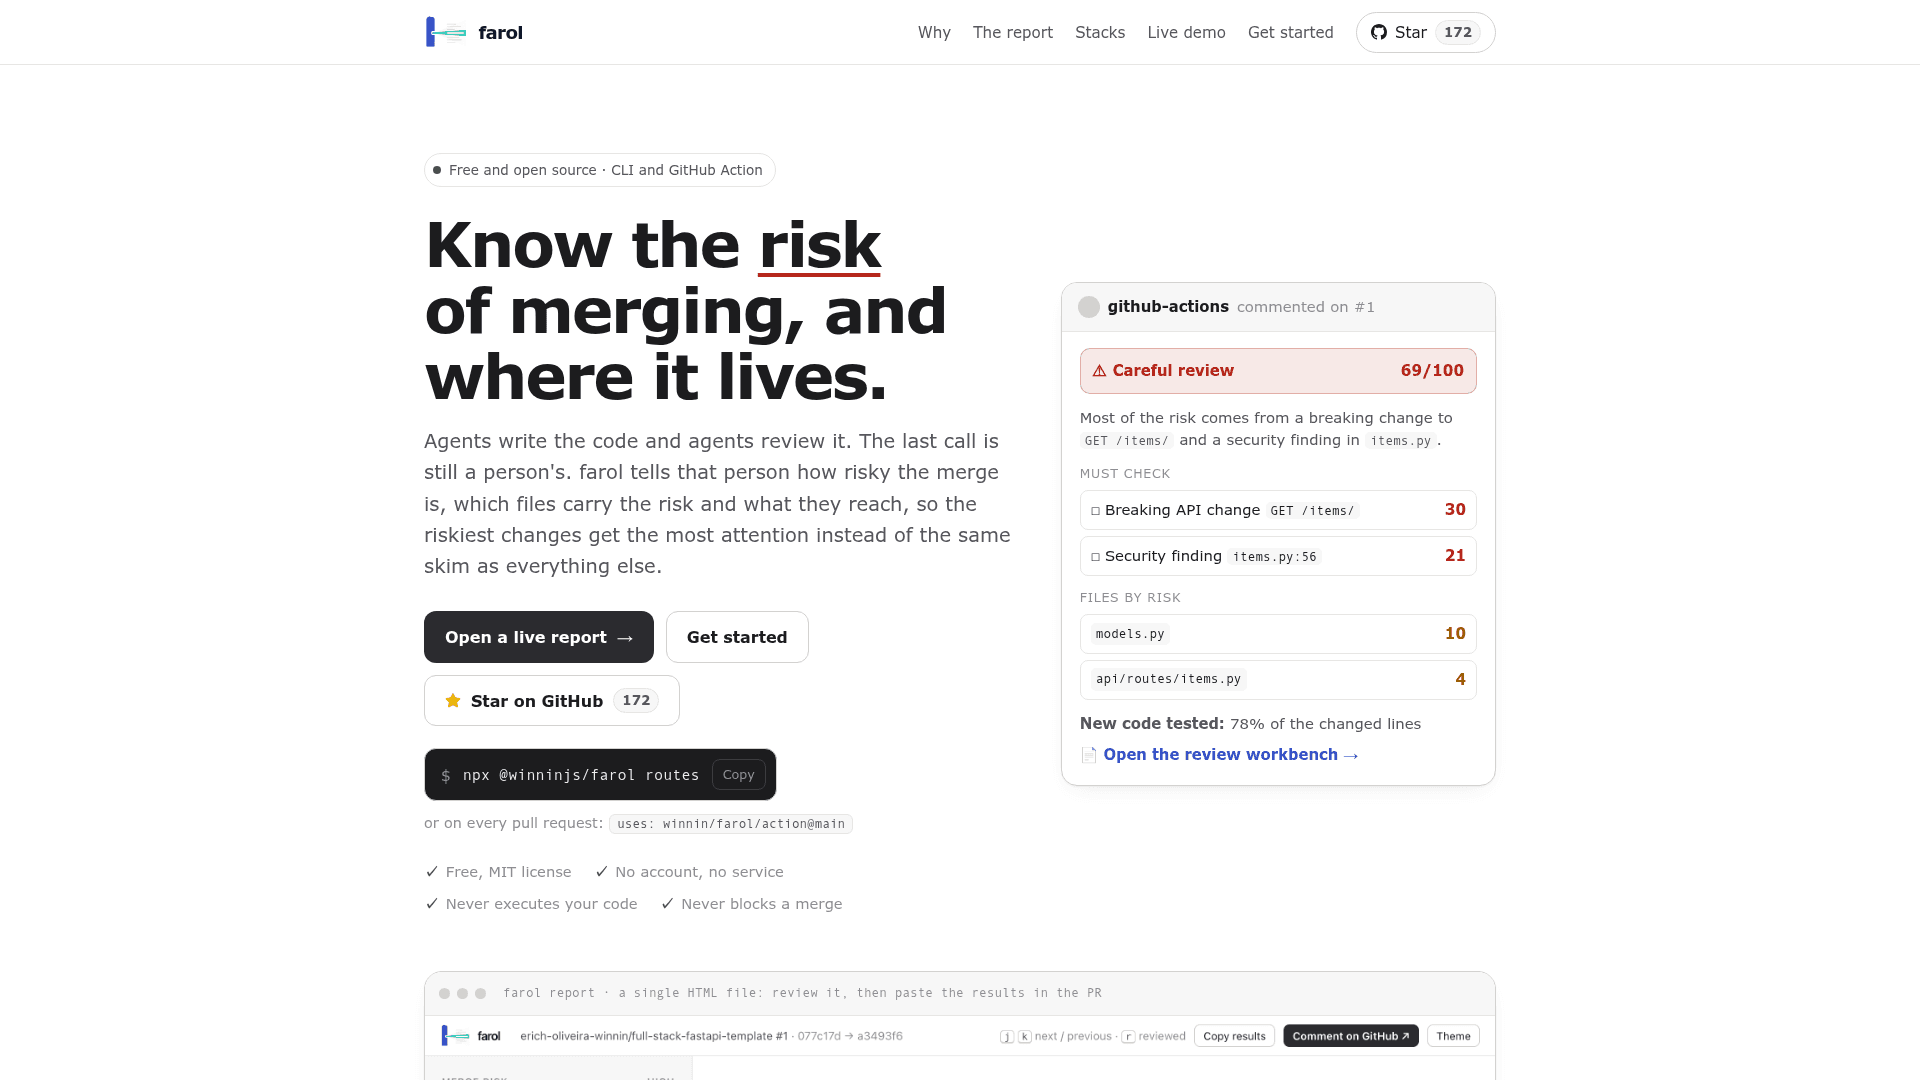
Free, open-source CLI and GitHub Action that scores the risk of merging a pull request and ranks the files that carry it.
At a Glance
About farol by winninjs
farol is a free, MIT-licensed CLI and GitHub Action from Winnin that analyzes a pull request and tells the approving reviewer how risky the merge is and which files carry the risk. It uses static analysis of TypeScript/React, Go and Python code, produces a 0-100 risk score with a verdict, and writes a single-file HTML report plus a PR comment. The latest listed release is v0.2.1.
What It Is
farol is a pull request triage tool meant to run after an AI review and before a human approval. It diffs the merge-base against the head, reads both trees without executing code, and builds a graph of which declaration uses which. From each changed declaration it finds the entry points (pages, API operations, RPC methods, jobs, scripts) that run it. The result is a verdict (fast track, quick review or careful review), a risk score, and a ranked list of files to read first.
The Report Workbench
The HTML report is an interactive review workbench. A merge risk score drops as the reviewer ticks files as read or confirms findings. A Must check list collects breaking API changes, security findings, lint errors and vulnerable dependencies. Files are grouped by risk tier with their diffs, and lines no test ran are marked. The report also shows diff coverage, the pages and endpoints the change can affect, suggested reviewers from git history and CODEOWNERS, and a copyable Markdown summary of results for the PR. After a push, a second report covers only the new commits.
Supported Stacks and Inputs
For TypeScript it reads React Router, Next.js and TanStack Router frontends, plus GraphQL and REST backends. For Go it reads chi, gin, echo and net/http routes and gRPC methods. For Python it reads FastAPI, Flask, Django, Celery, Temporal, Prefect and MCP entry points. It consumes the coverage, lint and audit reports a CI already produces, such as Istanbul, go test profiles, coverage.py, ESLint, golangci-lint, ruff, npm audit, govulncheck and pip-audit. Datadog traffic and error data can optionally be added as information that does not change the score.
Safety Model
The project states that analysis never executes the analyzed code and never uses the network, apart from the GitHub comment step and the optional Datadog read. It runs in shadow mode: it informs reviewers and never approves, requests changes or fails a check. When part of a change cannot be read, it reports unknown and asks for a careful review. Setup needs Node.js 22+ and git, plus Go or Python 3.11+ for those projects.
Community Discussions
Be the first to start a conversation about farol by winninjs
Share your experience with farol by winninjs, ask questions, or help others learn from your insights.
Pricing
Free (MIT open source)
Free, MIT-licensed CLI and GitHub Action; no account, hosted service, or paid tier.
- CLI via npx @winninjs/farol
- GitHub Action winnin/farol/action
- MIT license
- No account or hosted service
- Never executes your code
Capabilities
Key Features
- Merge risk score (0-100) with fast track, quick review and careful review verdicts
- Reach analysis from changed declarations to affected pages, endpoints, jobs and scripts
- Files ranked by risk with diffs and untested lines marked
- Diff coverage from existing CI coverage reports
- Breaking API contract detection for GraphQL, FastAPI, Go handlers and gRPC
- Security, lint and vulnerable dependency findings in a Must check list
- Single-file interactive HTML report and GitHub PR comment
- Incremental report covering only commits since the last push
- Suggested reviewers from git blame and CODEOWNERS
- Optional Datadog traffic and error data
- Fails closed with unknown when code cannot be read
- Shadow mode that never blocks a merge