
Gondolin
Local Linux micro-VMs with programmable network and filesystem control for sandboxing AI agents.
At a Glance
About Gondolin
Gondolin is an open-source agent sandbox built by Earendil. It runs generated code inside fast local Linux micro-VMs (libkrun where available, QEMU otherwise) while keeping network and filesystem access under host-side policy that can be customized in JavaScript. The project is described by its docs as early and experimental, with a CLI and a TypeScript SDK.
What It Is
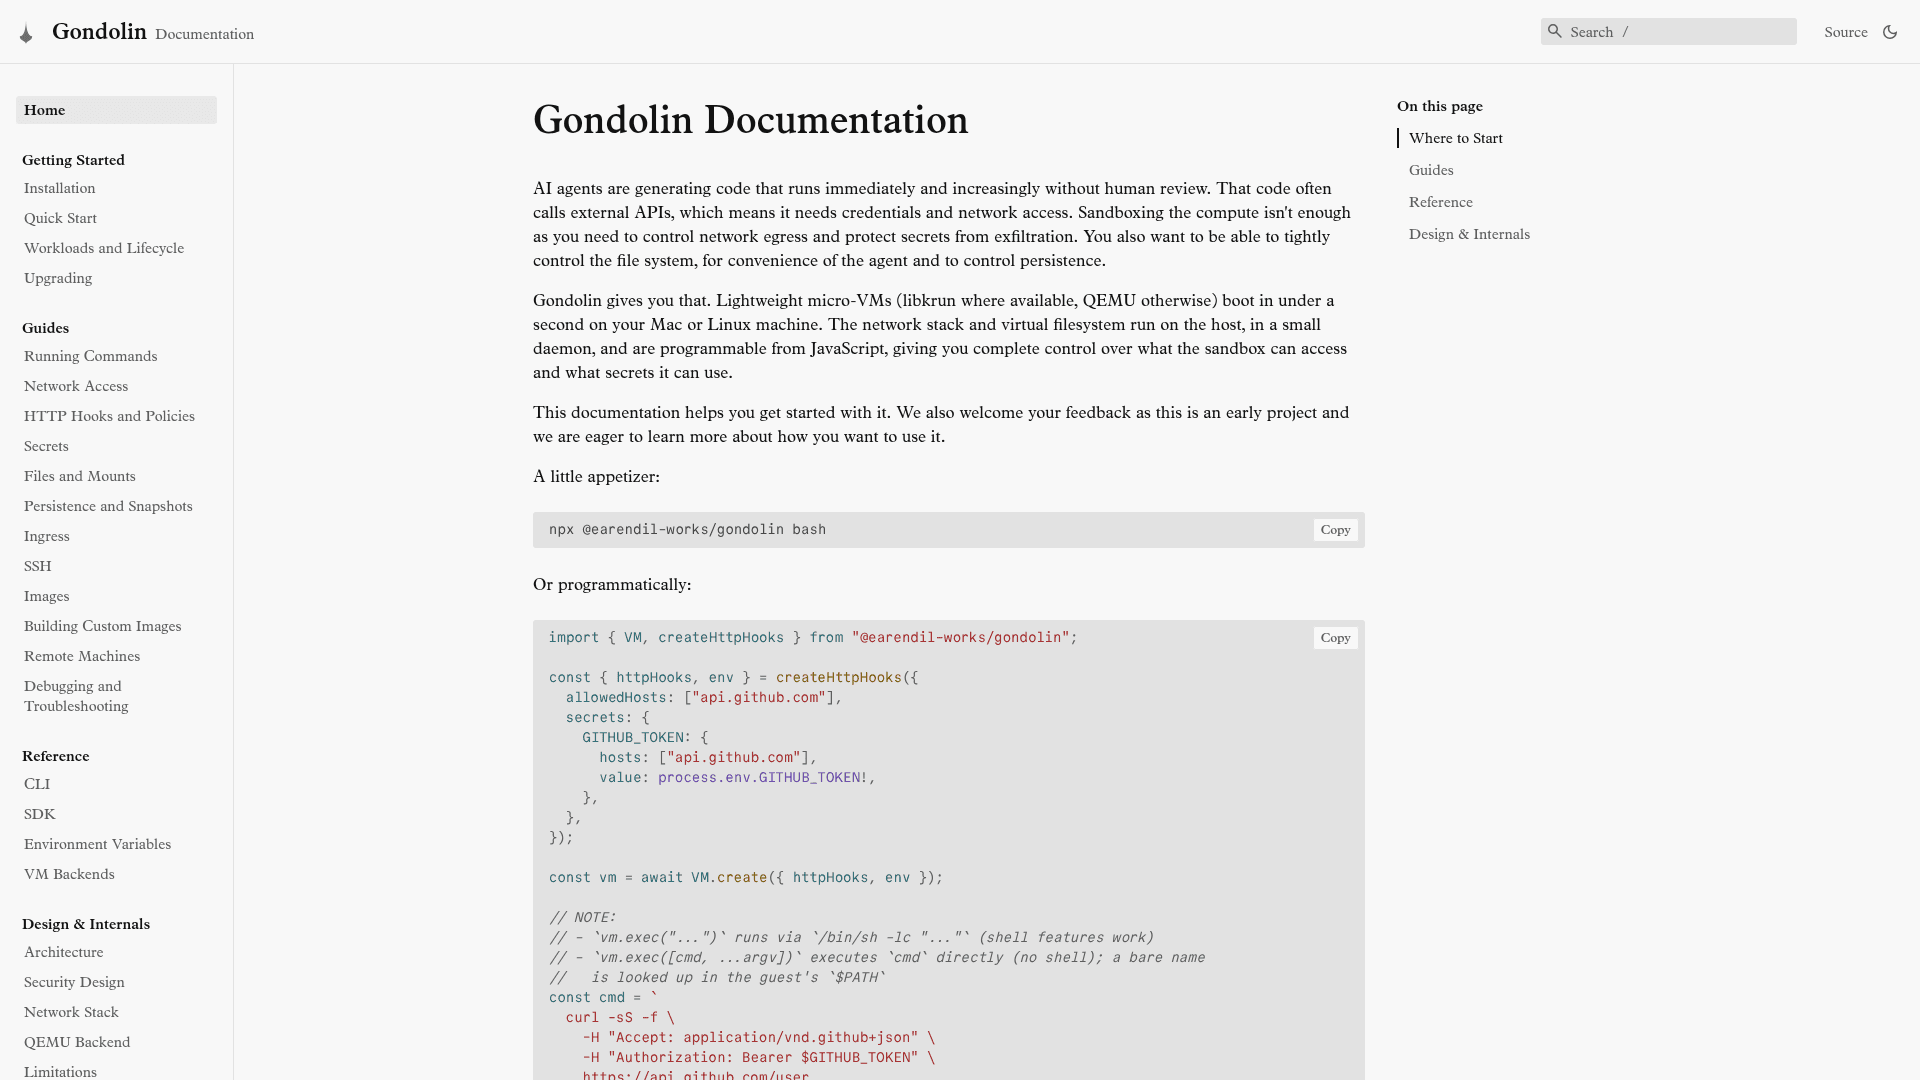
Gondolin addresses the case where AI agents run generated code without human review and that code needs network access and credentials. Instead of sandboxing only compute, it puts egress, secrets and the virtual filesystem under control of a small host-side daemon. Users start a shell with the CLI or create VMs programmatically with the SDK, run commands with vm.exec(), and read exit code, stdout and stderr.
Network and Secret Control
HTTP and TLS egress is governed by host allowlists and request/response hooks. Secrets are injected through placeholders: the guest sees only a placeholder token, and the host substitutes the real value for allowed destinations. DNS behavior can be set to synthetic, trusted or open modes. Policies can also be written as self-contained JavaScript that runs inside the daemon.
Filesystem, Persistence and Access
Host directories can be mounted, and programmable VFS mounts let custom filesystem behavior be written in JavaScript. Rootfs modes include readonly, memory and cow, and disk checkpoints support snapshots and resume. An ingress gateway exposes guest HTTP services on the host, SSH is supported in both directions with allowlisted upstreams, and custom images can be built from an Alpine-based pipeline.
Setup Path
Run npx @earendil-works/gondolin bash for a first shell. Guest images of roughly 200MB or more are downloaded on first use and cached. Node.js 22.19 or newer is required, and QEMU is needed only on hosts that cannot use krun. Remote machines are supported by running the daemon elsewhere while policy and credentials stay local. Examples include a Pi extension and a Browser Use example running Chromium in a micro-VM.
Community Discussions
Be the first to start a conversation about Gondolin
Share your experience with Gondolin, ask questions, or help others learn from your insights.
Pricing
Open Source
Self-hosted, local Gondolin core (micro-VM sandbox with programmable network and filesystem control) under the Apache-2.0 license.
- Licensed under Apache License 2.0
- Local Linux micro-VMs (libkrun or QEMU)
- Programmable HTTP/TLS egress policy and secret injection
- Programmable VFS mounts, ingress gateway, SSH support
- Disk checkpoints (snapshots) and custom image builds
Capabilities
Key Features
- Local disposable micro-VMs for agent tasks
- Programmable HTTP/TLS egress policy with allowlists and hooks
- Placeholder-based secret injection without guest exposure
- Programmable VFS mounts in JavaScript
- Ingress gateway for guest HTTP services
- Attach a shell to a running VM
- SSH access host-to-guest and allowlisted guest-to-upstream
- Disk checkpoints and snapshot resume
- Custom image builds
- Remote machines via static Rust daemon
- Daemon-side JavaScript policies
- Configurable DNS modes and rootfs modes