
HOL Guard
Local-first runtime security layer that checks AI coding agent commands, secret access, MCP calls and package installs before they run.
At a Glance
Free local protection forever; Guard Local core is open source under Apache-2.0. No credit card required.
Engagement
Available On
Listed Nov 2026
About HOL Guard
HOL Guard is a local-first runtime security layer for AI agents, built by HOL (Hashgraph Online). On supported integrations it checks risky actions such as shell commands, tool calls, package installs and configuration changes before they run, then allows, asks or blocks them and keeps a local record. Its core Guard Local runtime is open source under Apache-2.0 and runs on the developer machine without a cloud account.
What It Is
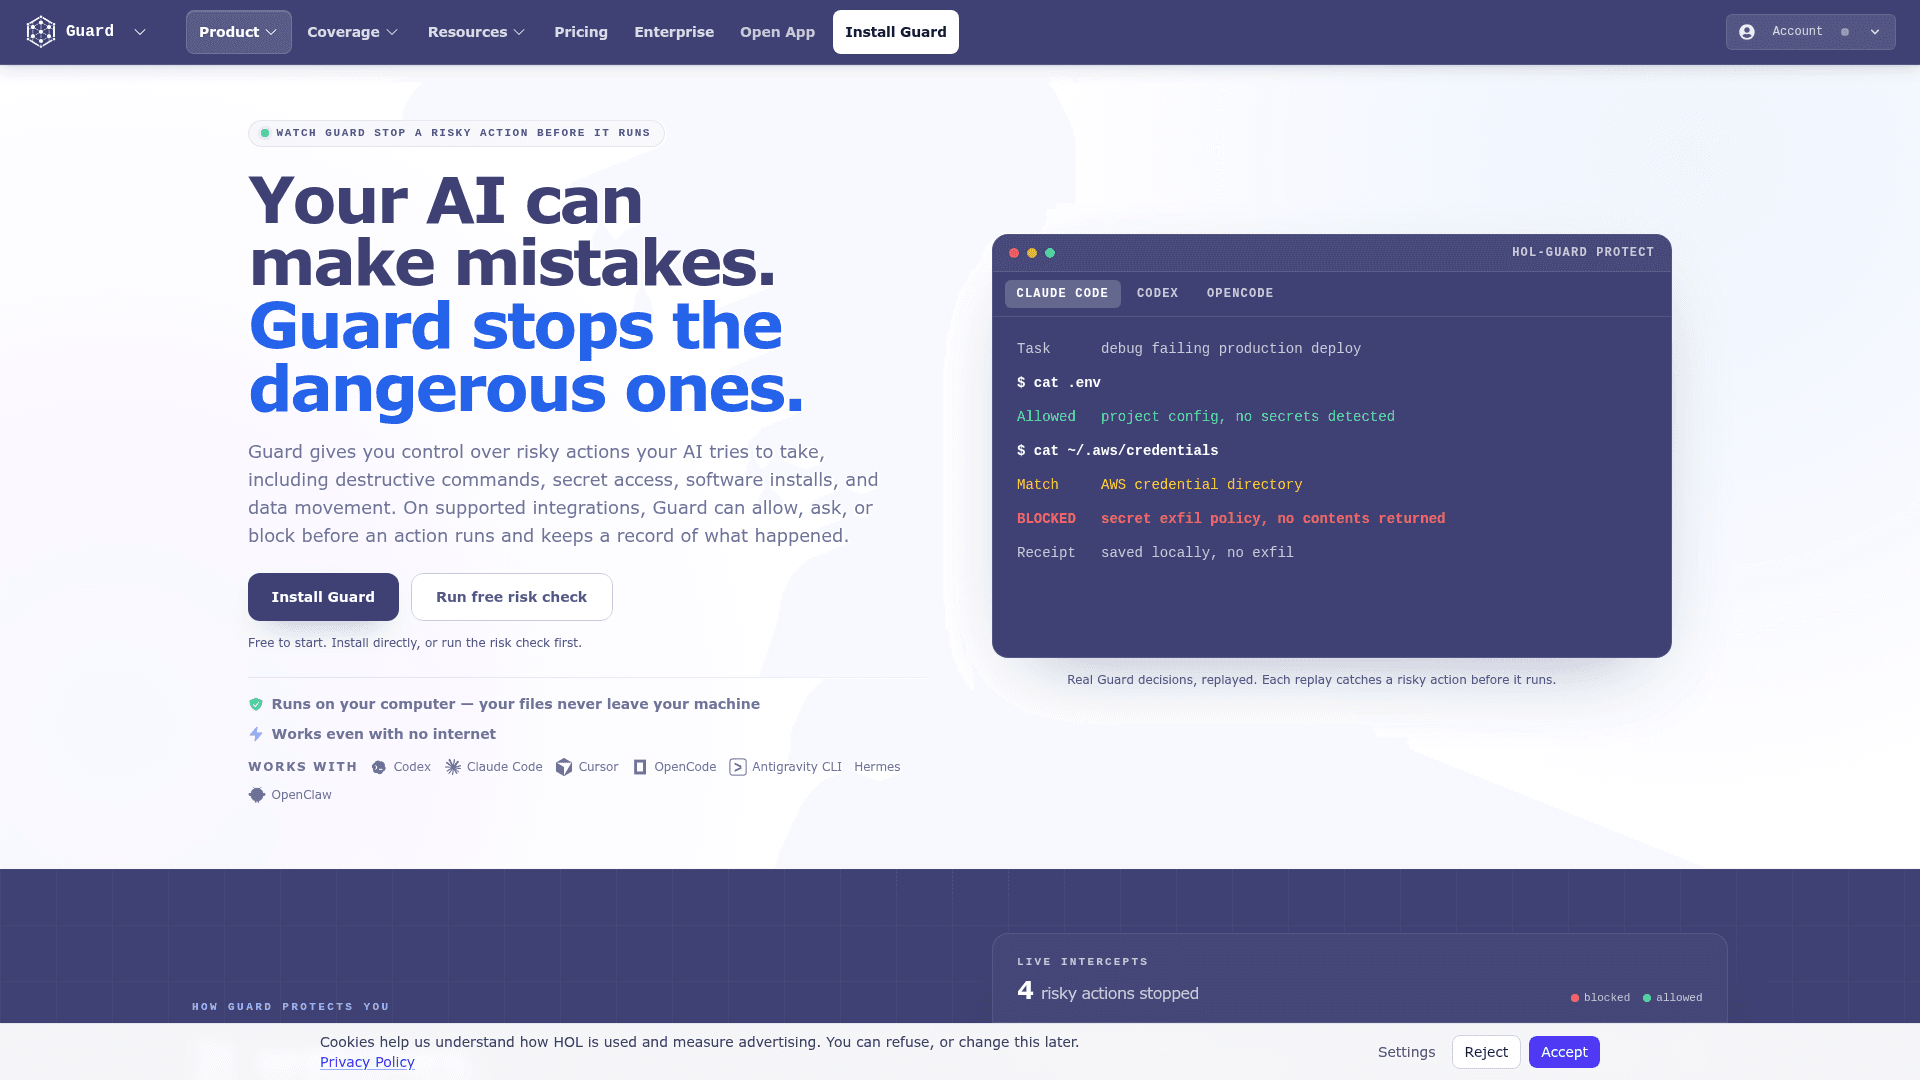
Guard sits between a coding agent and the machine it runs on. Routine work such as running tests goes through, new or ambiguous actions such as a first package install pause for approval, and clearly dangerous actions such as reading cloud credentials or sending a .env file to a remote host are blocked. Each decision is saved as a local receipt. Guard is described by HOL as not a cloud MCP gateway, not a network firewall, and not a complete prompt-injection preventer. It reduces impact at supported action boundaries.
Coverage and Protection Model
HOL says Guard protects supported workflows against secret and credential exposure, destructive commands, prompt-injection-driven actions, malicious or changed packages, risky MCP configuration, and unsafe plugins, skills, hooks and agent settings. Supported agents listed include Codex, Claude Code, Cursor, OpenCode, Antigravity CLI, Hermes, OpenClaw, GitHub Copilot CLI, Antigravity, Kimi, Grok, Pi / Oh My Pi and Zcode. Enforcement depth varies by agent and event type, so a public coverage matrix states what is blocked, reviewed, observed or not covered.
Setup Path
Installation is a one-line shell command for macOS or Linux that pipes the install script from hol.org into bash, with an option to configure a specific agent such as Cursor and verify the install. After installing, users run hol-guard init. A free risk check is also offered before installing.
Guard Local and Guard Cloud
Guard Local enforces policy on the developer machine and keeps working offline. Guard Cloud is an optional, separate service that adds synchronized evidence, shared policy, fleet visibility and team dashboards; HOL states cloud connectivity is for visibility and coordination, not enforcement.
For Plugin Maintainers
HOL also publishes plugin-scanner and a GitHub Action that validate plugins, skills and MCP configuration in CI, checking manifests, MCP transport hardening and skill-level issues such as prompt injection markers and dangerous shell commands. HOL's site lists v3.58.0 as the latest Guard release, dated October 27, 2026.
Community Discussions
Be the first to start a conversation about HOL Guard
Share your experience with HOL Guard, ask questions, or help others learn from your insights.
Pricing
Free
Free local protection forever; Guard Local core is open source under Apache-2.0. No credit card required.
- Local scanning and command interception
- On-device decisions and change diffs
- First-use protection and local policy
- Full offline support
- Local runtime, real-time approval prompts, local audit log
Solo
Personal Guard Cloud memory across two devices.
- 2 cloud-connected devices
- 30 days cloud retention
- 1 GB included cloud storage
- Weekly personal security digest
- Matched critical advisories
- Monitors up to 5 selected GitHub repositories
- 250 credential validity checks per month
- One custom detector
Pro
Longer history, instant alerts, full evidence; a free trial is offered via CTA.
- 5 cloud-connected devices
- 180 days cloud retention
- 5 GB included cloud storage
- Real-time activity alerts
- Policy versioning and rollback
- Advanced search and full evidence
Team
Shared policy and team workflows, priced per seat.
- Up to 25 cloud-connected devices
- 365 days cloud retention
- 25 GB + 5 GB/seat cloud storage
- Organization module policy
- Shared policy and team workflows
Contact sales
Enterprise security requirements review with commercial terms confirmed per deployment.
- Enterprise identity and access review
- Redacted evidence export via webhook
- Custom threat-feed requirements review
- Volume pricing and support planning
- Self-hosted / VPC deployment review
Capabilities
Key Features
- Pre-execution review of shell commands, tool calls, package installs and config changes
- Allow, ask or block decisions on supported integrations
- Secret and credential exfiltration protection
- MCP configuration and server risk review
- Local decision receipts and evidence trail
- Works offline without a cloud account
- Support for 13 coding agents
- Optional Guard Cloud for shared policy and team dashboards
- plugin-scanner and GitHub Action for maintainer CI checks