
nix-opencode-with-mitm
A Nix flake that runs opencode in a network-isolated jail with all traffic tunneled through an allow-listing mitmproxy.
At a Glance
Engagement
Available On
Listed Nov 2026
About nix-opencode-with-mitm
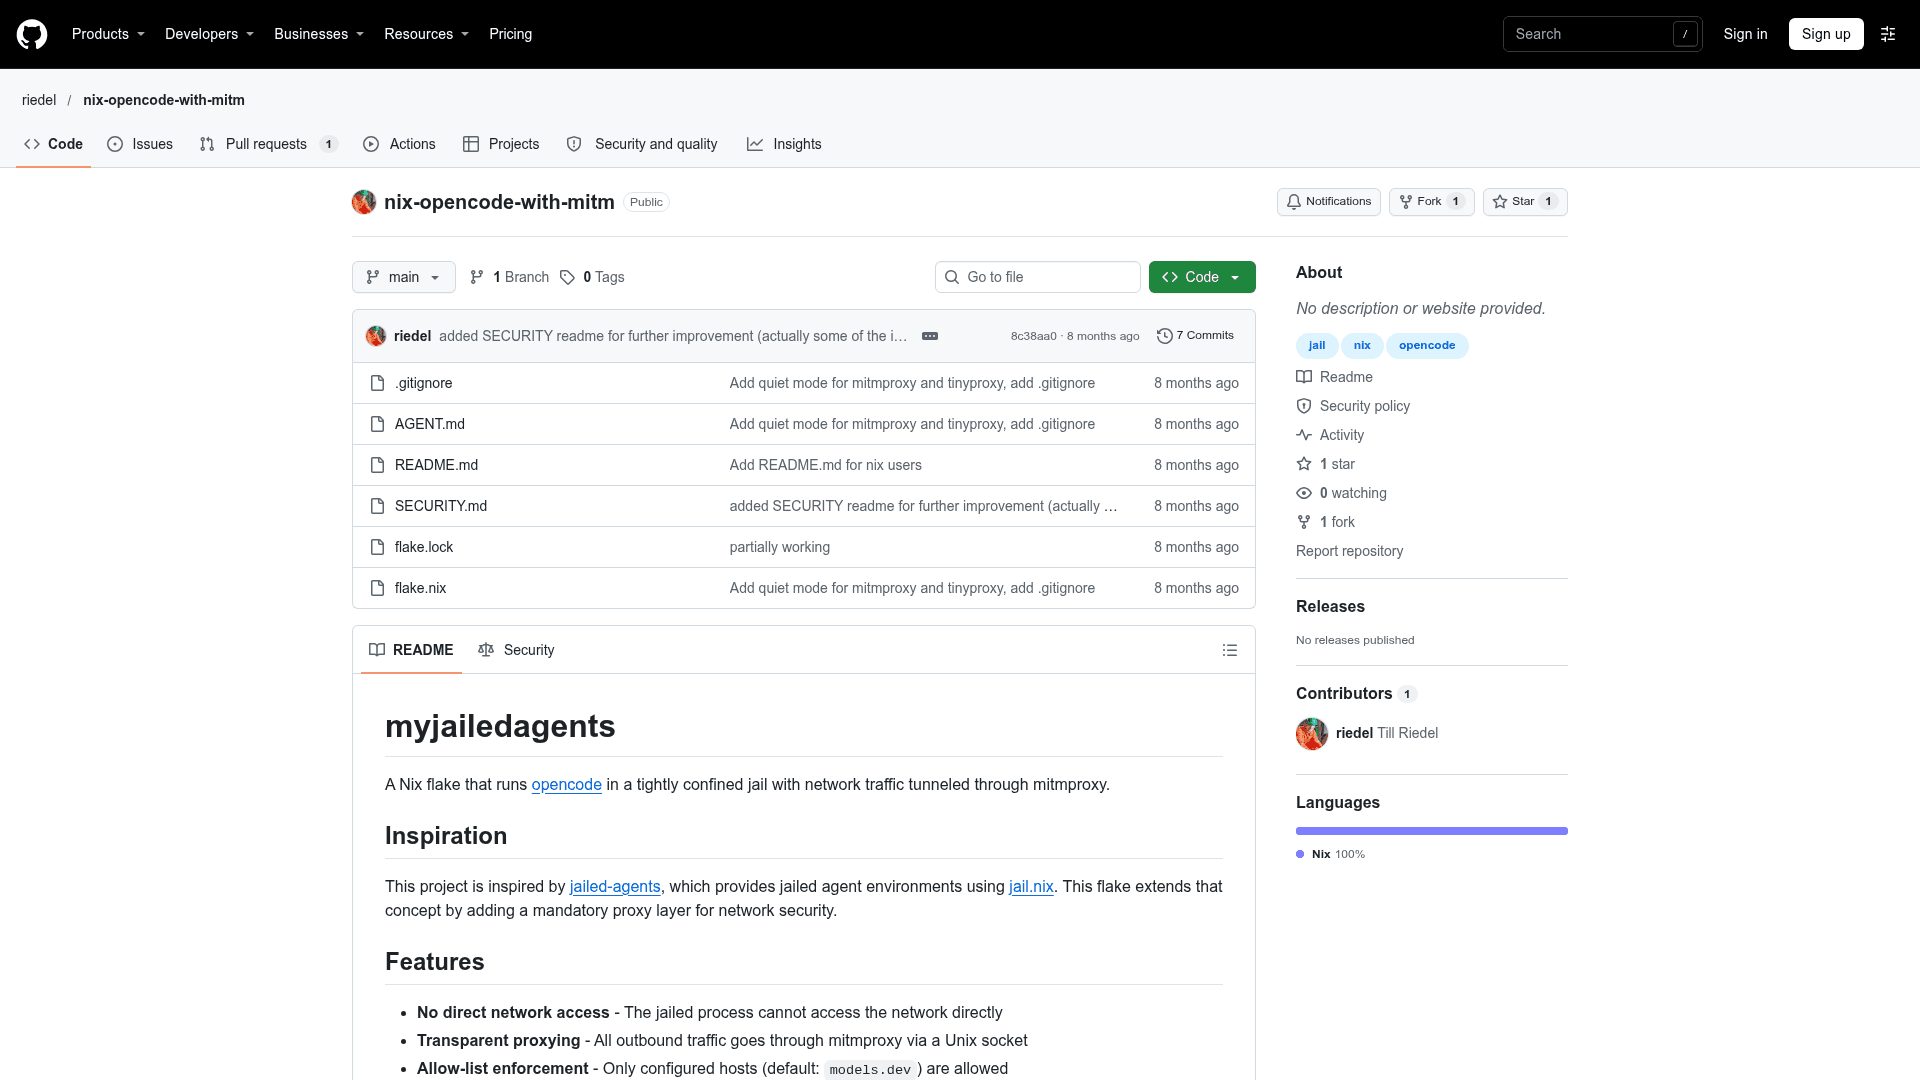
nix-opencode-with-mitm (README title: myjailedagents) is a Nix flake published on GitHub by riedel. It runs the opencode coding agent inside a confined jail that has no direct network access, routing outbound traffic through mitmproxy on the host.
The project is inspired by jailed-agents, which uses jail.nix, and adds a mandatory proxy layer for network control.
What It Is
This is a sandboxing wrapper for opencode, built and run with Nix. Users build the flake or use nix run to launch the opencode-with-mitm binary. The agent runs in a jail created with jail.nix that has no network namespace, so it cannot reach the network directly.
How the proxy path works
A host-side mitmproxy listens on a Unix socket, enforces a host allow-list, and terminates TLS. Inside the jail, HTTP_PROXY points to tinyproxy, which forwards through ip2unix to that socket. CA trust is configured for Node.js. Because the jail has no DNS, allowed hosts are pre-resolved through /etc/hosts.
Configuration
The allow-list is set with the MITM_ALLOW_HOSTS environment variable as a space-separated list, defaulting to models.dev. MITM_PORT sets the proxy port, defaulting to 8000. DEBUG=1 shows mitmproxy and tinyproxy output. OPENCODE_DISABLE_JAIL=1 runs opencode without the jail for debugging.
Community Discussions
Be the first to start a conversation about nix-opencode-with-mitm
Share your experience with nix-opencode-with-mitm, ask questions, or help others learn from your insights.
Pricing
Licensing Unpublished
The flake is available in a public GitHub repository. The maintainer hasn’t published a software price or license. Charges from the model you use with OpenCode are separate.
- Nix flake for sandboxing OpenCode
Capabilities
Key Features
- Jailed opencode with no direct network access
- All outbound traffic proxied through mitmproxy via a Unix socket
- Configurable host allow-list (default models.dev)
- TLS inspection with CA trust configured for Node.js
- Allowed hosts pre-resolved via /etc/hosts
- Debug output mode
- Option to disable jail for debugging