GuardRail
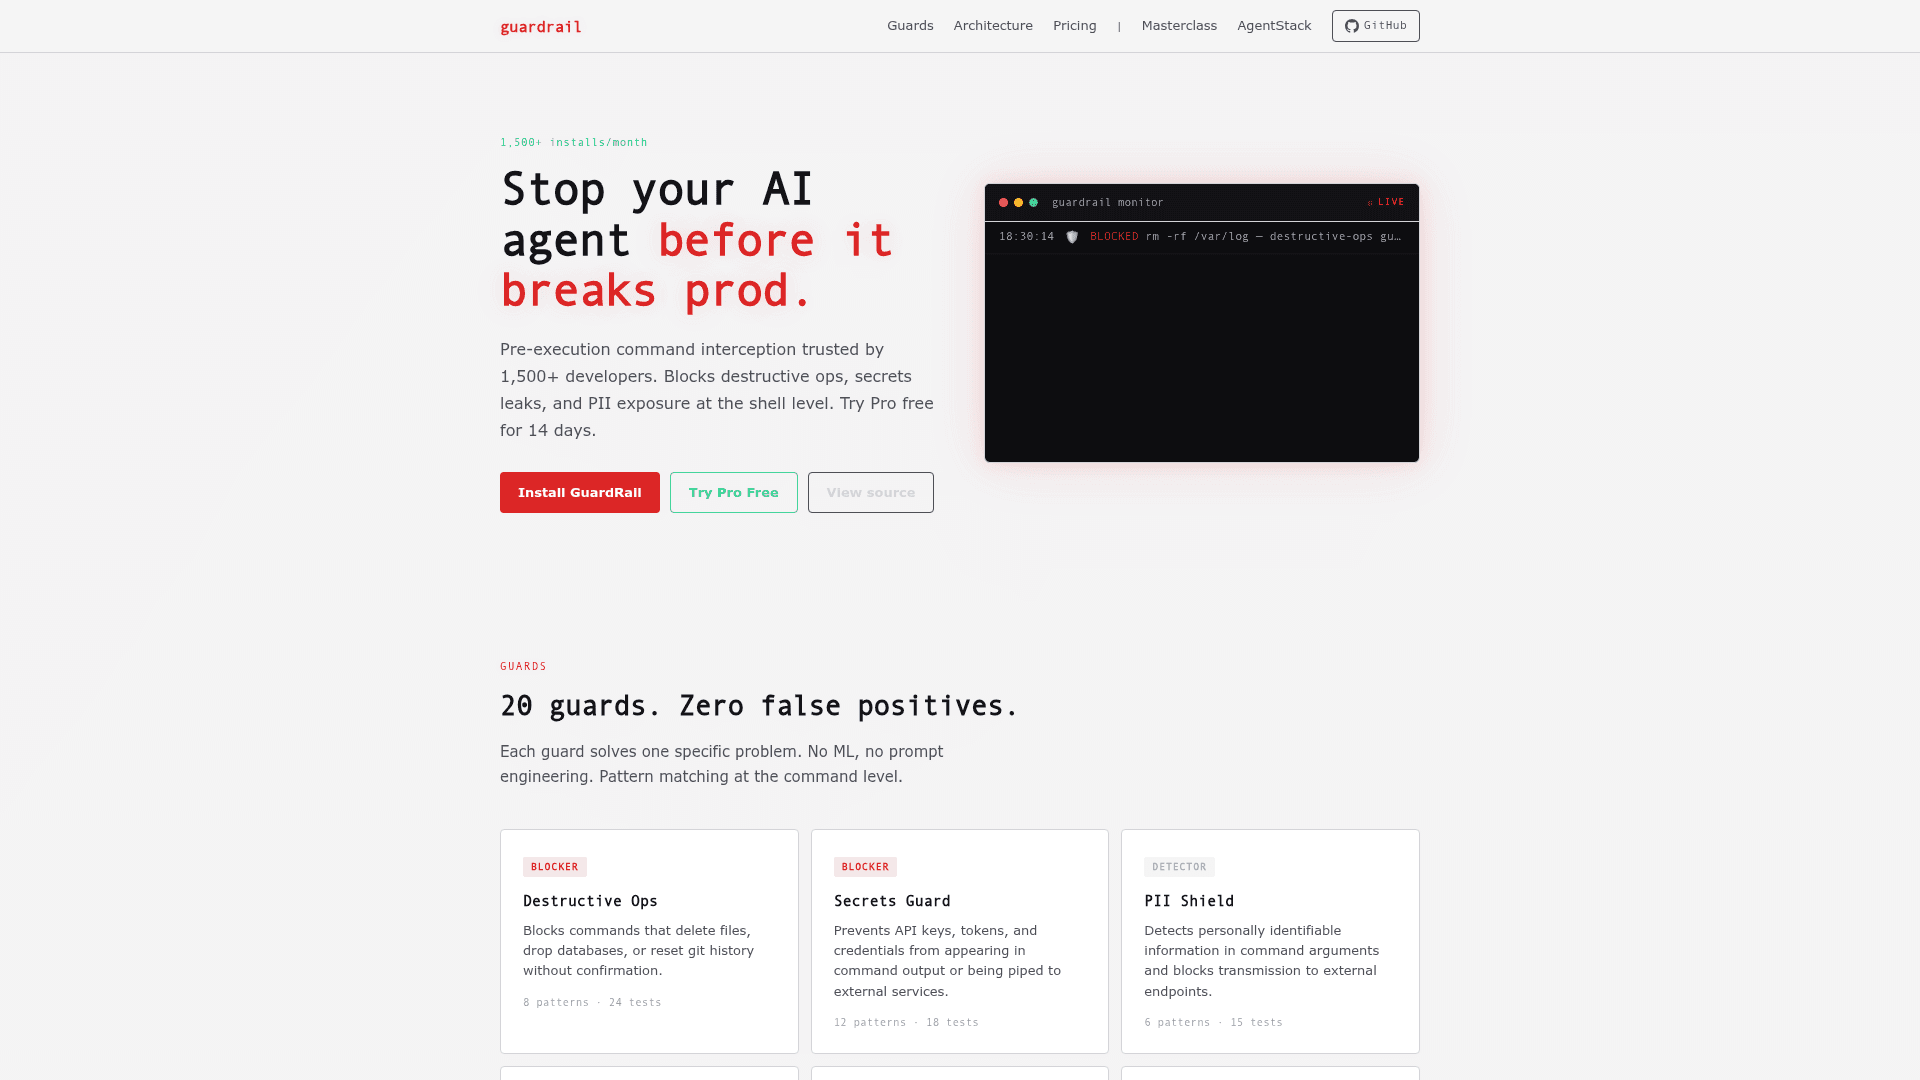
Pre-execution security for AI coding agents that intercepts shell commands before they run, blocking destructive operations, secrets leaks, and PII exposure.
At a Glance
For individual developers. 13 free MIT-licensed core guards.
Engagement
Available On
Alternatives
Listed Sep 2026
About GuardRail
GuardRail is an open-source, MIT-licensed security tool built by Prompt & Build that hooks into AI coding agents at the shell level to block dangerous commands before they execute. It ships 13 free core guards covering destructive file operations, SQL mass-deletes, secrets exfiltration, PII exposure, and agent self-bypass attempts — all running in under 1ms per guard with no ML or API calls in the path.
What It Is
GuardRail sits between an AI coding agent (such as Claude Code) and the operating system shell. Every command the agent attempts passes through a pre-execution dispatcher that pattern-matches against a set of guard rules. If a rule fires, the command is blocked and returns a non-zero exit code with a clear message; the agent never executes the dangerous operation. A post-execution dispatcher scans command output for environment variable dumps, prompt injection attempts, and error-swallowing patterns. The result is a deterministic, fail-closed enforcement layer that requires only bash 4+ and jq — no Python, no cloud API, no LLM in the decision path.
How the Guard Architecture Works
Guards are bash functions organized into two dispatchers:
- Pre-Bash Dispatcher — runs before every shell command; blockers halt execution, detectors warn
- Pre-Write Dispatcher — intercepts file-tool writes (Write / Edit / MultiEdit) to guard against credential injection and self-modification
- Post-Bash Dispatcher — scans command output after execution for PII, injection patterns, and runaway loops
The 13 free core guards cover: direct pushes to protected branches, PII and secret exfiltration via curl/wget, recursive deletion on protected paths, firewall flush commands, stopping critical services, SQL UPDATE/DELETE without WHERE clauses, and agent self-bypass via gate files. Each guard has a corresponding test suite; the README lists 103 tests passing with zero false positives according to the project's own pentest framework.
Deployment Model and Setup Path
Installation is a single npx guardrail-agent init command that backs up existing shell settings and registers the hook. The CLI provides guardrail status, guardrail pentest, guardrail disable/enable, and guardrail uninstall for clean removal. Configuration lives in ~/.guardrail/guardrail.config.sh and exposes variables for protected database tables, git branches, filesystem paths, critical services, wandering thresholds, and tool-call budgets. Custom guards can be scaffolded with guardrail new <name>, which generates a template and matching test. The project states requirements of bash 4+, jq, and openssl on Linux or macOS, with native hook support for Claude Code and planned adapters for Codex CLI, Gemini CLI, Aider, and Continue.dev.
Open-Source Core with Pro Extension
The 13 core guards are MIT-licensed and free forever. A Pro tier adds 48 additional guards derived from real production incidents, including script content analysis (to catch payload-in-file bypass patterns), multi-step attack detection, ML-powered PII Shield covering 10 EU countries, supply chain audit for npm installs, and an EU AI Act compliance kit with guard-to-article mapping and PDF audit reports. An Enterprise tier adds SSO/RBAC integration, dedicated support with a 24-hour SLA, and compliance audit report exports. The project also offers a one-time AI Governance Starter Kit and a KI-Governance Masterclass with 30 lessons on the GRIP framework.
Update: v0.4.6 / v0.3.1 Release
The GitHub repository shows the latest published release as v0.3.1 (August 14, 2026), while the CLI status output in the README displays v0.4.6, indicating active development between tagged releases. The repository was created in July 2026 and last pushed in September 2026. The project describes its guard patterns as extracted from a private production system that has run AI coding agents across 13 applications, with the README noting the system carries 177 guards in its private form and the public package ships the universal subset. The project is part of a five-tool AgentStack suite also including Model Router, NightShift, Graphify Toolkit, and Autonomie OS.
Community Discussions
Be the first to start a conversation about GuardRail
Share your experience with GuardRail, ask questions, or help others learn from your insights.
Pricing
Community
For individual developers. 13 free MIT-licensed core guards.
- 13 built-in guards (20 on website, 13 per README)
- Secrets + PII detection
- Git safety guards
- Audit trail
- Community support
Pro
For teams running agents in production. 48 guards from real incidents.
- 48 guards from 14 months of real incidents
- Everything in Community
- PII Shield (10 EU countries)
- EU AI Act compliance reports
- Multi-step attack detection
- PEN-test framework (50+ patterns)
- Priority support (48h SLA)
Enterprise
For organizations with compliance needs.
- Everything in Pro
- EU AI Act compliance pack
- SSO + RBAC integration
- Compliance audit reports
- Dedicated support (24h SLA)
AI Governance Starter Kit
One-time template pack: 20 production-tested guards, 4 skill runbooks, dispatcher templates, and a complete CLAUDE.md.
- 20 guards
- 3 dispatchers
- 4 skills
- CLAUDE.md template
- settings.json example
- Customization guide
Capabilities
Key Features
- Pre-execution shell command interception
- 13 free MIT-licensed core guards
- 48 Pro guards for production teams
- Destructive operations blocking (rm -rf, DROP, DELETE without WHERE)
- Secrets and API key exfiltration prevention
- PII detection and blocking
- Git safety guards (force push, push to main)
- Agent self-bypass detection
- Post-execution output scanning for injection and PII
- Audit trail with timestamped, hashed log entries
- Wandering/loop detection
- Tool call budget enforcement
- Custom guard scaffolding via CLI
- Built-in pentest framework (50+ attack patterns)
- EU AI Act compliance reports (Pro)
- Zero ML or API calls in decision path
- Sub-1ms per guard latency
- HMAC-signed tokens for bypass prevention
- Works with Claude Code natively
- Single-command install and clean uninstall