Pipelock
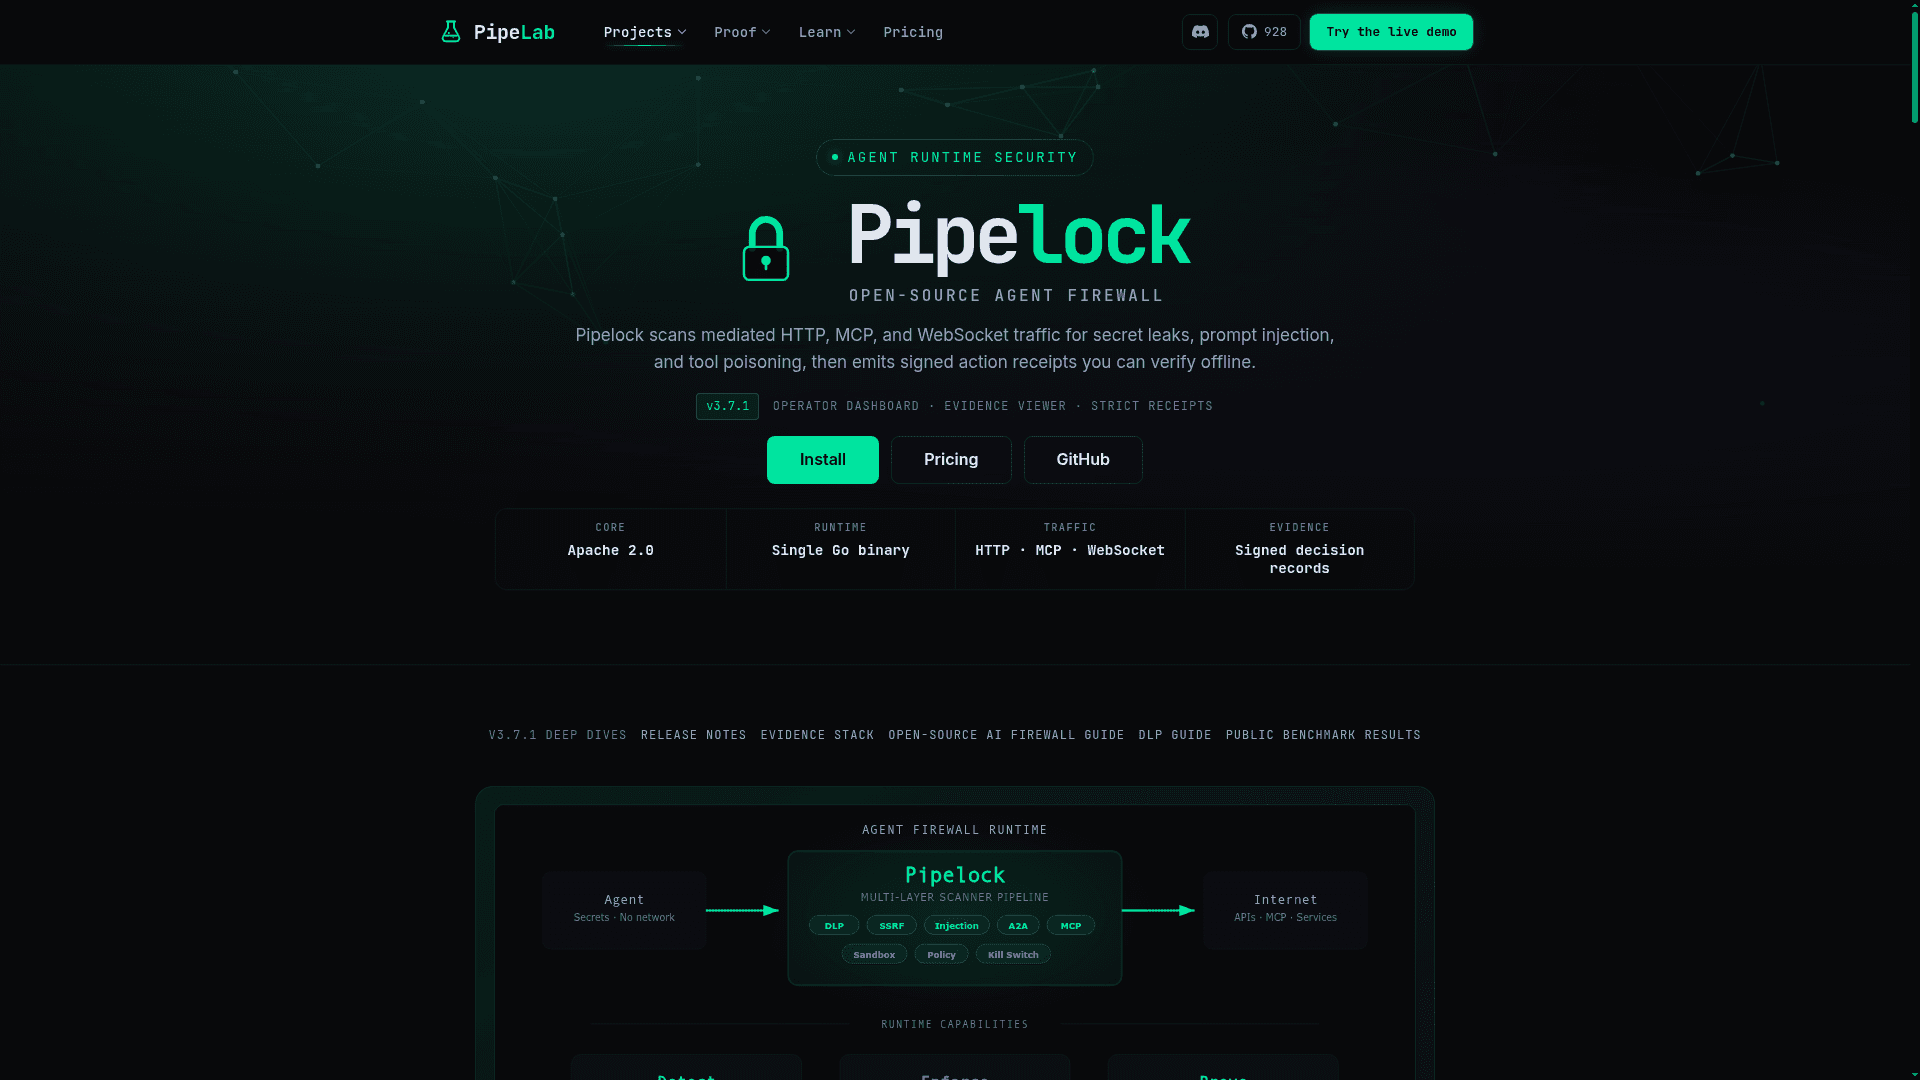
Open-source agent firewall that scans mediated HTTP, MCP, A2A and WebSocket traffic for secret leaks, prompt injection and tool poisoning and emits signed action receipts.
At a Glance
Free Apache-2.0 licensed core firewall; run on as many agents as you want.
Engagement
Available On
Alternatives
Listed Nov 2026
About Pipelock
Pipelock is an open-source agent firewall built by PipeLab. It sits between an AI agent and the network as a local proxy, scanning mediated HTTP, WebSocket, MCP and A2A traffic for secret exfiltration, prompt injection, SSRF and tool poisoning. It ships as a single Go binary with an Apache 2.0 core, and the site lists v3.7.1 as the current release.
What It Is
Pipelock is an egress and MCP security control for agents that hold credentials and have shell or API access. The agent keeps its keys, and Pipelock inspects the traffic crossing the boundary. Enforcement applies to traffic routed through its proxy, MCP wrapper, sandbox or containment setup; a direct network path around it must be prevented by routing or containment.
It works in three modes: strict (allowlist-only), balanced (the default) and audit. Mediated enforcement paths fail closed, so timeouts, parse errors and malformed messages are blocked rather than passed.
How the Scanning Works
URL scanning follows a fixed order: preflight checks, destination policy, credential and DLP checks, then DNS resolution, so secrets are caught before a DNS lookup occurs. The docs list 65 built-in DLP patterns and 34 response-injection patterns with multi-pass normalization.
For MCP, it wraps stdio servers or bridges to HTTP servers, scans tool arguments and responses, detects tool poisoning and mid-session description changes, and applies tool policy and chain detection. Optional controls include a seven-source kill switch, adaptive per-session enforcement, a Filesystem Sentinel, Browser Shield, and process containment using Landlock, seccomp and network namespaces on Linux or sandbox-exec on macOS.
Evidence and Receipts
Pipelock emits Ed25519-signed action receipts and a hash-chained flight recorder. Receipts can be checked offline with pipelock verify-receipt, and a free evidence viewer renders a recorded session as an HTML report. pipelock assess combines attack simulation, config scoring, install verification and discovery into signed evidence bundles. Verifier implementations exist in Go, TypeScript, Rust and Python.
Setup Path
Install from source with Go, or via Docker, Helm (OCI), Homebrew or a release binary. pipelock claude setup wires Claude Code through the proxy, and pipelock mcp proxy wraps a stdio MCP server. Integration guides cover Cursor, VS Code, JetBrains, Zed, Codex CLI, Cline, OpenCode, LangGraph, CrewAI, Google ADK and AutoGen. A GitHub Action can scan diffs in CI. Paid Pro and Enterprise tiers add multi-agent profiles, a dashboard and a fleet control plane.
Community Discussions
Be the first to start a conversation about Pipelock
Share your experience with Pipelock, ask questions, or help others learn from your insights.
Pricing
Community (Open Source Core)
Free Apache-2.0 licensed core firewall; run on as many agents as you want.
- Apache 2.0 core
- Scanning, detection, and enforcement controls in the open-source binary
- Single Go binary
- HTTP, MCP, WebSocket traffic
- Signed action receipts
Capabilities
Key Features
- Ordered URL scanner pipeline with DLP before DNS
- 65 built-in DLP patterns with encoding-aware inspection
- Response scanning for prompt injection
- MCP proxy with tool poisoning and rug-pull detection
- MCP tool policy and tool-call chain detection
- WebSocket and A2A traffic inspection
- SSRF and DNS rebinding protection
- Signed action receipts verifiable offline
- Hash-chained flight recorder
- Seven-source kill switch
- Adaptive per-session enforcement
- Process sandbox and host containment
- Browser Shield and media policy
- Canary tokens and skill-file scanning
- Signed community rule bundles
- Security assessment with signed evidence bundles
- GitHub Action for diff scanning
- Prometheus metrics and SIEM event emission
Integrations
Demo Video