
RLS Watch
Weekly read-only security checks for AI-built apps that flag exposed keys, open Supabase tables, and public files, with fix prompts for Lovable and Cursor.
At a Glance
One free credit on a new account for a full report after verifying ownership of the app.
Engagement
Available On
Alternatives
Listed Nov 2026
About RLS Watch
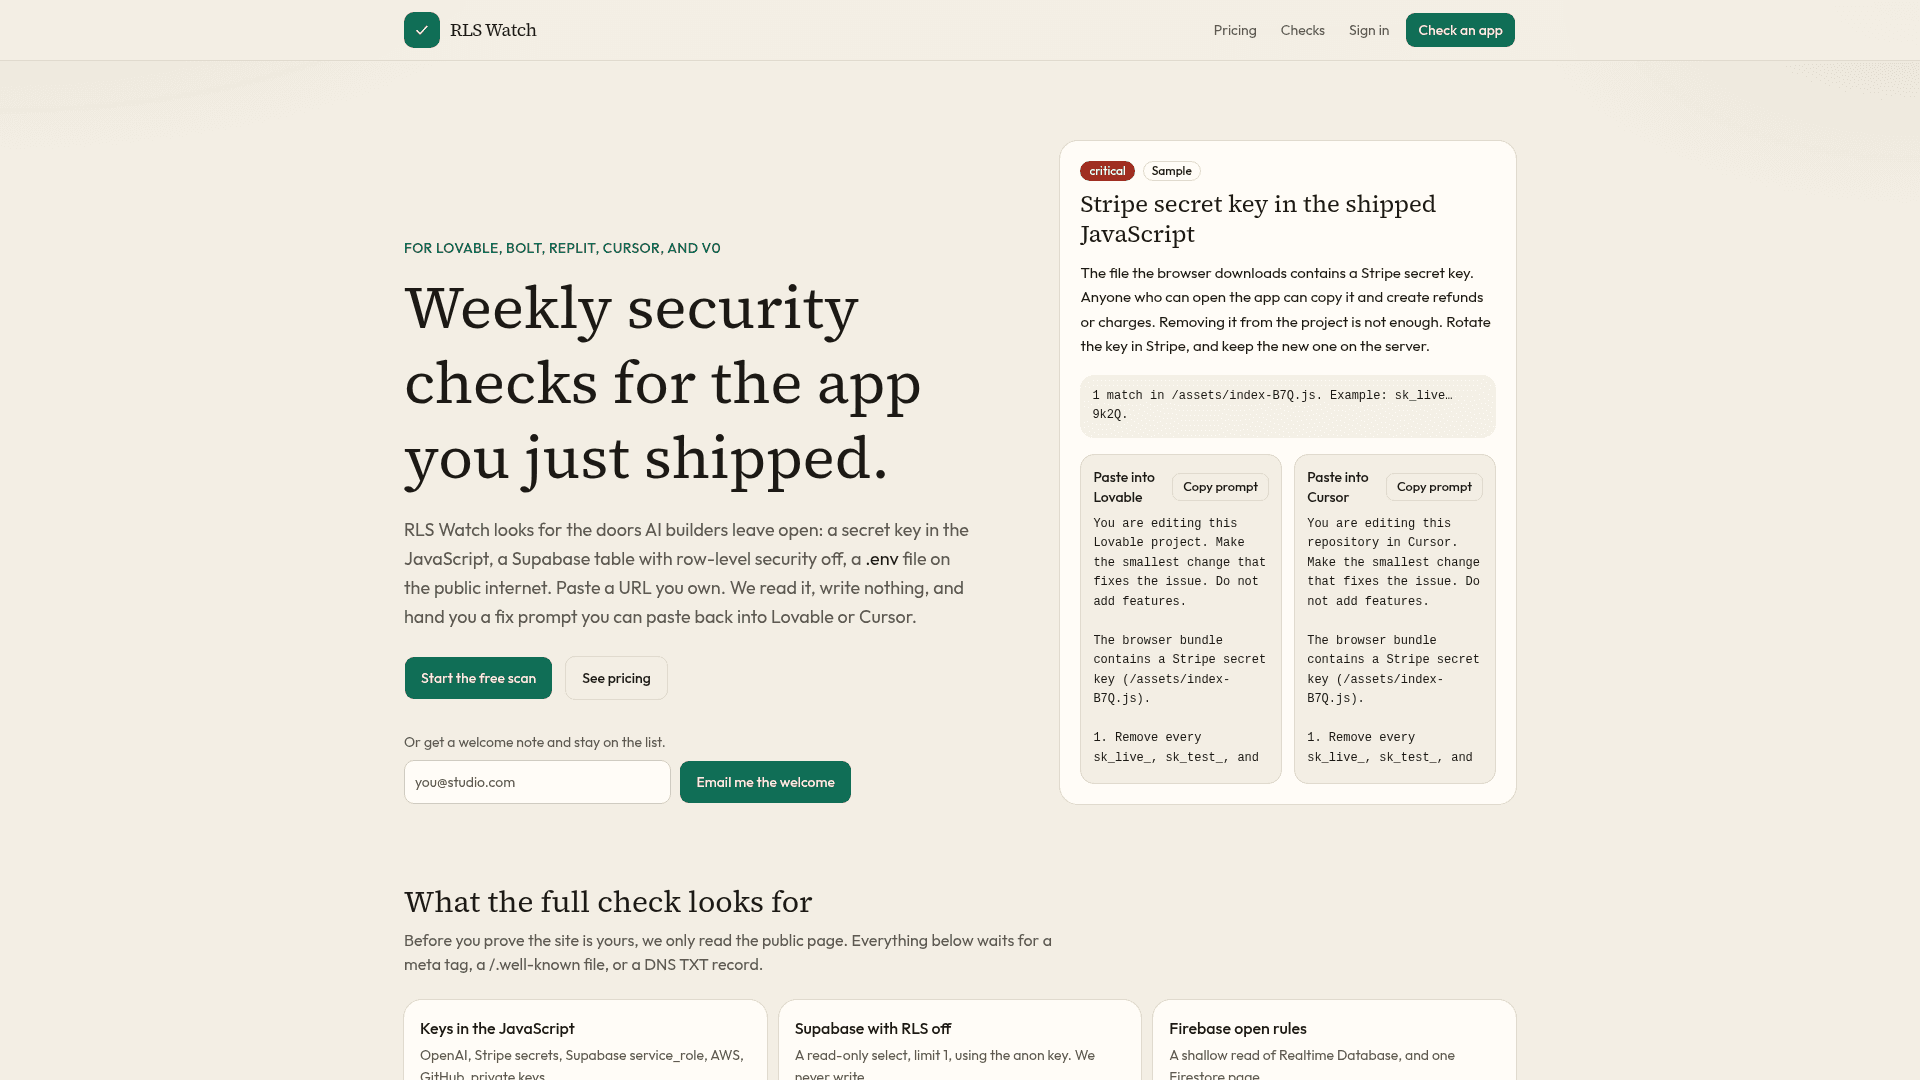
RLS Watch is a web service that runs security checks on apps built with AI builders such as Lovable, Bolt, Replit, Cursor, and v0. Users submit a URL they own, and the service reads it without writing anything, then returns a plain-English report with a fix prompt that can be pasted back into the builder.
What It Is
RLS Watch is a security scanner aimed at apps shipped quickly with AI coding tools. It looks for common exposures: secret keys in client JavaScript, Supabase tables with row-level security disabled, and public .env files.
How the Checks Work
Before ownership is proven, only a single passive read of the public page is made. After the user claims the app by ticking an ownership box and publishing a token (a meta tag, a /.well-known file, or a DNS TXT record), the full check runs. It remains read-only, with no logins, form posts, or database writes.
The full check covers:
- Keys in JavaScript, including OpenAI, Stripe secrets, Supabase service_role, AWS, GitHub, and private keys
- Supabase RLS, using a read-only select with limit 1 via the anon key
- Firebase open rules, via a shallow Realtime Database read and one Firestore page
- Public .env and .git files
- Open CORS, where a foreign Origin is reflected
- Missing security headers and mixed content
Reports and Fix Prompts
Each finding includes a severity, an explanation, evidence such as the file and a masked key, and ready-to-paste prompts for Lovable and Cursor that ask for the smallest change that fixes the issue. A weekly Monday job can rerun checks on verified apps, and email digests list what is new and what has cleared.
Community Discussions
Be the first to start a conversation about RLS Watch
Share your experience with RLS Watch, ask questions, or help others learn from your insights.
Pricing
First scan
One free credit on a new account for a full report after verifying ownership of the app.
- One credit on the new account
- Full report after you prove the app is yours
- Plain English, plus a fix prompt
Single scan
One additional full check for any verified app.
- One more full check, any verified app
- Use it the day you ship, or save it
- The Monday job can spend it
10-scan pack
Ten full checks for up to 10 apps on one account.
- Ten full checks
- Up to 10 apps on one account
- Email when a report changes
Capabilities
Key Features
- Weekly automated security checks
- Detects secret keys in shipped JavaScript
- Supabase row-level security check
- Firebase open rules check
- Public .env and .git exposure detection
- Open CORS detection
- Security headers and mixed content checks
- Copy-paste fix prompts for Lovable and Cursor
- Domain ownership verification via meta tag, /.well-known file, or DNS TXT
- Email digest when reports change
- Read-only scanning