
xss-audit
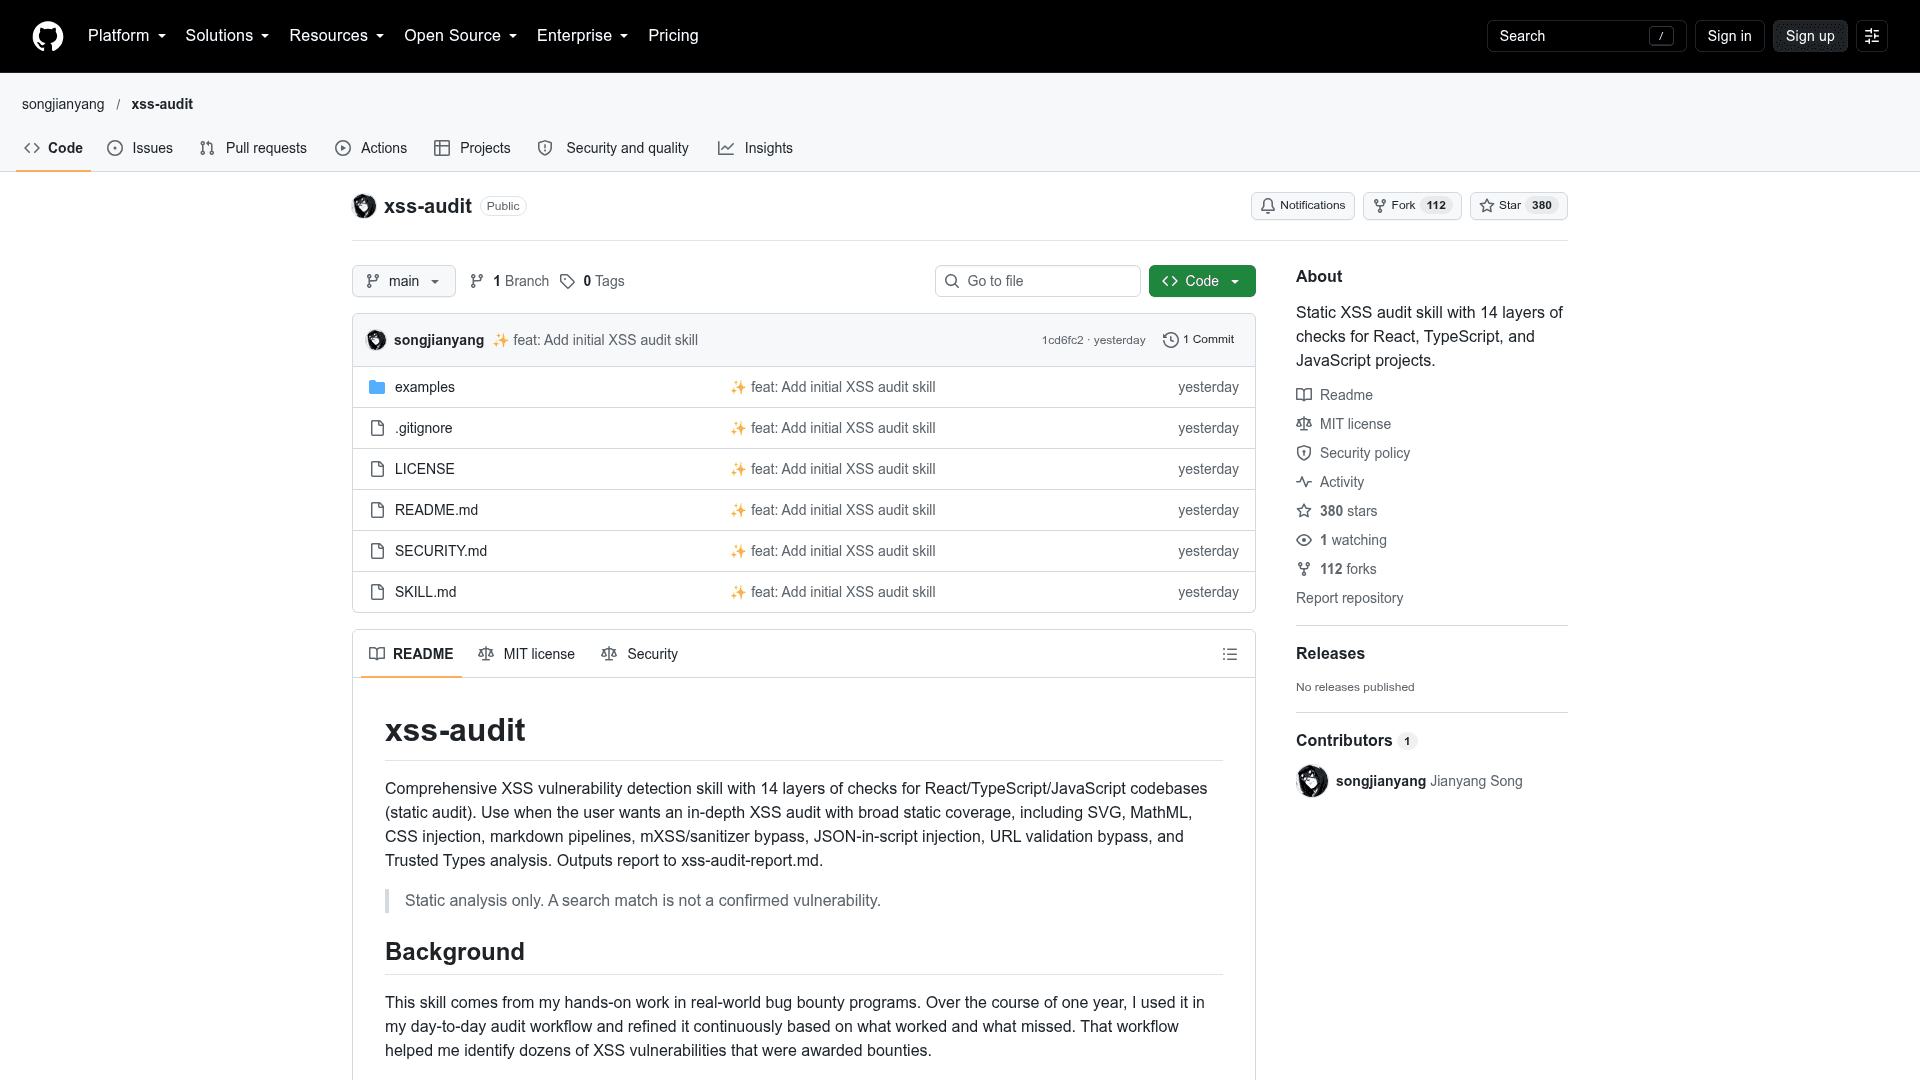
A static XSS audit agent skill with 14 layers of checks for React, TypeScript, and JavaScript codebases that writes a Markdown report.
At a Glance
xss-audit skill released under the MIT License; free to use, copy, modify and distribute.
Engagement
Available On
Listed Oct 2026
About xss-audit
xss-audit is an agent skill published by GitHub user songjianyang for in-depth static cross-site scripting audits of React, TypeScript, and JavaScript codebases. It is installed by copying its SKILL.md into an agent's skills directory and is invoked with a slash command (or $ syntax) optionally followed by a path. It writes its findings to xss-audit-report.md.
What It Is
xss-audit is a review procedure packaged as an agent skill rather than a standalone scanner. The author says it comes from real-world bug bounty work and was refined over a year of audits. The README states that it performs static analysis only and that a search match is not a confirmed vulnerability.
The 14 Review Layers
The layers cover DOM and HTML injection sinks, attributes and event handlers, URL and navigation validation, JSON-in-script injection, props spreading and gadget components, untrusted sources and messaging (postMessage, BroadcastChannel, storage), prototype pollution chains, and JavaScript execution sinks. They also cover CSS injection, SVG/MathML/XML namespace issues, Markdown and sanitizer (mXSS) handling, framework trust hooks (Vue, Angular, Svelte, Lit), Trusted Types and CSP, and template or binding injection in frameworks such as KnockoutJS, Alpine.js, AngularJS, Ember, and Handlebars.
Report Output
The report lists audited paths, exclusions, and unread files, then an executive summary with severity counts and manual-review counts. Findings are split into high, medium, and low severity, with a separate manual-review section for unconfirmed data flows. Each finding includes file and line, source, sink, data flow, vulnerable code, a fix recommendation, confidence, verification status, and reproduction notes that distinguish theoretical steps from executed ones. A per-layer summary separates pattern matches from confirmed vulnerabilities. A fictional sample report is included.
Limitations and Use
The README notes that static analysis can produce false positives and false negatives, and that no coverage is guaranteed. Reports may contain sensitive paths, source code, or credentials and should be sanitized before sharing. It should be used only on code you own or have permission to assess.
Community Discussions
Be the first to start a conversation about xss-audit
Share your experience with xss-audit, ask questions, or help others learn from your insights.
Pricing
Open Source (MIT)
xss-audit skill released under the MIT License; free to use, copy, modify and distribute.
- 14 layers of static XSS checks for React/TypeScript/JavaScript codebases
- Writes report to xss-audit-report.md
- MIT licensed
Capabilities
Key Features
- 14-layer static XSS audit
- DOM and HTML injection sink checks
- URL validation and navigation bypass analysis
- JSON-in-script breakout detection
- Prototype pollution gadget chains
- SVG, MathML, and CSS injection checks
- Markdown, sanitizer, and mXSS analysis
- Trusted Types and CSP review
- Framework binding and template injection checks
- Markdown report with severity levels and manual-review section